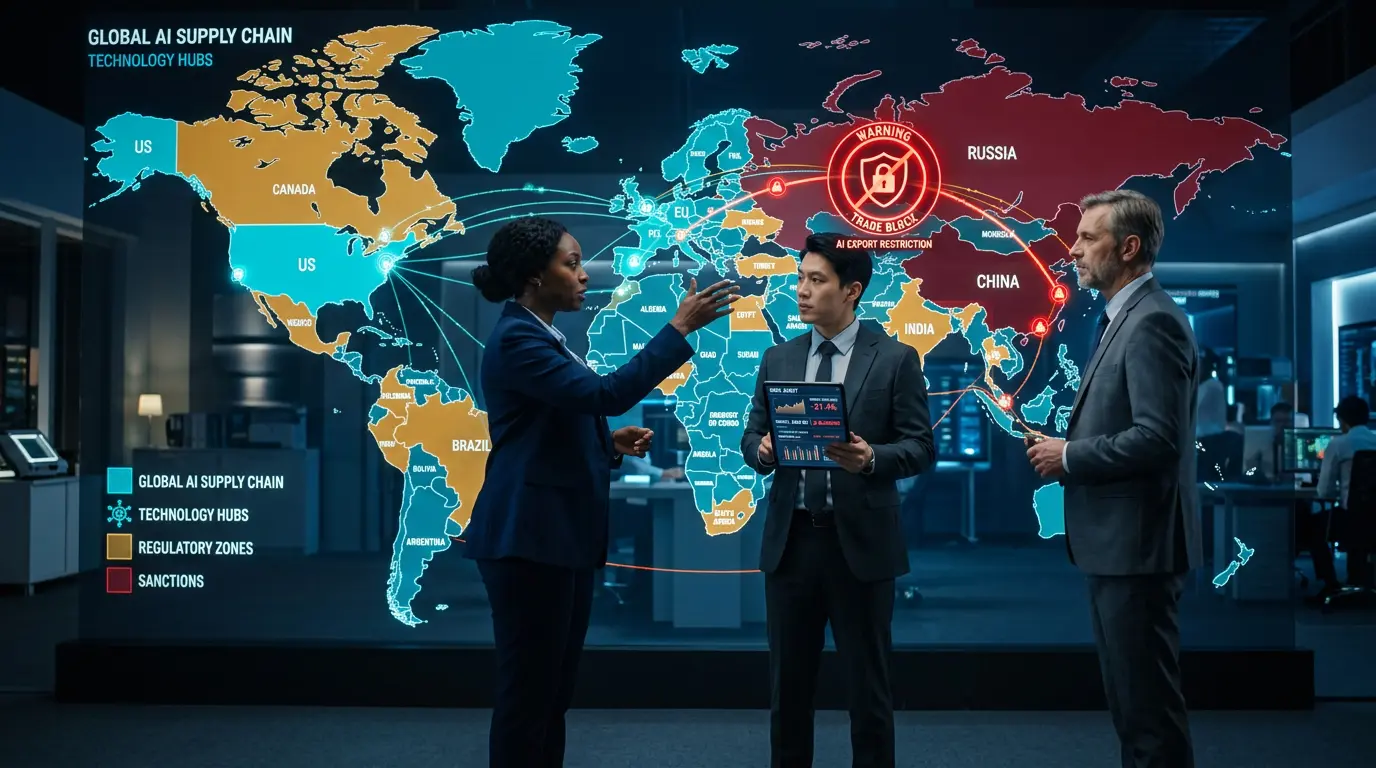
🌍 AI Has Become a Geopolitical Weapon, a Sanctions Target, and the Hardest Supply Chain Risk to Manage in 2026 — All at the Same Time: Export controls on AI chips, deepfake-powered influence operations, autonomous weapons systems, and digital sanctions are now reshaping how every organization plans its AI strategy. This comprehensive guide explains exactly how AI geopolitics works, which jurisdictions are at risk — including India’s rapidly evolving position under US export controls — what your supply chain exposure actually is, and the resilience framework that responsible organizations are building right now.
Last Updated: October 17, 2026
The geopolitics of artificial intelligence has moved from a topic discussed at think tanks and policy conferences to a pressing operational reality for technology leaders, supply chain managers, compliance professionals, and communications teams at organizations of every size. The same AI capabilities that are transforming healthcare, finance, logistics, and manufacturing have simultaneously become instruments of national power, targets of export control regimes, engines of industrial-scale disinformation, and flashpoints in a broader strategic competition that has fundamentally changed the global technology landscape. Organizations that were building AI infrastructure three years ago with the assumption that AI tools, chips, and services were globally available commodity inputs are now discovering that geopolitical risk — across dimensions that range from chip compliance to cognitive warfare — has become as important a variable in AI architecture decisions as cost, capability, and latency.
The scale of this transformation is difficult to overstate. The United States has imposed successive rounds of semiconductor export controls targeting China’s AI development capacity — restrictions that now extend to over 40,000 line items of controlled technology and have been designed to prevent China from acquiring the chips needed to train frontier AI models. China has responded with export controls on rare earth minerals and processing technology critical to global electronics supply chains, has accelerated domestic AI chip development programs that are closing the capability gap faster than many Western analysts predicted, and has deployed AI-enabled systems across military, surveillance, information warfare, and economic applications that have alarmed allies and partners globally. Russia’s invasion of Ukraine produced the world’s first AI-drone war at scale, while simultaneously demonstrating how synthetic media and deepfake operations can reshape battlefield perception and democratic discourse with equal force. The information warfare dimension of AI geopolitics is no longer a theoretical concern — it is active, industrialized, and accelerating.
This guide provides a comprehensive, practical examination of AI geopolitics and global sanctions in 2026 — covering the information warfare threat landscape, the autonomous weapons arms race, the major export control regimes, supply chain compliance obligations, the India/Nvidia export controls nexus, the 2026 regulatory change log, and the resilience framework that organizations need to navigate a technology landscape where geopolitical disruption has become a baseline planning assumption rather than a tail risk. Whether you are a CTO evaluating AI infrastructure decisions, a compliance officer navigating export control requirements, a communications director managing AI-enabled disinformation risk, or a board member trying to understand why your organization’s AI strategy now requires geopolitical scenario planning, this guide gives you the analytical framework and practical guidance to engage with this reality systematically. The technical dimensions of AI resilience connect to our guide on Sovereign AI and Resilience — and the governance principles for managing these risks connect to our guide to AI Governance Explained.
📖 New to AI terminology? Visit the AI Buzz AI Glossary — 100+ essential AI terms explained in plain English, each linking to a full in-depth guide.
🧠 1. The New Information Warfare — How AI Has Industrialized Influence Operations
Artificial intelligence has not merely improved information warfare — it has industrialized it. The asymmetric advantage that state-sponsored influence operations have always sought — the ability to produce and distribute compelling narratives faster than target populations can evaluate them — has been dramatically amplified by AI-generated content at scale. What previously required large teams of human operatives, native language fluency, and significant production budgets can now be accomplished with a small team, an AI content pipeline, and a distribution network built on social media automation. The barrier to entry for sophisticated influence operations has collapsed, and the number of actors capable of running them has multiplied accordingly.
Russia’s Storm-1516 network — the most extensively documented AI-augmented influence operation of the current period — demonstrated the operational template that subsequent actors have studied and adapted. Storm-1516 combined AI-generated synthetic news anchors presenting fabricated video reports, AI-translated content distributed simultaneously across multiple language markets, and coordinated social media amplification through bot networks that exploit platform recommendation algorithms to drive organic reach beyond the network’s own followers. The operation’s targeting of European audiences ahead of parliamentary elections in Germany, France, and Poland demonstrated the geographic precision with which AI-augmented influence operations can be deployed — and the speed with which synthetic content can achieve genuine circulation before platform moderation can respond.
China’s information warfare operations targeting Taiwan have added a further dimension to the threat model: long-horizon cognitive operations designed not to persuade immediately but to gradually erode confidence in democratic institutions, degrade trust in Taiwanese government communications, and create the perception of internal division that strategic planners assess as a prerequisite for successful coercion. AI-generated content in these operations has included synthetic testimonials from fabricated Taiwanese citizens, AI-dubbed versions of real Taiwanese officials’ speeches with altered content, and coordinated amplification of genuine internal Taiwanese political disputes in ways that make them appear more severe and representative than they actually are. The operational goal is not a single persuasive message but a sustained degradation of the information environment that makes accurate perception increasingly difficult for target populations. For organizations with operations, customers, or communications strategies in the Taiwan Strait region, this cognitive dimension of AI geopolitics creates specific reputational and operational risks that sit alongside — and interact with — the supply chain and export control risks that receive more attention in most business analyses.
Iran’s Deepfake Operations and the Global Template
Iran’s AI-enabled influence operations targeting the 2024 US election cycle — extensively documented by Microsoft’s Threat Intelligence team and subsequently confirmed by US intelligence assessments — established a template that has been widely studied and adapted. Iranian operators used AI-generated fake news websites, AI-produced video content featuring synthetic American personas, and AI-translated social media content targeting specific demographic groups within the United States to amplify existing social divisions and suppress civic engagement in communities assessed as politically influential. The sophistication of the operation was less in its technical production quality — which, while convincing, was not undetectable — than in its targeting precision: AI tools allowed Iranian operators to identify the specific communities, issues, and emotional triggers most likely to produce the amplification and division the operation sought.
The organizational implication of this threat model extends well beyond government and media institutions. Any organization that communicates publicly — through social media, press releases, executive statements, or investor communications — is a potential target for synthetic media operations that fabricate or distort those communications for adversarial purposes. A fabricated video of a CEO making inflammatory statements, a synthetic audio clip of an earnings call with altered financial disclosures, or AI-generated fake customer testimonials amplified through coordinated networks represent the commercial and reputational attack surface that AI-enabled information warfare has opened for the private sector. The connection between AI geopolitics and corporate communications security is direct and underappreciated in most enterprise risk assessments. Our guide to AI Deepfakes and Misinformation covers the detection and organizational response protocols in detail.
The Information Warfare Risk for Internal Communications
The deepfake proliferation makes media literacy a foundational organizational security skill in 2026 — as fundamental as phishing awareness has become over the past decade. Employees who cannot reliably distinguish synthetic media from authentic content are vulnerable to social engineering attacks that use deepfake video or audio of real executives or colleagues to authorize fraudulent transactions, extract sensitive information, or manipulate internal decision-making. The financial sector has documented a growing number of cases in which AI-generated video calls — impersonating CFOs, legal counsel, or auditors — were used to authorize wire transfers that resulted in significant losses. These attacks succeed not because of exceptional technical quality but because the target has no established verification protocol for authenticating video communications from people they believe they know.
At the organizational level, media literacy training for employees handling financial authorizations, sensitive communications, or executive instructions has become a security imperative rather than an optional enrichment activity. The training curriculum for this risk is different from traditional phishing awareness: it focuses on verification protocols (out-of-band confirmation for financial instructions received through any digital channel), recognition of deepfake artifacts (unnatural blinking patterns, audio-visual synchronization failures, background inconsistencies), and the organizational culture of skepticism toward unexpected requests that creates the friction deepfake attacks depend on eliminating. Organizations that have not yet integrated AI-generated synthetic media awareness into their security training programs have a gap that the current threat environment makes urgent to close.
🎭 2. The Deepfake Crisis — How Synthetic Media Is Weaponizing Democracy
The deepfake crisis of 2026 is not primarily a technology crisis — it is an epistemological crisis. The underlying technical challenge of distinguishing synthetic from authentic media is real and difficult, but the deeper problem is what information security researchers call the “liar’s dividend”: the phenomenon whereby the existence of convincing deepfake technology provides plausible deniability for any video or audio evidence, regardless of whether that specific piece of evidence is actually synthetic. A politician caught on authentic video making a damaging statement can now credibly claim the video is a deepfake. A corporate executive captured in an authentic recording making incriminating disclosures can now mount a deepfake defense in litigation. The liar’s dividend degrades accountability across every domain where video and audio evidence has historically provided a reliable factual foundation — law, journalism, politics, and corporate governance — and it does this damage whether or not any specific deepfake is actually deployed.
The electoral implications of deepfake proliferation have been most extensively documented in the 2024 election cycle, when deepfake content targeting candidates and voters appeared in elections across four continents. The Slovakian parliamentary election of 2023 — where an AI-generated audio clip fabricated a conversation between a candidate and a journalist discussing vote-buying — provided an early template that subsequent electoral influence operations have refined. The Bangladesh, Pakistan, and Indonesian elections of 2024 all featured deepfake content of varying sophistication targeting political figures, with platform moderation consistently lagging the distribution velocity of synthetic content by enough hours that the initial viral spread — which shapes audience perception most powerfully — occurred before fact-checking corrections reached comparable audiences. The WEF Global Risks Report 2026 ranked AI-enabled mis- and disinformation among the top short-term global risks — one of the few risks rated severe over both the two-year and ten-year horizons.
The C2PA Standard and the Authenticity Infrastructure Challenge
The technical response to the deepfake crisis that has attracted the broadest industry support is the Coalition for Content Provenance and Authenticity (C2PA) standard — a cryptographic content credentials framework that embeds verifiable metadata in media files at the point of creation, allowing downstream consumers to verify where a piece of content originated, what camera or AI tool created it, and whether it has been altered since creation. The C2PA standard has been adopted by major camera manufacturers including Sony, Nikon, and Canon, by major AI image generation platforms including Adobe Firefly and the DALL-E API, and by social platforms including LinkedIn and YouTube as a signal in their content moderation workflows. Microsoft has integrated C2PA content credentials into its Bing Image Creator and is expanding the implementation across its AI content creation tools.
The limitation of the C2PA approach is that it provides authenticity assurance for content created within the compliant ecosystem — cameras, tools, and platforms that have implemented the standard — but provides no protection against content created with tools that have not implemented C2PA, content that has been captured from a screen rather than exported from a C2PA-compliant tool, or content where the provenance chain has been deliberately broken by an adversary with the technical capability to strip metadata. For state-sponsored information warfare operations, which have access to significant technical resources and specifically target the gaps in authentication infrastructure, C2PA compliance provides meaningful friction rather than reliable protection. This limitation does not make C2PA unimportant — meaningful friction against influence operations is valuable even if not absolute — but it does mean that organizational content authentication strategies must layer C2PA verification with other verification protocols rather than treating it as a complete solution.
EU AI Act Article 50 and the Disclosure Obligation
The EU AI Act’s Article 50 — which took effect in August 2026 — imposes mandatory disclosure obligations on operators of AI systems that generate synthetic audio, video, or image content. Systems that produce deepfake content must clearly label that content as AI-generated in a manner that is “machine-readable and detectable” — a technical requirement that operationalizes the content authenticity principle at the regulatory level. The Article 50 obligation applies to any AI system deployed to EU users that generates synthetic media, regardless of where the system’s operator is headquartered — giving the EU AI Act extraterritorial reach over the global synthetic media ecosystem in a manner similar to GDPR’s extraterritorial application to data processing affecting EU residents.
The compliance implications of Article 50 for organizations that produce or distribute AI-generated content in European markets are direct: any content produced using AI image generation, AI video synthesis, or AI voice cloning tools must include disclosure that is technically verifiable, not merely a written disclaimer buried in terms of service. The enforcement risk is concentrated on organizations that produce AI-generated advertising, AI-generated training materials, or AI-generated news content for European audiences without implementing the required disclosure mechanism — a compliance gap that many marketing and communications teams have not yet addressed. For the broader synthetic media authenticity framework, Article 50’s regulatory teeth provide the enforcement mechanism that voluntary industry standards like C2PA alone cannot supply.
🤖 3. The Autonomous Weapons Arms Race — The New “Mutually Automated Destruction”
The Ukraine conflict has produced the world’s first AI-drone war at scale — a laboratory for autonomous weapons development whose lessons are reshaping military doctrine in every major power simultaneously. Ukraine established a dedicated Unmanned System Forces unit in February 2024 and planned to manufacture four million drones in 2025 alone, deploying AI-augmented systems that range from first-person view drones with AI-assisted targeting to autonomous loitering munitions capable of selecting and engaging targets without real-time human control when GPS and communications links are severed by electronic warfare. The battlefield saturation of AI-enabled autonomous systems has produced doctrinal, legal, and ethical challenges that the international governance frameworks governing the laws of armed conflict were not designed to address — and that the pace of military AI development is outrunning the capacity of international institutions to resolve. The AI in Defense and Military guide covers the strategic and ethical dimensions of this transformation in detail.
Russia’s military AI program has pursued a parallel track — deploying AI-augmented autonomous systems specifically designed to operate in environments where human communications links have been severed. In July 2026, a Russian drone struck a gas station in Zaporizhzhia killing three Ukrainian civilians — a strike that subsequent analysis indicated the drone’s AI had executed autonomously after losing its operator link, selecting a target based on its onboard recognition systems without human confirmation. This incident — documented by Help Net Security and subsequently verified by Ukrainian military investigators — represents the first confirmed instance of an autonomous AI weapons system causing civilian casualties in circumstances where no human made the final targeting decision. The legal and ethical vacuum this creates — which international humanitarian law scholar Hugo Slim described as “a crime without a clear criminal” — illustrates why the autonomous weapons governance debate is no longer a theoretical future concern but an immediate accountability crisis.
The US-China Military AI Competition
The United States Department of Defense had over 800 active AI-related projects in 2024 and requested $1.8 billion in AI funding, with Project Maven and Project Artemis — AI-resistant drones developed jointly with Ukraine — among the primary programs. China is pursuing what its military doctrine calls “intelligentized warfare” — the systematic integration of AI across all combat domains including land, sea, air, space, and cyber — with military AI spending exceeding $1.6 billion annually and accelerating. The US-China military AI competition creates a strategic dynamic that bears comparison to the nuclear arms race: each side’s development of autonomous weapons capabilities creates pressure on the other to accelerate its own development, compress human decision timelines, and reduce the oversight mechanisms that create operational friction but also create the space for error correction and escalation control.
The arms race dynamic in autonomous weapons creates specific risks for the commercial and civilian AI ecosystem that most enterprise risk assessments have not yet incorporated. Military AI development programs draw on the same foundational model architectures, training methodologies, and hardware infrastructure as commercial AI — creating a technology transfer pathway between commercial AI development and military applications that export controls, procurement regulations, and corporate AI ethics policies are all attempting to manage simultaneously. Organizations that provide AI infrastructure, AI development tools, or AI consulting services face the growing possibility that their commercial work has military applications they did not intend and may not have sanctioned — a dual-use challenge that is becoming increasingly difficult to navigate as AI capability improves and as the boundary between commercial and military AI applications narrows.
The International Governance Vacuum
The international governance framework for autonomous weapons is characterized by urgency without resolution. The United Nations’ Group of Governmental Experts on Lethal Autonomous Weapons Systems has been meeting since 2014 without producing a binding treaty, as major military AI powers — including the United States, Russia, China, and Israel — have resisted any framework that would constrain their autonomous weapons development programs. The 2023 Political Declaration on Responsible Military Use of AI and Autonomy — signed by the United States and endorsed by a coalition of allies — establishes non-binding principles for human oversight in military AI but explicitly does not prohibit autonomous weapons systems, leaving the most consequential governance question unresolved. The July 2026 Zaporizhzhia incident has intensified diplomatic pressure for a binding framework, but the fundamental tension between military advantage and governance constraint shows no signs of resolution at the speed the technology is advancing.
📊 4. The 2026 Export Control Landscape: What Changed and What It Means
The AI export control environment shifted materially in 2026. The changes did not represent a relaxation of strategic intent — the US government’s goal of limiting adversary access to frontier AI compute remains unchanged — but the specific policy mechanisms evolved in ways that create new compliance obligations and new planning complexity for organizations across the supply chain. Understanding the 2026 state of the export control landscape is essential because compliance requirements from even six months ago may no longer accurately reflect current obligations. The Bureau of Industry and Security (BIS) continues to be the primary US enforcement body, and its enforcement posture is intensifying: Congress approved a 23% increase in BIS’s Fiscal Year 2026 budget, with several million dollars specifically earmarked for semiconductor-related enforcement actions.
The most significant development in early 2026 was the January 15, 2026 BIS final rule revising the export license review policy for advanced computing semiconductors destined for China and Macau. The previous regime operated under a broad “presumption of denial” — meaning applications to export advanced AI chips to China faced an automatic presumption of rejection. The January 2026 rule replaced this with a case-by-case review system for chips below specific performance thresholds: chips with a Total Processing Performance (TPP) below 21,000 and DRAM bandwidth under 6,500 GB/s — including the NVIDIA H200 and AMD MI325X — are now eligible for case-by-case review instead of automatic denial. This is not a liberalization. The conditions attached to case-by-case approval are substantial: a 25% tariff, a 50% volume cap relative to US domestic shipments, mandatory third-party testing conducted in the United States before shipment, and full know-your-customer (KYC) compliance documentation. Re-export licenses — covering chips shipped from the US to a third country and then onward to China — remain under a presumption of denial, closing the third-country circumvention routes that had partially undermined earlier control rounds.
2026 Compliance Reality: In 2026, AI export compliance is not a trade lawyer’s problem. It is a procurement problem, a vendor management problem, and a board-level risk problem. The January 2026 BIS rule, the May 31, 2026 guidance reaffirming November 2023 licensing requirements, and the pending Affiliates Rule resumption together created layered compliance obligations for every organization in the AI chip supply chain — not just chip manufacturers and exporters.
BIS issued further guidance on May 31, 2026, confirming that the licensing requirements established in November 2023 remain fully in effect for advanced computing exports to Country Group D:5 destinations including China, Russia, and Iran. In parallel, BIS rescinded the AI Diffusion Rule that had created significant compliance uncertainty for data center operators — clarifying that bona fide data center operators acting consistently with the Export Administration Regulations may continue using, storing, and servicing advanced computing items without interruption pending further notice. This clarification was welcomed by cloud and data center operators, but BIS provided no timeline for future guidance, leaving meaningful regulatory uncertainty in place for organizations making long-term infrastructure commitments.
The BIS Affiliates Rule — a regulation extending export control restrictions to foreign entities at least 50% owned (directly or indirectly) by entities on BIS’s Entity List, Military End-User List, or OFAC’s SDN list — was suspended on November 10, 2025 for a period of one year. Organizations should treat the November 2026 deadline as a compliance planning milestone: the rule is likely to resume in some form, and data center operators and AI hardware purchasers with complex ownership structures need to complete their beneficial ownership analysis before that deadline. In Europe, draft AI export control options began circulating among EU member states in early 2026, with proposed thresholds targeting AI accelerators exceeding roughly 300 TFLOPS — a development that would affect European organizations currently operating outside the US control architecture.
| Jurisdiction | Key Control (2026) | What It Restricts | Business Impact |
|---|---|---|---|
| United States (BIS/EAR) | AI chip export controls — Jan 2026 case-by-case rule + May 2026 guidance | Advanced GPU/AI chip exports to China, Macau, and restricted destinations; re-exports remain presumed denied | 🔴 Procurement + supply chain compliance; KYC documentation; mandatory US testing |
| United States (OFAC) | SDN list + comprehensive sanctions programs | AI services, cloud access, and financial transactions with sanctioned entities and jurisdictions | 🔴 Software + API service risk; customer screening obligation |
| European Union | Regulation (EU) 2021/821 — updated Sept 2025; draft AI-specific controls circulating 2026; EU AI Act Article 50 active Aug 2026 | Dual-use AI technology; cyber-surveillance tools; proposed controls on accelerators above 300 TFLOPS; mandatory synthetic media disclosure | 🟠 EU-based operations; member state enforcement with criminal exposure |
| United Kingdom | Export Control Order — post-Brexit independent list broadly aligned with EU | AI components classified as dual-use technology; diverging from EU in some AI-specific categories | 🟠 UK-based operations; criminal prosecution for violations |
| China | Data export restrictions + rare earth export controls (2026 escalation) | Cross-border AI data flows; rare earth minerals and processing technology critical to chip manufacturing | 🔴 Any business with China operations or rare earth supply chain exposure |
The Entity List dimension of this landscape deserves specific attention for organizations in the AI supply chain. The US Entity List now contains over 600 Chinese technology companies and affiliates — creating significant compliance complexity for any business sourcing AI components, contracting AI services, or building products that incorporate AI hardware or software with Chinese-origin components. Export control violations carry penalties of up to $1 million per violation or twice the transaction value — whichever is greater — under the Export Administration Regulations. In January 2026, BIS entered into a $1.5 million settlement with a European company regarding the unlawful in-country transfer of semiconductor manufacturing items to a foundry facility on the Entity List by the European company’s China-based subsidiary — a real enforcement action that demonstrates the cross-border reach of US controls. Chatham House research published in April 2026 concludes that export controls alone will not prevent adversaries from developing advanced AI due to enforcement gaps, smuggling, and rapid technical adaptation — suggesting that compliance programs must be paired with resilience strategies rather than treating controls as a complete solution.
🏢 5. What This Means for Your Business: The Compliance Obligations Most Companies Miss
Most organizations that have begun to grapple with AI export compliance have focused on the obvious cases: chip manufacturers, cloud providers, and organizations with direct commercial relationships in China. The more challenging and more commonly overlooked compliance exposures arise in organizations that consider themselves downstream consumers of AI technology rather than participants in the AI supply chain — a framing that is increasingly incorrect and increasingly risky. The full landscape of AI regulation in 2026 makes clear that compliance obligations extend far beyond traditional technology exporters to encompass virtually any organization that procures, deploys, or sells AI-enabled products or services internationally. The BIS’s expanded enforcement mandate and increased FY2026 budget make this not a theoretical concern but an active enforcement priority.
The Downstream Compliance Reality: Most organizations that will receive BIS enforcement attention in 2026 and 2027 are not chip manufacturers. They are data center operators, cloud service customers, SaaS providers, and AI tool resellers who assumed they were outside the export control perimeter — and discovered they were not.
The Supply Chain Problem — You May Be Non-Compliant Without Knowing It
Most businesses that use AI tools, cloud AI platforms, or AI-enabled hardware do not know the origin of the chips powering those services — and in 2026, that knowledge gap creates genuine compliance exposure. If your cloud AI provider uses restricted components in a jurisdiction-violating configuration, or if a vendor in your AI hardware supply chain has a beneficial ownership connection to an Entity List company, you may have indirect exposure even though you are not the exporter of record. The “know your customer” and “know your supplier” obligations under BIS’s Export Administration Regulations apply downstream as well as upstream — the obligation does not end at your direct vendor relationship but extends to what you can reasonably know about your supply chain’s ultimate provenance.
The practical action this requires is more specific than simply asking vendors about their compliance programs. It means requesting chip provenance documentation from AI infrastructure vendors as a standard element of vendor due diligence — including which specific chip models power the AI services you consume, where those chips were manufactured, and whether the vendor has completed Entity List screening for their own supply chain. This documentation request should be a standard element of every AI vendor contract and renewal negotiation. Our AI Audit Checklist provides the complete framework for structuring these vendor assessments, including the specific questions that surface export control exposure in AI supply chains.
The SaaS and API Risk — Selling AI Services Across Borders
If your business provides AI-powered SaaS products or API services, exporting those services to restricted countries or sanctioned entities is a violation — even if no physical product crosses a border. Software-as-a-service is explicitly covered under US export control regulations: providing access to controlled AI software through an API is legally equivalent to exporting that software for export control purposes. A single API call from a sanctioned jurisdiction can constitute an export violation if the underlying AI software is subject to export controls and the end-user is in a restricted destination. The geographic indirection of cloud service access — customers routing requests through VPNs, third-country proxies, or distributed infrastructure — does not eliminate the compliance obligation; it creates a due diligence requirement to implement geo-restriction controls and customer screening that makes the service provider’s best-effort compliance demonstrable.
Organizations that provide AI-powered services internationally should implement a geo-restriction control layer that blocks service access from comprehensively sanctioned jurisdictions (Iran, North Korea, Cuba, Syria, and Russia under various OFAC program categories), maintain a customer screening process against the OFAC SDN list and the BIS Entity List for enterprise customers, and document these controls as evidence of good-faith compliance that reduces penalty exposure in enforcement scenarios. The absence of any screening or geo-restriction controls is the compliance posture that creates the highest enforcement risk — not because every API call from a restricted jurisdiction will be prosecuted, but because the documented absence of controls eliminates the good-faith compliance defense that typically results in reduced penalties rather than maximum enforcement actions.
The Talent and Research Risk — Hiring and Collaboration
A compliance exposure that most technology organizations have not yet incorporated into their AI governance programs is the “deemed export” risk — the principle that sharing controlled AI technology with a foreign national inside the United States constitutes an export to that person’s country of citizenship, potentially requiring the same export license that a physical export would require. This applies to research collaborations, open-source AI contributions, hiring decisions, and any professional interaction where controlled AI technology — including certain AI software, model architecture documentation, and training methodologies — is shared with a national of a restricted country. US universities and research institutions with AI programs are facing growing deemed export compliance complexity as the scope of controlled AI technology expands, and corporate AI research teams face the same obligations when their work involves controlled technology categories.
The Information Warfare Risk — What AI Geopolitics Means for Internal Communications
The deepfake proliferation makes media literacy a foundational organizational security requirement in 2026 — as fundamental as phishing awareness has become over the past decade. Employees who cannot reliably distinguish synthetic media from authentic content are vulnerable to social engineering attacks that use deepfake video or audio of real executives or colleagues to authorize fraudulent transactions, extract sensitive information, or manipulate internal decision-making. The financial sector has documented a growing number of cases in which AI-generated video calls impersonating CFOs, legal counsel, or auditors were used to authorize wire transfers that resulted in significant losses — attacks that succeed not because of exceptional technical quality but because targets have no established verification protocol for authenticating video communications from people they believe they recognize.
At the organizational level, media literacy training for employees handling financial authorizations, sensitive communications, or executive instructions has become a security imperative rather than an optional enrichment activity. The training curriculum for this risk focuses on verification protocols (out-of-band confirmation for financial instructions received through any digital channel), recognition of deepfake artifacts (unnatural blinking patterns, audio-visual synchronization failures, background inconsistencies), and the organizational culture of skepticism toward unexpected requests that creates the friction deepfake attacks depend on eliminating. Organizations that have not yet integrated AI-generated synthetic media awareness into their security training programs — alongside their export compliance and vendor screening programs — have a gap that the current threat environment makes urgent to close.
| Business Activity | Export Control Risk | Action Required |
|---|---|---|
| Purchasing AI cloud services | ⚠️ Medium — chip provenance gap | Request vendor compliance documentation confirming Entity List screening and chip origin |
| Selling AI SaaS internationally | 🔴 High — service export rules | OFAC/Entity List screening before customer onboarding; geo-restriction controls for sanctioned jurisdictions |
| Hiring AI researchers | 🟠 Medium — deemed export risk | Legal review for nationals of restricted countries working on controlled AI technology |
| Open-source AI contributions | 🟠 Medium — deemed export risk | Contribution policy review with export control counsel; assess controlled technology scope |
| Using AI APIs in global products | 🔴 High — jurisdiction exposure | Geo-restriction implementation + customer screening protocol for all international deployments |
| Sourcing AI hardware | 🟠 Medium — supply chain risk | Chip provenance documentation + beneficial ownership screening for hardware vendors |
| Internal executive communications | 🟠 Medium — deepfake fraud risk | Out-of-band verification protocols for financial authorizations; synthetic media awareness training |
🗺️ 6. The AI Geopolitics Landscape: Six Major Risk Vectors
AI geopolitical risk is not a single, monolithic threat but a complex of distinct risk vectors that affect different organizations in different ways depending on their technology stack, geographic footprint, customer base, and supply chain structure. Understanding the distinct risk vectors allows organizations to assess their specific exposure rather than treating “AI geopolitical risk” as an undifferentiated concept that applies equally to everyone.
| Risk Vector | Description | Who Is Most Affected | Current Status (2026) |
|---|---|---|---|
| Semiconductor Export Controls | US and allied restrictions on advanced AI chip exports to China, Russia, and designated entities | Chip manufacturers, cloud providers, organizations with Chinese or Russian supply chain exposure | 🔴 Actively Enforced |
| AI Software and Model Restrictions | Restrictions on exports of AI software, model weights, and training technology to controlled jurisdictions | AI software developers, cloud AI service providers, organizations with multinational AI deployments | 🟠 Expanding Rapidly |
| Cloud Service Blocking | Restrictions on providing cloud AI services to sanctioned countries or entities; reciprocal blocking by China | Cloud service providers, organizations relying on cloud AI for international operations | 🔴 Actively Enforced |
| Data Localization Requirements | National requirements that AI training data, model weights, and inference outputs cannot leave national boundaries | Multinational organizations, AI SaaS providers, organizations using cross-border data flows | 🟠 Growing Significantly |
| Rare Earth and Materials Supply | Chinese export controls on rare earth elements and processing technology critical to semiconductor manufacturing | Semiconductor manufacturers, electronics supply chains, any organization dependent on semiconductor availability | 🟠 Active and Escalating |
| AI Standards Fragmentation | Diverging AI regulatory frameworks, certification requirements, and technical standards across US, EU, and China | Global technology companies, AI developers deploying across multiple regulatory jurisdictions | 🟡 Developing Rapidly |
🔧 7. The Semiconductor Export Control Architecture
The most consequential and most immediately operational AI geopolitical risk for most technology-dependent organizations is the architecture of semiconductor export controls that the United States, with varying participation from allies including Japan, the Netherlands, and South Korea, has constructed around the advanced chip technology required to train and deploy frontier AI systems. Understanding this architecture — not just the specific rules but the logic and trajectory of the control regime — is essential for making sound AI infrastructure decisions in 2026 and planning for how the landscape will evolve.
The October 2022, October 2023, and October 2024 Rule Sets
The current export control architecture for AI-related semiconductors was built in three major rule-making actions, each more comprehensive than the previous one. The October 2022 rules imposed restrictions on exports of advanced logic chips and semiconductor manufacturing equipment to China, targeting chips above specific performance thresholds measured in total performance and interconnect speed — and including a foreign direct product rule that extended US jurisdiction to chips made by non-US manufacturers using US-origin equipment or intellectual property. The October 2023 rules expanded the control architecture substantially — adding chips from additional manufacturers, closing the loopholes through which controlled chips had continued to flow via third countries, and creating a three-tier country classification system. The October 2024 rules added comprehensive controls on the export of advanced AI software, including in some cases large language model weights, to controlled destinations.
The Practical Effect on Global AI Development
The practical impact of these controls on China’s AI development has been significant but not as decisive as some US policymakers initially hoped. Chinese chip designers — led by Huawei’s HiSilicon and emerging companies including Cambricon and Biren Technology — have made faster progress in designing domestically producible AI chips than the US control architecture anticipated. Chinese manufacturers have also continued to access some level of controlled chips through third-country distributor networks that enforcement actions have not fully disrupted. And Chinese AI researchers have demonstrated that for many applications, models trained on somewhat less capable chips can approach the performance of frontier models trained on the most advanced available hardware — raising questions about whether the chip control strategy can achieve its stated goal of preventing China from developing competitive frontier AI capabilities.
For non-Chinese and non-Russian organizations, the export controls create compliance obligations and supply chain management requirements rather than direct denial of chip access. BIS enforcement actions taken against organizations that violated the chip export controls in 2024 and 2025 — including significant financial penalties and in some cases criminal referrals — demonstrate that the enforcement posture is serious and that compliance negligence carries genuine organizational risk. According to BIS’s export enforcement program, civil penalties for export control violations can reach twice the value of the transaction or $1 million per violation — whichever is greater — and criminal penalties can include substantial fines and imprisonment for responsible individuals.
Allied Coordination and the Multilateral Control Architecture
The effectiveness of the US semiconductor export control strategy depends critically on allied coordination — because chips and manufacturing equipment produced by Japanese, Dutch, South Korean, and Taiwanese manufacturers are equally capable of training frontier AI models and would simply substitute for US-produced items in Chinese supply chains if not subject to equivalent restrictions. The Wassenaar Arrangement provides the legal framework within which allied coordination on chip controls operates, but achieving and maintaining allied alignment on the specific scope and timing of restrictions has required intensive diplomatic engagement that has not always produced complete agreement on pace or scope.
The Netherlands’ restrictions on ASML — the sole global supplier of extreme ultraviolet lithography machines essential for manufacturing the most advanced semiconductor nodes — represent the most strategically significant allied contribution to the chip control architecture. ASML’s EUV equipment cannot be exported to China without Dutch government license, and Dutch authorities have declined to issue these licenses under strong US encouragement. This single restriction, covering equipment that no other company in the world can supply, is arguably as significant as all the chip-specific export controls combined in limiting China’s ability to domestically manufacture the most advanced AI chips.
🤖 8. AI Software, Models, and the Emerging Digital Frontier
While semiconductor export controls have dominated coverage of AI geopolitics, a rapidly developing second front in the AI technology competition concerns AI software, model weights, and the knowledge embedded in trained AI systems. The question of whether large language model weights — the mathematical parameters that encode everything a trained AI model has learned — constitute exportable technology subject to export control has been actively debated within the US government and is increasingly being resolved in favor of control for the most capable models.
Model Weight Export Controls: The Emerging Framework
The October 2024 export control rules for the first time explicitly included provisions addressing the export of certain AI model weights, establishing a framework for controlling the transfer of trained AI models to controlled jurisdictions. The specific thresholds and scope of these controls — which models are covered, what “export” means for a model that can be downloaded, how to think about models accessible through API versus models distributed as downloadable weights — are areas of ongoing regulatory development creating significant compliance uncertainty for AI developers. The policy challenge of controlling AI model exports is significantly more complex than controlling physical chips: a chip cannot be downloaded through the internet; a set of model weights can. These enforcement challenges have led some export control experts to be skeptical that model controls can be effectively enforced, while others argue that even imperfectly enforceable controls create meaningful friction that serves policy objectives.
Open-Source AI and the Control Challenge
The open-source AI ecosystem — models like Meta’s Llama 4, Mistral’s models, and the hundreds of community-developed models available through Hugging Face and similar repositories — creates a specific challenge for AI export control that reflects the fundamental tension between the US’s open technology culture and its strategic interest in limiting adversary access to AI capability. Models that have been publicly released under open licenses cannot be effectively recalled or restricted once released — they are globally available to anyone with the computational resources to download and run them, including entities in controlled jurisdictions. The policy debate around whether and how to restrict open-source AI model releases is one of the most contested in current US AI governance. Arguments for restriction note that capable open-source models can be fine-tuned for specific applications — including weapons development — that create genuine national security concerns. Arguments against restriction note that open-source AI has produced enormous beneficial innovation and that restricting US releases would cede open-source leadership to non-US actors. The framework for open-source versus closed-source AI deployment provides useful context for understanding why this question has both technical and geopolitical dimensions that resist simple answers.
☁️ 9. Cloud AI Services and the Sanctions Compliance Challenge
For most organizations that access AI capabilities through cloud service providers rather than training models on owned infrastructure, the primary geopolitical compliance concern is not semiconductor export controls but rather the cloud service provider’s sanctions compliance obligations — and the implications of those obligations for service availability, data handling, and operational continuity. Cloud AI services are subject to comprehensive sanctions regimes that restrict providers from serving customers in sanctioned jurisdictions or from serving entities on designated party lists regardless of where those entities are legally incorporated.
OFAC Compliance and the AI Service Provider Obligation
The US Treasury Department’s Office of Foreign Assets Control (OFAC) administers comprehensive sanctions programs that restrict US persons and US-nexus service providers from engaging in transactions with sanctioned countries — including Iran, North Korea, Cuba, Syria, and Russia under various program categories — and with specifically designated individuals and entities on the SDN list. For AI service providers, OFAC compliance means maintaining the technical and procedural infrastructure to screen customers, verify their sanctions status, and terminate service when sanctions exposure is identified. OFAC expects service providers to implement reasonable due diligence appropriate to the risk profile of the service — which for high-capability AI services with national security applications means more thorough customer verification than for general-purpose web services.
Reciprocal Blocking: China’s Great Firewall and AI Services
The United States is not the only source of AI access restrictions in the current geopolitical environment. China’s internet censorship infrastructure — the “Great Firewall” — blocks access to most major Western AI services including ChatGPT, Claude, Gemini, and the majority of AI tools built on these models. For multinational organizations operating in China, the blocking of Western AI services creates operational implications that require explicit planning. Research teams, engineering departments, and business units in China cannot access the same AI productivity tools as their colleagues in the US, Europe, or other markets — creating a two-tier capability environment within the same organization. Organizations address this through China-compliant AI services (domestic platforms including Baidu’s ERNIE, Alibaba’s Qianwen, and Zhipu AI’s ChatGLM have developed rapidly and can substitute for Western services in many use cases) and local deployments of open-source AI models that do not require internet access to Western services.
The India, Middle East, and Southeast Asia Complexity
The binary US-China framing of AI geopolitics obscures the complexity facing organizations operating in the significant portion of the world that sits outside both major technology blocs. India’s AI ecosystem is receiving enormous US government and corporate investment while maintaining long-standing defense and technology relationships with Russia — creating a complex compliance environment for organizations serving Indian customers or operating Indian facilities. The UAE’s position as a significant AI hub attracting both US and Chinese technology investment has evolved materially in 2026: a BIS final rule effective July 10, 2026 upgraded the UAE’s export control status, removing it from Country Groups D:3 and D:4 and adding it to Country Group A:5 — creating an entity-specific approval framework that gives vetted UAE entities access to advanced AI computing items. These “middle power” jurisdictions represent the most genuinely complex compliance environment for multinational organizations, and engagement with qualified export control counsel should be treated as a baseline operational requirement rather than an exceptional response to specific incidents.
📰 Want to stay current on AI? Browse the AI Buzz News & Trends Hub — curated analysis of the latest AI market shifts, geopolitics, workforce impact, and industry trends shaping 2026.
🇮🇳 9A. US Export Controls on AI Chips: Impact on India’s AI Infrastructure (2026)
India occupies a strategically privileged position in the US AI chip export control architecture — classified as a “trusted partner” under US export regulations, giving Indian organizations legal access to NVIDIA H100, H200, and AMD Instinct series chips that China cannot freely procure. However, that preferential access comes with cost pressures, delivery constraints, and bilateral negotiation complexity that are materially reshaping how Indian hyperscalers, data centers, and AI startups plan and fund their infrastructure buildouts in 2026.
| Dimension | Detail (2026) |
|---|---|
| Controlling regulation | US Export Administration Regulations (EAR) — BIS controls under ECCNs 3A090 and 4A090, covering advanced AI accelerators. India classified as trusted partner; not in restricted Country Groups D:1, D:3, or D:4. |
| Key restricted chips (China-banned) | NVIDIA H100 and A100 (both variants) — banned to China since October 2022; NVIDIA A800 and H800 — banned since October 2023; NVIDIA Blackwell B200 and GB200 — presumption of denial. India can legally access all of these subject to standard EAR due diligence obligations. |
| India-specific access position | Indian companies can access NVIDIA H200 and AMD Instinct AI chips without the volume caps, tariff conditions, or KYC certification layers that govern China-bound exports. However, the rescission of the AI Diffusion Rule shifted India from a fixed access tier to bilateral arrangement dependency — creating planning uncertainty for large-scale GPU cluster procurement. |
| Cost and delivery constraints (2026) | India’s combined import duty on AI GPUs runs approximately 28–30% (7.5% basic customs duty plus 18% IGST), pushing NVIDIA H200 SXM5 cards to approximately ₹35–38 lakh each all-in. The global 25% tariff on controlled AI chips has stretched H200 delivery times to 6–9 months for Indian data centers competing against hyperscaler demand. |
| Government response: ISM 2.0 | India Semiconductor Mission 2.0, announced in the Union Budget 2026, includes a compute access framework allowing MeitY and the IndiaAI Mission to negotiate bulk GPU procurement deals with NVIDIA and AMD on behalf of Indian institutions — potentially reducing per-unit compute costs through government-level volume agreements. The IndiaAI compute program at indiaai.gov.in offers subsidised GPU access for eligible Indian startups and research institutions. |
| Domestic chip development pathway | India’s Shakti RISC-V processor program — developed at IIT Madras under government funding — represents the primary domestic semiconductor design track. Shakti chips do not yet approach the AI training performance of NVIDIA’s H-series, but the program’s ongoing development signals long-term intent to reduce import dependency. A growing ecosystem of Indian chip design startups is receiving ISM 2.0 funding to develop application-specific AI accelerators. |
| 2026 bilateral trajectory | With the AI Diffusion Rule rescinded, India’s future GPU access terms depend on bilateral US-India semiconductor diplomacy — an opportunity for deeper preferential access but also a source of planning uncertainty that organizations with India-based AI operations must factor into multi-year infrastructure roadmaps. |
What the BIS AI Chip Export Controls Actually Restrict
BIS controls advanced AI chips through Export Control Classification Numbers (ECCNs) 3A090 and 4A090 — the regulatory categories that cover the NVIDIA H100, H200, A100, B100, B200, GB200, and AMD MI300X series, among others. These classifications impose license requirements or license exception conditions that bind every party in the supply chain, not only the original exporter. The compliance burden does not end when controlled hardware clears customs at the destination port — it continues for the operational life of the equipment. Data center operators hosting controlled GPUs, cloud service providers offering compute on controlled infrastructure, and sovereign AI platform operators running controlled clusters all carry ongoing compliance obligations under US export controls, regardless of whether they are US companies.
For India specifically, the trusted partner classification means that the most restrictive licensing layers — the 25% tariff, the 50% volume cap, and the mandatory US-based third-party testing that apply to China-bound H200 exports under the January 2026 BIS rule — do not apply to standard Indian procurement. Standard EAR due diligence obligations still apply: Indian purchasers must verify end-use compliance, maintain documentation of chip deployment, and ensure that controlled chips are not re-exported to restricted destinations. The critical compliance risk for Indian organizations is not acquisition — it is post-acquisition re-export or unauthorized transfer that could inadvertently funnel controlled technology toward restricted jurisdictions.
India’s AI Infrastructure Under Export Control Pressure
India’s AI infrastructure buildout is proceeding at scale — the government’s target of establishing significant sovereign GPU capacity under IndiaAI and ISM 2.0 is real and funded — but it is constrained by the global supply chain dynamics that US export controls have created. NVIDIA’s H200 production capacity remains heavily allocated to US hyperscalers and the China case-by-case review pipeline, creating delivery backlogs for Indian buyers that stretch to six to nine months even for priority procurements. The combined import duty burden of approximately 28–30% adds meaningful cost to Indian data center economics, reducing the compute-per-dollar available to Indian AI developers relative to their US counterparts working with domestically-sourced hardware at pre-tariff prices.
The proposed global GPU licensing framework floated by the Trump administration in March 2026 — a three-tier volume system that would require US government approval for large GPU cluster deployments anywhere in the world, including allied nations — represents the most significant potential constraint on Indian AI infrastructure development in the near term. Under the proposed framework, GPU orders above 200,000 units would require formal certification from government officials in the host country. While final rules had not been published as of October 2026, the proposal signals a trajectory toward global compute governance that would formalize India’s bilateral relationship with the US as a prerequisite for large-scale sovereign AI cluster deployment.
How Indian AI Companies Are Responding in 2026
Indian AI organizations are navigating export control pressure through four primary strategies. First, institutional procurement aggregation: routing GPU purchases through the IndiaAI Mission’s bulk procurement framework to access government-negotiated pricing and reduce per-unit cost. Second, alternative supplier diversification: evaluating AMD Instinct MI300X series as a partial substitute for NVIDIA H-series chips in training workloads where CUDA lock-in is not a constraint. Third, open-source model optimization: investing in inference optimization techniques — quantization, speculative decoding, and efficient batching — that reduce the compute required to serve frontier-capability models, partially offsetting per-GPU cost disadvantages. Fourth, domestic design investment: channeling ISM 2.0 funding into application-specific AI accelerator design that targets inference workloads where general-purpose GPU performance advantages are smaller, building toward a longer-term reduction in import dependency. For organizations building AI infrastructure with India-based operations, the practical planning implication is to model six to nine month hardware delivery timelines into procurement schedules and to treat the IndiaAI bulk procurement pathway as the cost-efficient route for large cluster builds.
📋 9B. AI Export Regulations 2026: What Changed and Who Is Affected
The 2026 AI export regulatory environment has seen more rule changes, guidance updates, and enforcement escalations in a twelve-month period than in any comparable period since the initial October 2022 framework was established. Organizations that mapped their compliance posture in 2024 or even early 2025 are operating on outdated assessments. The table below provides a chronological change log of the material regulatory developments that compliance teams need to have absorbed before the November 2026 Affiliates Rule resumption deadline. For the broader AI governance frameworks that contextualize these export controls within organizational risk programs, see our AI Governance Explained guide.
| Date | Regulation / Action | Issuing Body | Key Change | Who Is Affected |
|---|---|---|---|---|
| January 15, 2026 | BIS Final Rule — Advanced AI Chip Export Review Policy (91 FR 1684) | US Dept of Commerce / BIS | Replaced “presumption of denial” with case-by-case review for chips below TPP 21,000 and DRAM bandwidth 6,500 GB/s (NVIDIA H200, AMD MI325X) destined for China — subject to 25% tariff, 50% volume cap, mandatory US-based testing, and KYC documentation. Re-exports to China remain presumed denied. | 🔴 Chip exporters, cloud providers, data center operators, AI hardware supply chains globally |
| February 2026 | BIS Enforcement — $252M Settlement | US Dept of Commerce / BIS | Second-largest standalone BIS penalty in history — materials engineering company. BIS simultaneously signalled intent to seek Congressional authority to raise the per-violation ceiling to $1.2 million and double the statute of limitations from five to ten years. | 🔴 Any organisation with AI hardware or semiconductor supply chain exposure |
| March 5, 2026 | Proposed Global GPU Licensing Framework (Bloomberg) | US Dept of Commerce / BIS (draft) | Draft rules would extend GPU export licensing to every country globally — including allies. Three-tier volume framework: under 1,000 GPUs standard review; mid-volume preclearance; 200,000+ GPUs requires host-country government certification. Final rule not yet published as of October 2026. | 🟠 All global AI infrastructure projects above 1,000 GPU scale — including EU, UK, India, Japan |
| March 26, 2026 | Chip Security Act — House Foreign Affairs Committee (42-0 vote) | US Congress | Legislation advanced requiring BIS to establish hardware-level chip location verification mechanisms for all exported controlled chips under ECCNs 3A090 and 3A001.z — creating real-time tracking obligations for the operational life of controlled hardware deployed internationally. | 🟠 Data center operators, cloud providers, and sovereign AI programs holding controlled GPUs outside the US |
| May 31, 2026 | BIS Guidance — D:5 Licensing Requirements Reaffirmed; AI Diffusion Rule Rescission | US Dept of Commerce / BIS | Confirmed November 2023 licensing requirements remain in full force for Country Group D:5 (China, Russia, Iran). Closed loophole allowing Chinese-headquartered entities to acquire chips through overseas subsidiaries. Simultaneously rescinded the AI Diffusion Rule’s fixed three-tier country framework — shifting access terms for Tier 2 nations (India, UAE, Singapore, Israel, Saudi Arabia) to bilateral negotiation. | 🔴 Chinese-headquartered entities globally; 🟠 All organisations in Tier 2 former Diffusion Rule countries planning large AI infrastructure builds |
| July 10, 2026 | BIS Final Rule — UAE Export Control Status Upgrade | US Dept of Commerce / BIS | UAE removed from Country Groups D:3 and D:4; added to Country Group A:5. New entity-specific approval framework created for advanced computing items — vetted UAE entities can now access controlled AI chips under a structured approval pathway. First major post-Diffusion Rule bilateral upgrade. | 🟠 Organisations with UAE data center operations or AI infrastructure partnerships; sets template for future bilateral arrangements |
| August 2, 2026 | EU AI Act Articles 8–15 — High-Risk AI Provisions Enforceable; Article 50 Synthetic Media Disclosure Active | European Commission | High-risk AI system obligations (conformity assessments, human oversight, transparency) now enforceable for EU deployments. Article 50 mandates machine-readable disclosure on all AI-generated synthetic media — applies to any operator deploying to EU users regardless of headquarters jurisdiction. | 🔴 Any organisation deploying AI to EU markets — marketing, media, healthcare, finance, HR applications |
| November 10, 2026 | BIS Affiliates Rule Suspension Expires | US Dept of Commerce / BIS | One-year suspension of the Affiliates Rule — which extends export control restrictions to foreign entities at least 50% owned by BIS Entity List, Military End-User List, or OFAC SDN entities — expires. Rule is expected to resume in some form. Beneficial ownership audits must be completed before this deadline. | 🔴 Data center operators, AI hardware purchasers, and cloud providers with complex international ownership structures |
US Bureau of Industry and Security (BIS): 2026 AI Controls
The defining characteristic of BIS’s 2026 AI control posture is simultaneous policy liberalization and enforcement escalation — a combination that creates significant planning complexity for compliance teams. The January 2026 case-by-case rule for H200/MI325X exports to China represents a policy shift away from blanket denial, but the enforcement environment has intensified sharply in parallel. The February 2026 $252 million settlement — the second-largest standalone BIS penalty on record — was accompanied by public statements from BIS’s Assistant Secretary for Export Enforcement indicating that current penalty ceilings are insufficient deterrents. BIS is simultaneously pursuing Congressional authority to raise the per-violation ceiling from $1 million to $1.2 million and to double the statute of limitations for export control violations from five to ten years. The practical compliance implication: the window of opportunity to remediate historical compliance gaps is narrowing materially, and organizations that discover past violations now face a lengthening liability horizon if those violations occurred within a potential future ten-year lookback period.
EU AI Act: Export and Cross-Border Implications
The EU AI Act’s cross-border reach extends well beyond its conventional characterization as a domestic EU regulation. Article 50’s August 2026 activation — requiring machine-readable synthetic media disclosure for any AI system deployed to EU users — operates on the same extraterritorial logic as GDPR: it applies to any operator deploying to EU users, regardless of where that operator is headquartered. The draft EU AI export control framework circulating among member states in 2026 — which proposes controls on AI accelerators exceeding approximately 300 TFLOPS — would, if adopted, create a parallel European export control regime operating alongside the US EAR architecture. EU-based organizations currently relying on the absence of EU chip export controls as a compliance simplification would face material new obligations. The EU AI Act’s broader framework for AI governance frameworks provides the organizational accountability structure within which these export-adjacent obligations sit.
What “Deemed Export” Means for AI Model Weights and Training Data
The deemed export doctrine — which treats the transfer of controlled technology to a foreign national inside the United States as an export to that person’s country of citizenship — is expanding its footprint in AI regulation in ways that most technology organizations have not fully absorbed. The October 2024 BIS rules, which for the first time included provisions addressing the export of certain AI model weights, raise a direct deemed export question: if a researcher who is a national of a restricted country has access to controlled model weights, training methodologies, or model architecture documentation within a US organization, that access may constitute a deemed export requiring the same license that a physical export would require. The compliance implication is not limited to obviously sensitive military-application AI — it extends to any AI research environment where controlled technology categories are present and where researchers who are nationals of Country Group D:5 destinations have access. HR and engineering teams that have not integrated deemed export assessment into their hiring workflows for AI research roles have a compliance gap that BIS’s expanding enforcement posture makes urgent to address.
🌐 9C. Geopolitical AI Risk Map: Which Countries Face the Highest Infrastructure Constraints
The geopolitical risk profile for AI infrastructure varies dramatically by jurisdiction — and the US-China binary that dominates most analysis obscures the operational complexity facing organizations with footprints in India, the Middle East, Southeast Asia, and other markets that sit in the contested middle of the US-China technology competition. The table below provides a structured comparison of export control exposure, domestic AI capacity, and overall infrastructure risk by region — the format that policy audiences and enterprise risk officers use to triage planning decisions.
| Region / Country | Export Control Exposure | Domestic AI Capacity | Key 2026 Development | Infrastructure Risk Level |
|---|---|---|---|---|
| 🇮🇳 India | Medium — Trusted Partner status grants legal access to controlled chips; no chip bans; 28–30% combined import duties; 6–9 month delivery delays; bilateral dependency post-Diffusion Rule rescission | Growing — ISM 2.0 compute access framework; IndiaAI Mission bulk procurement; Shakti RISC-V domestic chip program; strong software and AI services ecosystem | India Semiconductor Mission 2.0 (Union Budget 2026) — government-negotiated GPU bulk procurement; IndiaAI subsidised compute for startups and researchers | 🟠 Medium-High — access available but cost-constrained; planning dependent on bilateral US-India semiconductor diplomacy |
| 🇨🇳 China | Highest — H100, A100, H800, A800 banned; Blackwell series presumed denied; H200 case-by-case with severe conditions; January 14, 2026 China boycotted approved H200 anyway; re-exports from third countries presumed denied | Significant — Huawei Ascend 910B/C accelerators in commercial training deployments; SMIC 7nm process node advancing; Cambricon and Biren developing alternative architectures; models from Baidu, Alibaba, Zhipu narrowing capability gap | China’s MIIT ordered domestic AI companies to boycott newly-approved H200 and prioritise homegrown silicon (January 14, 2026) — accelerating domestic ecosystem despite controls | 🔴 High — severe frontier chip access constraint; domestic substitution underway but performance gap remains significant for largest training runs |
| 🇦🇪 UAE / Middle East | Medium, improving — UAE upgraded to Country Group A:5 (July 10, 2026): removed from D:3 and D:4; vetted entity-specific approval framework for advanced AI chips; Saudi Arabia and other GCC states still subject to case-by-case review | Emerging — Significant sovereign AI investment (UAE G42, Saudi Humain); both US and Chinese AI investment attracted; limited domestic chip design; primary capacity through hyperscaler partnerships | UAE A:5 upgrade creates entity-specific chip access framework — first post-Diffusion Rule bilateral model; sets template that India and other trusted partners may seek to replicate | 🟡 Medium — UAE access improving significantly; Saudi Arabia and broader GCC still navigating case-by-case complexity with dual US/China investment tension |
| 🇪🇺 European Union | Low-Medium — EU member states are allies; standard export clearances apply; proposed EU-specific accelerator controls (above ~300 TFLOPS) circulating 2026 but not yet adopted; EU AI Act compliance adds domestic regulatory overhead | Moderate — Mistral AI (France) represents frontier open-source model development; EU sovereign AI fund investments ongoing; semiconductor fabrication dominated by non-EU supply chains; ASML provides strategic EUV lithography leverage | EU AI Act Articles 8–15 enforceable August 2, 2026; draft AI-specific export controls circulating among member states; proposed GPU threshold controls could create new compliance layer for EU-based operators | 🟢 Low-Medium — chip access available; primary risk is regulatory compliance overhead and potential EU-specific accelerator controls under consideration |
| 🇯🇵🇰🇷 Japan / South Korea | Low — both are Wassenaar Arrangement members and key allied semiconductor nations; standard ally-tier export clearances; proposed global GPU licensing framework would introduce new documentation requirements even for allies at 200,000+ GPU scale | High — TSMC advanced node fabrication (Taiwan-origin); Samsung and SK Hynix HBM memory supply; Japan METI semiconductor investment programs; NEC, Fujitsu domestic AI development | Samsung and SK Hynix received annual BIS licences replacing expired VEU status; Japan and Netherlands continue coordinated restrictions on advanced semiconductor manufacturing equipment exports to China | 🟢 Low — highly capable domestic semiconductor ecosystems; ally-tier export treatment; primary exposure is supply chain dependency on Taiwanese fabrication |
| 🇸🇬🇮🇩 Southeast Asia | Medium — Singapore was in former Diffusion Rule Tier 2 alongside India; now subject to bilateral negotiation post-rescission; Indonesia and Vietnam in standard review tier; re-export risk elevated given proximity to restricted jurisdictions | Emerging — Singapore hyperscaler data center hub; Indonesia and Vietnam growing AI startup ecosystems; limited domestic chip design capacity; high dependency on NVIDIA cloud and hyperscaler partner programs | Post-Diffusion Rule rescission creates bilateral uncertainty for Singapore’s data center operators; re-export enforcement focus elevated as BIS targets China-headquartered entities acquiring chips through overseas subsidiaries in the region | 🟠 Medium — chip access generally available but re-export compliance risk elevated; bilateral terms under negotiation; Singapore most exposed to post-rescission uncertainty |
The strategic implication of this risk map is that the most complex compliance environments in 2026 are not the obviously restricted jurisdictions — China and Russia — but the “bilateral dependency” jurisdictions: India, Singapore, Saudi Arabia, and other markets whose access terms shifted from fixed regulatory tier to case-by-case diplomatic negotiation when BIS rescinded the AI Diffusion Rule. Organizations with significant AI infrastructure investments in these markets should treat bilateral semiconductor diplomacy as a live business risk variable, not a background geopolitical development, and should model access uncertainty into multi-year infrastructure planning timelines. The agentic AI infrastructure layer adds an additional compliance dimension for these jurisdictions — as autonomous AI systems deployed across borders interact with cloud endpoints, model APIs, and tool-calling frameworks, the question of where controlled technology is “used” becomes as complex as the question of where it is “exported.” For organizations deploying agentic AI across multi-jurisdiction infrastructure, the technical identity and access controls discussed in our guide to AI agent identity standards have direct export compliance implications: uncontrolled agent-to-service calls that cross jurisdictional boundaries can constitute the kind of unauthorized technology access that export controls are designed to prevent.
🔗 10. AI Supply Chain Risk Assessment: Mapping Your Exposure
Effective management of AI geopolitical risk requires understanding your organization’s specific supply chain dependencies at a granularity that most technology teams have not previously needed to develop. The question is not whether your organization uses AI — in 2026, virtually every significant organization does — but which specific AI components, from which specific vendors, manufactured with which specific inputs, create geopolitical exposure that could affect operational continuity, compliance standing, or competitive position. The May 2026 BIS guidance emphasizes that due diligence must encompass both the direct vendor and the underlying infrastructure that enables the service.
The Four-Layer AI Supply Chain
Understanding AI supply chain risk requires mapping across four distinct layers that together constitute the complete supply chain for any AI capability your organization depends on. Each layer has different geopolitical risk characteristics that need to be assessed separately rather than assumed to be equivalent. As workloads move toward autonomous systems, the “Models & Software” layer must also incorporate emerging AI agent identity standards to ensure non-human identities used by agents are compliant with cross-border data transfer and service export regulations.
| Supply Chain Layer | Key Geopolitical Risk | Critical Component |
|---|---|---|
| 1. Hardware & Silicon | Semiconductor export controls; rare earth mineral bans; fabrication jurisdiction (Taiwan risk) | GPUs, AI Accelerators, Lithography equipment |
| 2. Cloud Infrastructure | Sanctions-driven service blocking; data localization laws; infrastructure nationalization risk | Data centers, IaaS providers, High-bandwidth networking |
| 3. Models & Software | Model weight export bans; API access termination; training data sovereignty violations | Foundational models (LLMs), Inference APIs, Model weights |
| 4. Data & Knowledge | Cross-border data flow bans; deemed export of model training IP; geopolitical dataset poisoning | Training sets, RAG databases, User prompts |
A practical AI geopolitical risk audit follows this four-layer framework to document the organization’s current supply chain dependencies. The output of the audit is not a binary assessment but a risk map identifying where dependencies are concentrated and which mitigation investments provide the most reduction in exposure. The investment required to map these layers is a prerequisite for the resilience framework described in the following sections. Our guide to AI Risk Assessment provides the evaluation methodology framework that informs this process.
🛡️ 11. The Resilience Framework: Building AI Supply Chain Security
The appropriate response to AI geopolitical risk is not paralysis or withdrawal from AI investment — AI capability is too central to competitive position in 2026 for any serious organization to make that choice. The appropriate response is deliberate resilience planning that reduces concentrated dependencies, builds operational flexibility, and maintains compliance discipline — creating an AI architecture that can sustain operations across a broader range of geopolitical scenarios than a single-vendor, single-jurisdiction approach would permit.
Diversification Across Providers and Geographies
The single most effective structural resilience strategy is avoiding single-vendor dependencies for critical AI capabilities — maintaining the ability to operate with alternative providers if a specific vendor becomes unavailable due to sanctions or export controls. For cloud AI services, this means maintaining tested integrations with multiple providers — not just primary and backup configurations on paper, but regularly exercised alternative pathways. For frontier AI model access, it means maintaining the technical capability to switch between models from different providers, including open-source models that can be self-hosted if cloud API access becomes unavailable.
On-Premises and Sovereign AI Deployment Capability
For organizations with the highest sensitivity to AI supply chain risk — critical infrastructure operators, defense contractors, and those handling sovereign data — developing the capability to run AI workloads on owned or leased on-premises infrastructure provides the deepest resilience. On-premises AI deployment using open-source models eliminates dependency on cloud service providers’ sanctions compliance policies and avoids data sovereignty risks associated with cross-border cloud data flows. The Sovereign AI and Resilience framework provides the detailed technical guidance for building self-sufficient AI capabilities that can sustain operations through disruption.
Compliance Infrastructure and Legal Expertise
Building the infrastructure to navigate AI geopolitical regulations requires investment in human expertise. Export control compliance for AI-related products requires legal expertise in multiple regulatory regimes — BIS EAR, OFAC sanctions, and EU dual-use regulations. Organizations should assess whether their current legal capacity is adequate for the compliance obligations they face and engage specialized counsel for gap analysis. On the process side, compliance infrastructure includes vendor screening, transaction monitoring for sanctioned jurisdictions, and a technology classification process (ECCN) to determine which components require licenses. These processes must be integrated into procurement and product development workflows.
🌏 12. The Sovereign AI Dimension
The geopolitical vulnerabilities created by AI dependence have triggered a global movement toward sovereign AI — the effort by nation-states and regional blocs to develop indigenous AI capabilities that do not depend on the technology stacks of rival powers. The Strategic Logic of Sovereign AI is rooted in the recognition that AI has become a foundational infrastructure, similar to telecommunications or energy grids. A nation that depends entirely on foreign-controlled AI models, chips, and cloud infrastructure is inherently vulnerable to the technological, economic, and political priorities of the providing power.
In 2026, the strategic logic of sovereign AI has shifted from purely government projects to public-private partnerships. Nations are investing in domestic GPU clusters, localized training data repositories that reflect national linguistic and cultural nuances, and domestic AI talent pipelines to reduce the “brain drain” to Silicon Valley. The goal is to ensure that even in a scenario of total technological decoupling, the nation retains the ability to operate its own critical infrastructure, government services, and domestic economy using AI systems it controls. However, the limits and tensions of sovereign AI are significant: the capital requirements are enormous, and the performance gap between domestic sovereign models and global frontier models remains a significant hurdle for commercial adoption.
🏛️ 13. The Global Governance Gap
The UN Global Dialogue and Its Limits represent the primary international effort to coordinate AI governance, yet the gap between diplomatic ambition and operational reality remains wide. While the UN General Assembly adopted a landmark resolution in 2024 on “seizing the opportunities of safe, secure and trustworthy AI systems,” the resolution lacks the enforcement mechanisms needed to govern the most contentious aspects of AI geopolitics, particularly autonomous weapons and state-sponsored information warfare.
Governance Reality Check: International AI governance is currently a patchwork of voluntary codes and non-binding declarations. In the vacuum created by the absence of a global AI treaty, national and regional regulations like the EU AI Act and US Export Controls have become the de facto standards that global organizations must follow.
🚀 Governance & Security Hub
Build a resilient, compliant AI strategy. Explore our AI Governance & Security Hub for the latest frameworks on risk management, regulatory compliance, and supply chain security in 2026.
🌐 14. The Technology Decoupling Scenarios: Planning for Different Futures
Effective geopolitical risk planning requires thinking explicitly about the range of future scenarios that could materialize. The decisions organizations make now about AI architecture will persist for years and must be robust to futures that look different from today’s baseline.
- Scenario 1: Managed Decoupling (Most Likely): Successive rounds of export control tightening progressively limit adversary access to frontier AI hardware, but economic interdependence prevents full separation. Organizations must maintain separate AI stacks for specific markets.
- Scenario 2: Accelerated Decoupling (Significant Risk): Triggered by a major geopolitical crisis, existing controls are substantially tightened on compressed timelines. Organizations with concentrated dependencies face severe operational disruptions.
- Scenario 3: Regulatory Fragmentation: AI regulatory frameworks diverge dramatically across major jurisdictions (EU, US, China, India), forcing organizations to maintain jurisdiction-specific deployments and compliance postures. Our guide to the EU AI Act provides the framework for the most developed of these requirements.
🔮 15. The Chinese AI Domestic Development Track: What Organizations Need to Know
A dimension of AI geopolitics often underappreciated is the pace of Chinese domestic AI development, which is creating an ecosystem viable for a growing range of commercial applications. Organizations operating in China need to develop a realistic assessment of these capabilities rather than assuming Western services are the only option.
Chinese frontier models from providers like Baidu (ERNIE), Alibaba (Qianwen), and Zhipu AI have narrowed the capability gap, particularly in Chinese-language tasks and mathematical reasoning. On the hardware side, Huawei’s Ascend series AI accelerators are being used in commercial training operations despite performance limitations relative to NVIDIA’s H200. The demonstrated viability of these domestic tracks means Chinese AI development will continue regardless of the success of the chip export control strategy — a reality that affects the medium-term competitive dynamics of the global AI industry.
⚖️ 16. The 2026 Regulatory Stack: Frameworks Every Compliance Team Needs
The landscape of regulatory frameworks governing AI technology exports has grown substantially more complex. Organizations that mapped their compliance based on 2024 data are operating on outdated assessments. For the complete picture of how these frameworks interact with broader AI governance frameworks, see our guide to AI Regulation in 2026 and the Colorado AI Act Explained.
| Framework | Administered By | Covers | Penalty |
|---|---|---|---|
| Export Administration Regulations (EAR) | U.S. BIS (23% budget increase in FY2026) | AI chips, software, technology; ECCN-classified items; deemed exports | Up to $1M per violation or 2× transaction value |
| OFAC Sanctions Programs | U.S. Treasury / OFAC | Transactions with sanctioned entities; AI service provision to SDN-listed persons | Civil + criminal; profit disgorgement; SDN listing |
| EU Dual-Use Regulation (2021/821) | European Commission / member states | Dual-use AI tech; proposed controls on accelerators > 300 TFLOPS | Member state enforcement; varies by jurisdiction |
| Wassenaar Arrangement | 42 member states | Dual-use goods; AI foundational models under active debate for inclusion | Via member state implementing law |
The only defensible compliance posture in 2026 is a comprehensive mapping of all applicable frameworks across all jurisdictions where the organization procures, sells, or transfers AI technology.
📋 17. Compliance Checklist: What Organizations Must Do Now
The following checklist provides the baseline actions every organization with significant AI-related operations should have completed or have in active progress to address current geopolitical risks.
| Priority | Action Required | Who Owns It | Deliverable |
|---|---|---|---|
| P1 — High | Complete AI supply chain audit (Hardware, Cloud, Models, Data) | CTO / Compliance | Geopolitical Exposure Map |
| P1 — High | Implement automated SDN and Entity List screening | Legal / Procurement | Active Screening Registry |
| P2 — Medium | Formal classification of AI products (ECCN determination) | General Counsel | Export License Matrix |
| P3 — Routine | Establish multi-provider failover capability and tests | Engineering / Ops | Failover Test Report |
✅ 18. The AI Geopolitics Compliance Checklist: What to Do in the Next 90 Days
Translating requirements into a structured program converts a reactive posture into an evidence-based one. Most organizations facing BIS or OFAC attention in 2026 are those that had no structured process and discovered exposure only when an incident triggered scrutiny. A 90-day program addresses the four critical areas authorities examine first. For internal governance, the AI Audit Checklist and Corporate AI Policy template provide the necessary documentation.
| Phase | Action | Primary Owner | Strategic Output |
|---|---|---|---|
| Days 1–30 | Inventory all AI tools, hardware, and staff with access to controlled tech | IT + HR | AI Asset Register & Deemed Export Assessment |
| Days 31–60 | Activate geo-restrictions and screen customer base against Entity Lists | Engineering / Legal | Active Control Implementation Report |
| Days 61–90 | Establish formal export policy and quarterly monitoring schedule | General Counsel | Corporate AI Export Compliance Policy |
🏁 19. Conclusion: Geopolitical Risk as Baseline, Not Tail Risk
The most important shift in organizational mindset that AI geopolitics demands is moving from treating geopolitical risk as a tail risk to treating it as baseline operational context that every architecture decision must account for. The organizations that made AI infrastructure decisions in 2022 under the assumption that the technology ecosystem would remain open are now discovering those decisions are proving more costly to revisit than they would have been if geopolitical resilience had been a design criterion from the start.
The practical implications are not about becoming paralyzed by uncertainty or abandoning AI investment — AI capability is too central to organizational performance in 2026 for that choice. The implications are about making decisions that are durable across scenarios — choosing architectures that provide diversification rather than single-vendor concentration, investing in the compliance expertise needed to navigate the regulatory environment, and building the operational flexibility to adapt to new constraints. Every AI capability decision is simultaneously a technology decision, a compliance decision, and a strategic resilience decision. Making all three dimensions explicit is the discipline that separates organizations that will maintain AI capability through the disruptions ahead from those that will find their investments compromised by political events they should have anticipated. The framework in our guide to Buy vs. Build for AI provides additional decision structure for making these multi-dimensional choices systematically.
📌 Key Takeaways
| ✅ | Takeaway |
|---|---|
| ✅ | India NVIDIA Access: India is a US “Trusted Partner” for AI chips, granting legal access to NVIDIA H200 cards that China cannot procure. However, 28–30% import duties and delivery delays of 6–9 months create significant infrastructure cost pressure in 2026. |
| ✅ | 2026 Regulatory Log: Key shifts include the BIS $252M settlement (enforcement escalation), UAE’s A:5 status upgrade (July 2026), and the rescission of the fixed-tier AI Diffusion Rule — shifting “middle power” access to bilateral negotiation. |
| ✅ | Geopolitical Risk Map: Infrastructure risk is highest in China (boycotts/bans) and medium-high in “bilateral dependency” states like Singapore and India, where compute access depends on fluid diplomatic arrangements rather than stable rules. |
| ✅ | The January 15, 2026 BIS final rule replaced the “presumption of denial” for AI chip exports to China with a case-by-case review system, but attached severe conditions including a 25% tariff, 50% volume caps, and mandatory US-based testing. |
| ✅ | The WEF Global Risks Report 2026 ranked AI-enabled mis- and disinformation among the top short-term global risks, warning that industrialized synthetic media operations now threaten rule-of-law and democratic accountability globally. |
| ✅ | The “liar’s dividend” represents a systemic threat where the mere existence of deepfake technology allows individuals to plausibly deny authentic evidence, degrading accountability in corporate governance, legal proceedings, and news media. |
| ✅ | Ukraine has become the world’s first AI-drone battlefield, with autonomous systems accounting for the vast majority of casualties in specific sectors by March 2026, leading to a “governance vacuum” in international laws of armed conflict. |
| ✅ | Congress increased the BIS FY2026 enforcement budget by 23%, specifically targeting semiconductor violations, signaling that enforcement rigor is rising even as specific licensing policies evolve. |
| ✅ | The BIS Affiliates Rule — targeting foreign entities 50% owned by sanctioned companies — is suspended until November 10, 2026, creating a critical planning window for data center operators to complete beneficial ownership audits. |
| ✅ | Downstream consumers of AI services face “deemed export” risks when sharing controlled technology with foreign nationals, requiring HR and engineering teams to integrate export compliance into their hiring and research workflows. |
| ✅ | EU AI Act Article 50, active as of August 2026, mandates detectable and machine-readable disclosure for all AI-generated synthetic media, creating a standard that impacts global marketing and media content distributed in European markets. |
| ✅ | A 90-day program covering inventory, screening, and policy documentation converts reactive compliance exposure into an audit-ready posture, mitigating the risk of penalties that can reach $1 million per violation. |
| ✅ | Sovereign AI development has become a national priority for nation-states seeking to protect critical infrastructure from technological decoupling, driving a move toward localized GPU clusters and domestic model training. |
| ✅ | Every AI infrastructure decision must be evaluated as a technology, compliance, and strategic resilience decision simultaneously, with geopolitical risk treated as baseline operational context rather than a tail risk. |
🔗 Related Articles
- 📖 Sovereign AI and Resilience: Protecting Your Workflows from Geopolitical Risk
- 📖 AI Regulation in 2026: 7 New Laws Reshaping How Businesses Use AI
- 📖 AI in Defense and Military: Autonomous Systems and Strategic Intelligence
- 📖 The AI Audit Checklist: How to Prove Your Company is Compliant in 2026
- 📖 EU AI Act Explained: A Beginner-Friendly Compliance Guide and Practical Checklist
- 📖 Non-Human Identity (NHI) for AI Agents: Security Standards & Risks
❓ Frequently Asked Questions: AI Export Controls and Sanctions Compliance 2026
1. What did the January 2026 BIS rule change about AI chip exports to China?
The January 15, 2026 BIS final rule replaced the previous “presumption of denial” policy for advanced AI chip exports to China with a case-by-case review system. Chips with TPP below 21,000 (including NVIDIA H200 and AMD MI325X) are now eligible for review — but only with a 25% tariff, a 50% volume cap, mandatory US third-party testing, and full KYC documentation. Re-exports remain denied. See our AI Regulation in 2026 guide for the full regulatory context.
2. Does providing AI SaaS or API services internationally create export control exposure?
Yes — software-as-a-service is explicitly covered under US export control regulations. Providing AI-powered services to customers in sanctioned jurisdictions or to SDN-listed entities constitutes an export violation even without any physical product crossing a border. Organizations must implement geo-restriction controls and screen customer lists against OFAC and BIS Entity Lists before onboarding. The AI Vendor Due Diligence Checklist covers the vendor-side of this obligation.
3. What is a “deemed export” and why does it matter for AI companies?
A deemed export is the sharing of controlled AI technology with a foreign national inside the United States — which is legally treated as an export to that person’s country of citizenship. This applies to hiring decisions, research collaborations, and open-source contributions involving nationals of restricted countries working on controlled AI technology. US AI companies with internationally diverse research teams must assess deemed export risk with qualified legal counsel.
4. What is the BIS Affiliates Rule and when does it resume?
The BIS Affiliates Rule extends export control restrictions to foreign entities at least 50% owned (directly or indirectly) by companies on the BIS Entity List, Military End-User List, or OFAC SDN list. It was suspended pending further review and is scheduled to resume November 10, 2026. Organizations with complex ownership structures in their AI supply chains must complete beneficial ownership analysis before this date. Our Sovereign AI and Resilience guide covers the infrastructure resilience strategies that complement compliance programs.
5. What are the penalties for violating AI export control regulations?
Under the Export Administration Regulations, civil penalties for export control violations can reach $1 million per violation or twice the transaction value — whichever is greater. Criminal violations can result in substantial fines and imprisonment for responsible individuals. The BIS received a 23% budget increase in FY2026 specifically for enforcement, including dedicated semiconductor enforcement resources. See The AI Audit Checklist for the evidence documentation framework that demonstrates compliance to regulators.
📧 Get the AI Buzz Weekly Digest
Weekly AI insights, tools, and strategies — delivered every Monday. Free.
Leave a Reply