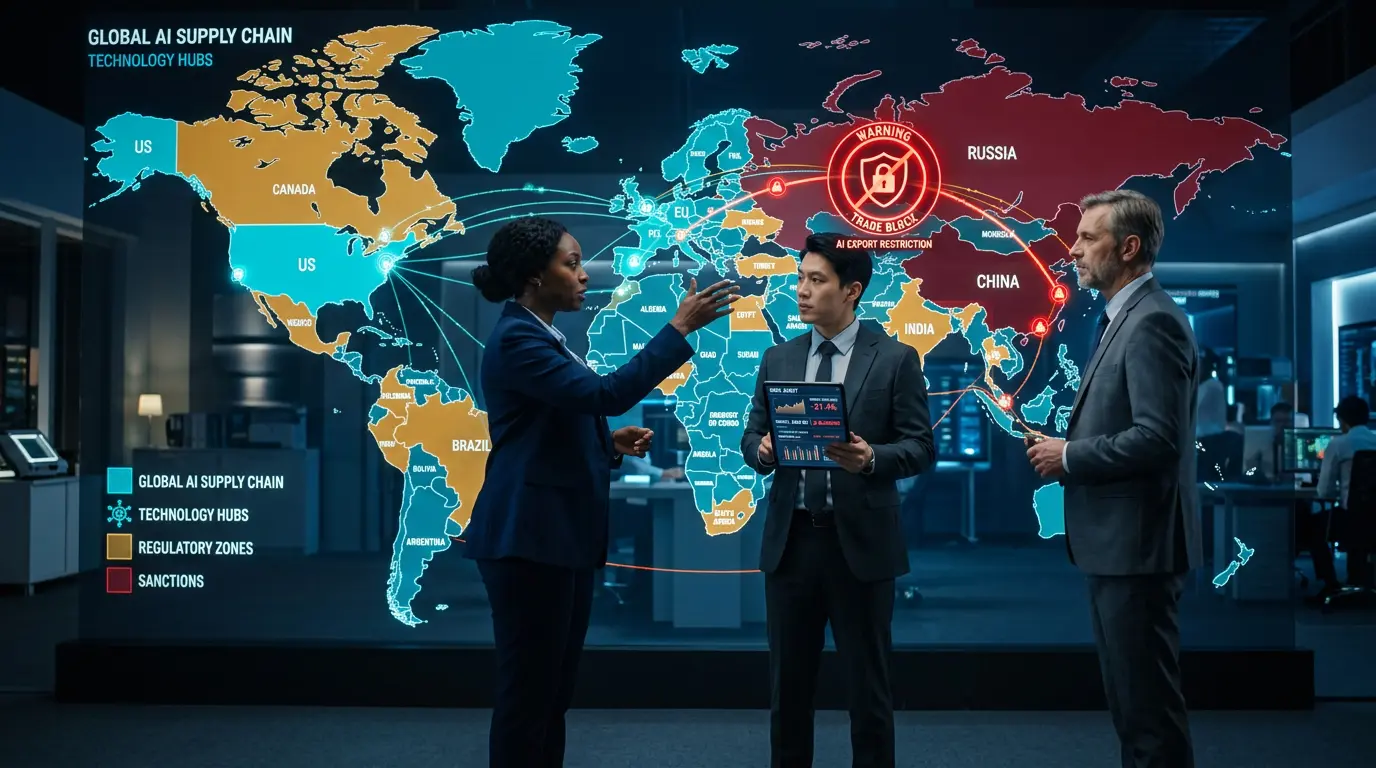
🌍 AI Has Become a Geopolitical Weapon, a Sanctions Target, and the Hardest Supply Chain Risk to Manage in 2026 — All at the Same Time: Export controls on AI chips, software restrictions, model access blocking, and digital sanctions are now reshaping how every organization plans its AI strategy. This comprehensive guide explains exactly how AI geopolitics works, which jurisdictions are at risk, what your supply chain exposure actually is, and the resilience framework that responsible organizations are building right now.
Last Updated: September 14, 2026
The geopolitics of artificial intelligence has moved from a topic discussed at think tanks and policy conferences to a pressing operational reality for technology leaders, supply chain managers, and compliance professionals at organizations of every size. The same AI capabilities that are transforming healthcare, finance, logistics, and manufacturing have simultaneously become instruments of national power, targets of export control regimes, and flashpoints in a broader strategic competition that has fundamentally changed the global technology landscape. Organizations that were building AI infrastructure three years ago with the assumption that AI tools, chips, and services were globally available commodity inputs are now discovering that geopolitical risk has become as important a variable in AI architecture decisions as cost, capability, and latency.
The scale of this transformation is difficult to overstate. The United States has imposed successive rounds of semiconductor export controls targeting China’s AI development capacity — restrictions that now extend to over 40,000 line items of controlled technology and have been designed, in the words of their architects, to prevent China from acquiring the chips needed to train frontier AI models. China has responded with export controls on rare earth minerals and processing technology critical to global electronics supply chains, has accelerated domestic AI chip development programs that are closing the capability gap faster than many Western analysts predicted, and has deployed AI-enabled systems across military, surveillance, and economic applications that have alarmed allies and partners globally. Russia’s invasion of Ukraine demonstrated both the military applications of AI-enabled warfare and the vulnerability of AI infrastructure to sanctions — with Russian access to Western AI tools, cloud services, and semiconductor supply chains disrupted in ways that have materially affected both civilian and military technology capability.
This guide provides a comprehensive, practical examination of AI geopolitics and global sanctions in 2026 — covering exactly how the major export control regimes work and what they restrict, which jurisdictions and use cases create compliance exposure, how AI supply chain dependencies translate into geopolitical risk, and the resilience framework that organizations need to navigate a technology landscape where geopolitical disruption has become a baseline planning assumption rather than a tail risk. Whether you are a CTO evaluating AI infrastructure decisions in light of geopolitical risk, a compliance officer navigating export control requirements for AI-related products, a supply chain leader assessing your organization’s dependencies on geopolitically sensitive technology components, or a board member trying to understand why your organization’s AI strategy now requires geopolitical scenario planning, this guide gives you the analytical framework and practical guidance to engage with this reality systematically. The technical dimensions of AI resilience connect to our guide on Sovereign AI and Resilience — and the governance principles for managing these risks connect to our guide to AI Governance Explained.
📖 New to AI terminology? Visit the AI Buzz AI Glossary — 95+ essential AI terms explained in plain English, each linking to a full in-depth guide.
📊 1. The 2026 Export Control Landscape: What Changed and What It Means
The AI export control environment shifted materially in the first quarter of 2026. The changes did not represent a relaxation of strategic intent — the US government’s goal of limiting China’s access to frontier AI compute remains unchanged — but the specific policy mechanisms evolved in ways that create new compliance obligations and new planning complexity for organizations across the supply chain. Understanding the 2026 state of the export control landscape is essential because compliance requirements from even six months ago may no longer accurately reflect current obligations. The Bureau of Industry and Security (BIS) continues to be the primary US enforcement body, and its enforcement posture is intensifying: Congress approved a 23% increase in BIS’s Fiscal Year 2026 budget, with several million dollars specifically earmarked for semiconductor-related enforcement actions.
The most significant 2026 development is the January 15, 2026 BIS final rule revising the export license review policy for advanced computing semiconductors destined for China and Macau. The previous regime operated under a broad “presumption of denial” — meaning applications to export advanced AI chips to China faced an automatic presumption of rejection. The January 2026 rule replaced this with a case-by-case review system for chips below specific performance thresholds: chips with a Total Processing Performance (TPP) below 21,000 and DRAM bandwidth under 6,500 GB/s — including the NVIDIA H200 and AMD MI325X — are now eligible for case-by-case review instead of automatic denial. This is not a liberalization. The conditions attached to case-by-case approval are substantial: a 25% tariff on affected chips, a 50% volume cap relative to US domestic shipments, mandatory third-party testing conducted in the United States before shipment, and full know-your-customer (KYC) compliance documentation. Re-export licenses — covering chips shipped from the US to a third country and then onward to China — remain under a presumption of denial, closing the third-country circumvention routes that had partially undermined earlier control rounds.
2026 Compliance Reality: In 2026, AI export compliance is not a trade lawyer’s problem. It is a procurement problem, a vendor management problem, and a board-level risk problem. The January 2026 BIS rule created new compliance obligations for every organization in the AI chip supply chain — not just chip manufacturers and exporters.
A second significant 2026 development is the BIS Affiliates Rule — a regulation extending export control restrictions to foreign entities at least 50% owned (directly or indirectly) by entities on BIS’s Entity List, Military End-User List, or OFAC’s SDN list. This rule would dramatically expand the compliance burden for data center operators, cloud providers, and AI hardware purchasers by extending controls to thousands of additional entities connected to listed companies. The Affiliates Rule is currently suspended until November 10, 2026 while BIS evaluates implementation. Organizations should treat this as a compliance planning deadline: the rule is likely to resume in some form, and data center operators and AI hardware purchasers with complex ownership structures need to complete their beneficial ownership analysis before November 2026. In Europe, draft AI export control options began circulating among EU member states in early 2026, with leaked thresholds suggesting controls on AI accelerators exceeding roughly 300 TFLOPS — a development that would affect European organizations currently operating outside the US control architecture.
| Jurisdiction | Key Control (2026) | What It Restricts | Business Impact |
|---|---|---|---|
| United States (BIS/EAR) | AI chip export controls — Jan 2026 case-by-case rule | Advanced GPU/AI chip exports to China, Macau, and restricted destinations; re-exports remain presumed denied | 🔴 Procurement + supply chain compliance; KYC documentation; mandatory US testing |
| United States (OFAC) | SDN list + comprehensive sanctions programs | AI services, cloud access, and financial transactions with sanctioned entities and jurisdictions | 🔴 Software + API service risk; customer screening obligation |
| European Union | Regulation (EU) 2021/821 — updated Sept 2025; draft AI-specific controls circulating 2026 | Dual-use AI technology; cyber-surveillance tools; proposed controls on accelerators above 300 TFLOPS | 🟠 EU-based operations; member state enforcement with criminal exposure |
| United Kingdom | Export Control Order — post-Brexit independent list broadly aligned with EU | AI components classified as dual-use technology; diverging from EU in some AI-specific categories | 🟠 UK-based operations; criminal prosecution for violations |
| China | Data export restrictions + rare earth export controls (2026 escalation) | Cross-border AI data flows; rare earth minerals and processing technology critical to chip manufacturing | 🔴 Any business with China operations or rare earth supply chain exposure |
The Entity List dimension of this landscape deserves specific attention for organizations in the AI supply chain. The US Entity List now contains over 600 Chinese technology companies and affiliates — creating significant compliance complexity for any business sourcing AI components, contracting AI services, or building products that incorporate AI hardware or software with Chinese-origin components. Export control violations carry penalties of up to $1 million per violation or twice the transaction value — whichever is greater — under the Export Administration Regulations. The BIS “know your customer” obligation means organizations cannot plead ignorance if an AI component reaches a sanctioned end-user through an intermediary they failed to screen. Critically, Chatham House research published in April 2026 concludes that export controls alone will not prevent adversaries from developing advanced AI due to enforcement gaps, smuggling, and rapid technical adaptation — suggesting that compliance programs must be paired with resilience strategies rather than treating controls as a complete solution.
🏢 2. What This Means for Your Business: The Compliance Obligations Most Companies Miss
Most organizations that have begun to grapple with AI export compliance have focused on the obvious cases: chip manufacturers, cloud providers, and organizations with direct commercial relationships in China. The more challenging and more commonly overlooked compliance exposures arise in organizations that consider themselves downstream consumers of AI technology rather than participants in the AI supply chain — a framing that is increasingly incorrect and increasingly risky. The full landscape of AI regulation in 2026 makes clear that compliance obligations extend far beyond traditional technology exporters to encompass virtually any organization that procures, deploys, or sells AI-enabled products or services internationally. The BIS’s expanded enforcement mandate and increased FY2026 budget make this not a theoretical concern but an active enforcement priority.
The Downstream Compliance Reality: Most organizations that will receive BIS enforcement attention in 2026 and 2027 are not chip manufacturers. They are data center operators, cloud service customers, SaaS providers, and AI tool resellers who assumed they were outside the export control perimeter — and discovered they were not.
The Supply Chain Problem — You May Be Non-Compliant Without Knowing It
Most businesses that use AI tools, cloud AI platforms, or AI-enabled hardware do not know the origin of the chips powering those services — and in 2026, that knowledge gap creates genuine compliance exposure. If your cloud AI provider uses restricted components in a jurisdiction-violating configuration, or if a vendor in your AI hardware supply chain has a beneficial ownership connection to an Entity List company, you may have indirect exposure even though you are not the exporter of record. The “know your customer” and “know your supplier” obligations under BIS’s Export Administration Regulations apply downstream as well as upstream — the obligation does not end at your direct vendor relationship but extends to what you can reasonably know about your supply chain’s ultimate provenance.
The practical action this requires is more specific than simply asking vendors about their compliance programs. It means requesting chip provenance documentation from AI infrastructure vendors as a standard element of vendor due diligence — including which specific chip models power the AI services you consume, where those chips were manufactured, and whether the vendor has completed Entity List screening for their own supply chain. This documentation request should be a standard element of every AI vendor contract and renewal negotiation. Our AI Vendor Due Diligence Checklist provides the complete framework for structuring these vendor assessments, including the specific questions that surface export control exposure in AI supply chains.
The SaaS and API Risk — Selling AI Services Across Borders
If your business provides AI-powered SaaS products or API services, exporting those services to restricted countries or sanctioned entities is a violation — even if no physical product crosses a border. Software-as-a-service is explicitly covered under US export control regulations: providing access to controlled AI software through an API is legally equivalent to exporting that software for export control purposes. A single API call from a sanctioned jurisdiction can constitute an export violation if the underlying AI software is subject to export controls and the end-user is in a restricted destination. The geographic indirection of cloud service access — customers routing requests through VPNs, third-country proxies, or distributed infrastructure — does not eliminate the compliance obligation; it creates a due diligence requirement to implement geo-restriction controls and customer screening that makes the service provider’s best-effort compliance demonstrable.
Organizations that provide AI-powered services internationally should implement a geo-restriction control layer that blocks service access from comprehensively sanctioned jurisdictions (Iran, North Korea, Cuba, Syria, and Russia under various OFAC program categories), maintain a customer screening process against the OFAC SDN list and the BIS Entity List for enterprise customers, and document these controls as evidence of good-faith compliance that reduces penalty exposure in enforcement scenarios. The absence of any screening or geo-restriction controls is the compliance posture that creates the highest enforcement risk — not because every API call from a restricted jurisdiction will be prosecuted, but because the documented absence of controls eliminates the good-faith compliance defense that typically results in reduced penalties rather than maximum enforcement actions.
The Talent and Research Risk — Hiring and Collaboration
A compliance exposure that most technology organizations have not yet incorporated into their AI governance programs is the “deemed export” risk — the principle that sharing controlled AI technology with a foreign national inside the United States constitutes an export to that person’s country of citizenship, potentially requiring the same export license that a physical export would require. This applies to research collaborations, open-source AI contributions, hiring decisions, and any professional interaction where controlled AI technology — including certain AI software, model architecture documentation, and training methodologies — is shared with a national of a restricted country. US universities and research institutions with AI programs are facing growing deemed export compliance complexity as the scope of controlled AI technology expands, and corporate AI research teams face the same obligations when their work involves controlled technology categories.
| Business Activity | Export Control Risk | Action Required |
|---|---|---|
| Purchasing AI cloud services | ⚠️ Medium — chip provenance gap | Request vendor compliance documentation confirming Entity List screening and chip origin |
| Selling AI SaaS internationally | 🔴 High — service export rules | OFAC/Entity List screening before customer onboarding; geo-restriction controls for sanctioned jurisdictions |
| Hiring AI researchers | 🟠 Medium — deemed export risk | Legal review for nationals of restricted countries working on controlled AI technology |
| Open-source AI contributions | 🟠 Medium — deemed export risk | Contribution policy review with export control counsel; assess controlled technology scope |
| Using AI APIs in global products | 🔴 High — jurisdiction exposure | Geo-restriction implementation + customer screening protocol for all international deployments |
| Sourcing AI hardware | 🟠 Medium — supply chain risk | Chip provenance documentation + beneficial ownership screening for hardware vendors |
1. 🗺️ The AI Geopolitics Landscape: Six Major Risk Vectors
AI geopolitical risk is not a single, monolithic threat but a complex of distinct risk vectors that affect different organizations in different ways depending on their technology stack, geographic footprint, customer base, and supply chain structure. Understanding the distinct risk vectors allows organizations to assess their specific exposure rather than treating “AI geopolitical risk” as an undifferentiated concept that applies equally to everyone.
| Risk Vector | Description | Who Is Most Affected | Current Status (2026) |
|---|---|---|---|
| Semiconductor Export Controls | US and allied restrictions on advanced AI chip exports to China, Russia, and designated entities | Chip manufacturers, cloud providers, organizations with Chinese or Russian supply chain exposure | 🔴 Actively Enforced |
| AI Software and Model Restrictions | Restrictions on exports of AI software, model weights, and training technology to controlled jurisdictions | AI software developers, cloud AI service providers, organizations with multinational AI deployments | 🟠 Expanding Rapidly |
| Cloud Service Blocking | Restrictions on providing cloud AI services to sanctioned countries or entities; reciprocal blocking by China | Cloud service providers, organizations relying on cloud AI for international operations | 🔴 Actively Enforced |
| Data Localization Requirements | National requirements that AI training data, model weights, and inference outputs cannot leave national boundaries | Multinational organizations, AI SaaS providers, organizations using cross-border data flows | 🟠 Growing Significantly |
| Rare Earth and Materials Supply | Chinese export controls on rare earth elements and processing technology critical to semiconductor manufacturing | Semiconductor manufacturers, electronics supply chains, any organization dependent on semiconductor availability | 🟠 Active and Escalating |
| AI Standards Fragmentation | Diverging AI regulatory frameworks, certification requirements, and technical standards across US, EU, and China | Global technology companies, AI developers deploying across multiple regulatory jurisdictions | 🟡 Developing Rapidly |
2. 🔧 The Semiconductor Export Control Architecture
The most consequential and most immediately operational AI geopolitical risk for most technology-dependent organizations is the architecture of semiconductor export controls that the United States, with varying participation from allies including Japan, the Netherlands, and South Korea, has constructed around the advanced chip technology required to train and deploy frontier AI systems. Understanding this architecture — not just the specific rules but the logic and trajectory of the control regime — is essential for making sound AI infrastructure decisions in 2026 and planning for how the landscape will evolve.
The October 2022, October 2023, and October 2024 Rule Sets
The current export control architecture for AI-related semiconductors was built in three major rule-making actions, each more comprehensive than the previous one. The October 2022 rules imposed restrictions on exports of advanced logic chips and semiconductor manufacturing equipment to China, targeting chips above specific performance thresholds measured in total performance (measured in billions of operations per second) and interconnect speed. The rules also restricted the export of chips produced anywhere in the world using US technology — a foreign direct product rule that extended US jurisdiction to chips made by non-US manufacturers using US-origin equipment or intellectual property.
The October 2023 rules expanded the control architecture substantially — adding chips from additional manufacturers, closing the “loopholes” through which controlled chips had continued to flow to China via third countries, creating a three-tier country classification system that subjected exports to different licensing requirements based on the destination country’s relationship with the United States, and extending controls to additional semiconductor manufacturing equipment categories. The October 2024 rules took the architecture further still — imposing comprehensive controls on the export of advanced AI software, including in some cases large language model weights, to controlled destinations, and adding new provisions targeting the network of distributors and logistics companies that had been facilitating the circumvention of earlier rounds of controls.
The Practical Effect on Global AI Development
The practical impact of these controls on China’s AI development has been significant but not as decisive as some US policymakers initially hoped, for several reasons that inform understanding of how the technology competition is likely to evolve. Chinese chip designers — led by Huawei’s HiSilicon and emerging companies including Cambricon and Biren Technology — have made faster progress in designing domestically producible AI chips than the US control architecture anticipated. Chinese manufacturers have also continued to access some level of controlled chips through the network of third-country distributors and front companies that enforcement actions have not fully disrupted. And Chinese AI researchers have demonstrated that for many applications, models trained on somewhat less capable chips can approach the performance of frontier models trained on the most advanced available hardware — raising questions about whether the chip control strategy can achieve its stated goal of preventing China from developing competitive frontier AI capabilities.
For non-Chinese and non-Russian organizations, the export controls create compliance obligations and supply chain management requirements rather than direct denial of chip access — but these obligations are more complex than they appear at first assessment. Organizations that manufacture products incorporating controlled chips, that provide cloud computing services to international customers, or that have supply chains passing through controlled jurisdictions must navigate the export control requirements carefully to avoid inadvertent violations. The Bureau of Industry and Security (BIS) enforcement actions taken against organizations that violated the chip export controls in 2024 and 2025 — including significant financial penalties and in some cases criminal referrals — demonstrate that the enforcement posture is serious and that compliance negligence carries genuine organizational risk. According to BIS’s export enforcement program, civil penalties for export control violations can reach twice the value of the transaction or $1 million per violation — whichever is greater — and criminal penalties can include substantial fines and imprisonment for responsible individuals.
Allied Coordination and the Multilateral Control Architecture
The effectiveness of the US semiconductor export control strategy depends critically on allied coordination — because chips and manufacturing equipment produced by Japanese, Dutch, South Korean, and Taiwanese manufacturers are equally capable of training frontier AI models and would simply substitute for US-produced items in Chinese supply chains if not subject to equivalent restrictions. The Wassenaar Arrangement — the multilateral export control regime covering conventional arms and dual-use goods including semiconductors — provides the legal framework within which allied coordination on chip controls operates, but achieving and maintaining allied alignment on the specific scope and timing of restrictions has required intensive diplomatic engagement that has not always produced complete agreement on pace or scope.
The Netherlands’ restrictions on ASML — the sole global supplier of extreme ultraviolet lithography machines essential for manufacturing the most advanced semiconductor nodes — represent the most strategically significant allied contribution to the chip control architecture. ASML’s EUV equipment cannot be exported to China without Dutch government license, and Dutch authorities have declined to issue these licenses under strong US encouragement. This single restriction, covering equipment that no other company in the world can supply, is arguably as significant as all the chip-specific export controls combined in limiting China’s ability to domestically manufacture the most advanced AI chips. The strategic significance of a single Dutch company to the global AI competition is a striking illustration of the interconnected and fragile nature of the semiconductor supply chain that undergirds all AI capability.
3. 🤖 AI Software, Models, and the Emerging Digital Frontier
While semiconductor export controls have dominated coverage of AI geopolitics, a rapidly developing second front in the AI technology competition concerns AI software, model weights, and the knowledge embedded in trained AI systems. The question of whether large language model weights — the mathematical parameters that encode everything a trained AI model has learned — constitute exportable technology subject to export control has been actively debated within the US government and is increasingly being resolved in favor of control for the most capable models.
Model Weight Export Controls: The Emerging Framework
The October 2024 export control rules for the first time explicitly included provisions addressing the export of certain AI model weights, establishing a framework for controlling the transfer of trained AI models to controlled jurisdictions. The specific thresholds and scope of these controls — which models are covered, what “export” means for a model that can be downloaded, how to think about models accessible through API versus models distributed as downloadable weights — are areas of ongoing regulatory development that are creating significant compliance uncertainty for AI developers.
The policy challenge of controlling AI model exports is significantly more complex than controlling physical chips. A chip cannot be downloaded through the internet; a set of model weights can. A chip manufacturer can be required to verify the end-user before shipment; an API that provides inference access to a model cannot practically verify the physical location and sanctioned status of every request at the scale at which modern AI APIs operate. These enforcement challenges have led some export control experts to be skeptical that model controls can be effectively enforced, while others argue that even imperfectly enforceable controls create meaningful friction that serves policy objectives even without perfect compliance.
Open-Source AI and the Control Challenge
The open-source AI ecosystem — models like Meta’s Llama family, Mistral’s models, and the hundreds of community-developed models available through Hugging Face and similar repositories — creates a specific challenge for AI export control that reflects the fundamental tension between the US’s open technology culture and its strategic interest in limiting adversary access to AI capability. Models that have been publicly released under open licenses cannot be effectively recalled or restricted once released — they are globally available to anyone with the computational resources to download and run them, including entities in controlled jurisdictions that the export control framework is intended to restrict.
The policy debate around whether and how to restrict open-source AI model releases is one of the most contested in current US AI governance. Arguments for restriction note that the most capable open-source models are approaching the performance of frontier closed-source models and can be fine-tuned for specific applications — including weapons development — that create genuine national security concerns. Arguments against restriction note that open-source AI has produced enormous beneficial innovation, that restricting US open-source releases would cede the open-source AI leadership to non-US actors who face no equivalent restrictions, and that the enforcement challenges are so significant that restrictions would achieve little practical security benefit while imposing large costs on domestic innovation. The framework for open-source versus closed-source AI deployment provides useful context for understanding why this question has both technical and geopolitical dimensions that resist simple answers.
4. ☁️ Cloud AI Services and the Sanctions Compliance Challenge
For most organizations that access AI capabilities through cloud service providers rather than training models on owned infrastructure, the primary geopolitical compliance concern is not semiconductor export controls but rather the cloud service provider’s sanctions compliance obligations — and the implications of those obligations for service availability, data handling, and operational continuity. Cloud AI services are subject to comprehensive sanctions regimes that restrict providers from serving customers in sanctioned jurisdictions or from serving entities on designated party lists regardless of where those entities are legally incorporated.
OFAC Compliance and the AI Service Provider Obligation
The US Treasury Department’s Office of Foreign Assets Control (OFAC) administers comprehensive sanctions programs that restrict US persons and US-nexus service providers from engaging in transactions with sanctioned countries — including Iran, North Korea, Cuba, Syria, and Russia under various program categories — and with specifically designated individuals and entities on the SDN (Specially Designated Nationals and Blocked Persons) list. For AI service providers, OFAC compliance means maintaining the technical and procedural infrastructure to screen customers, verify their sanctions status, and terminate service when sanctions exposure is identified — a requirement that has become significantly more complex as AI services have proliferated and as customers access them through increasingly indirect pathways.
The practical compliance challenge for AI service providers is the geographic indirection of cloud service access. A customer accessing an AI API may be routing their traffic through multiple cloud layers, VPN services, or third-country intermediaries in ways that make their actual physical location and ultimate beneficial ownership difficult to determine from the API request alone. OFAC expects service providers to implement reasonable due diligence appropriate to the risk profile of the service — which for high-capability AI services with national security applications means more thorough customer verification than for general-purpose web services. Organizations that receive AI services through enterprise agreements are typically screened at contract initiation; organizations accessing AI through self-service APIs may receive less thorough initial screening, creating compliance gaps that enforcement actions have targeted.
Reciprocal Blocking: China’s Great Firewall and AI Services
The United States is not the only source of AI access restrictions in the current geopolitical environment. China’s internet censorship infrastructure — the “Great Firewall” — blocks access to most major Western AI services including ChatGPT, Claude, Gemini, and the majority of AI tools built on these models. Chinese users who access Western AI services do so through circumvention tools — VPNs and proxy services — that are technically illegal under Chinese law but tolerated at varying levels of enforcement intensity depending on the political moment.
For multinational organizations operating in China, the blocking of Western AI services creates operational implications that require explicit planning. Research teams, engineering departments, and business units in China cannot access the same AI productivity tools as their colleagues in the US, Europe, or other markets — creating a two-tier capability environment within the same organization that affects research productivity, software development velocity, and the consistency of AI-assisted workflows. Organizations address this through a combination of China-compliant AI services (domestic Chinese AI platforms including Baidu’s ERNIE, Alibaba’s Qianwen, and Zhipu AI’s ChatGLM have developed rapidly and can substitute for Western services in many use cases), local deployments of open-source AI models that do not require internet access to Western services, and in some cases VPN access for sensitive research and development functions where Western AI capability provides material advantage.
The India, Middle East, and Southeast Asia Complexity
The binary US-China framing of AI geopolitics obscures the complexity facing organizations operating in the significant portion of the world that sits outside both major technology blocs and that is actively navigating relationships with both. India’s AI ecosystem is receiving enormous US government and corporate investment while maintaining long-standing defense and technology relationships with Russia — creating a complex compliance environment for organizations serving Indian customers or operating Indian facilities that handle both US-origin technology and Russia-adjacent relationships. The UAE’s position as a significant AI hub attracting both US and Chinese technology investment while maintaining Gulf Cooperation Council relationships that include states under US sanctions creates similar complexity for organizations with UAE-based operations.
These “middle power” jurisdictions — large, strategically significant technology markets that are not straightforwardly aligned with either the US or Chinese technology blocs — represent the most genuinely complex compliance environment for multinational organizations. The legal analysis required to determine when a specific technology transfer involving a middle-power jurisdiction creates export control or sanctions exposure requires expert legal input that cannot be summarized in generalized guidance, and organizations operating in these markets should treat engagement with qualified export control counsel as a baseline operational requirement rather than an exceptional response to specific incidents.
📰 Want to stay current on AI? Browse the AI Buzz News & Trends Hub — curated analysis of the latest AI market shifts, geopolitics, workforce impact, and industry trends shaping 2026.
5. 🔗 AI Supply Chain Risk Assessment: Mapping Your Exposure
Effective management of AI geopolitical risk requires understanding your organization’s specific supply chain dependencies at a granularity that most technology teams have not previously needed to develop. The question is not whether your organization uses AI — in 2026, virtually every significant organization does — but which specific AI components, from which specific vendors, manufactured with which specific inputs, create geopolitical exposure that could affect operational continuity, compliance standing, or competitive position.
The Four-Layer AI Supply Chain
Understanding AI supply chain risk requires mapping across four distinct layers that together constitute the complete supply chain for any AI capability your organization depends on. Each layer has different geopolitical risk characteristics that need to be assessed separately rather than assumed to be equivalent.
Layer 1 — Hardware and Semiconductors: The physical compute infrastructure that runs AI workloads — GPUs, AI accelerators, and the servers they are installed in — has the most direct and most documented geopolitical risk exposure. NVIDIA’s H100 and H200 GPUs, AMD’s MI300X accelerators, and Intel’s Gaudi series AI accelerators are all subject to US export controls for specific destinations. The supply chain for these chips — from TSMC’s fabrication in Taiwan through packaging and assembly in various Asian countries to final delivery — runs through multiple jurisdictions with distinct geopolitical risk profiles. Organizations that own or plan to purchase GPU hardware should map the specific chip models and manufacturing origins of their hardware infrastructure to understand which export control rules apply to their procurement decisions and which supply chain disruption scenarios could affect hardware availability.
Layer 2 — Cloud Infrastructure: Organizations that access AI capabilities through cloud providers are inheriting the geopolitical risk profile of those providers’ infrastructure decisions, data center locations, and compliance postures. A cloud provider that has significant infrastructure in jurisdictions subject to data localization requirements, that relies on semiconductor supply chains with Chinese manufacturing exposure, or that operates under legal frameworks that give foreign governments potential access to customer data creates specific risks for customers whose sensitivity to these factors varies by their own regulatory environment and risk tolerance. Cloud infrastructure geopolitical risk assessment should identify the specific data center regions where workloads run, the legal jurisdiction of the cloud provider’s primary operating entity, and the provider’s documented compliance posture regarding sanctions, data localization, and government data access requests.
Layer 3 — AI Models and Services: The AI models your organization uses — whether through API access to frontier models from OpenAI, Anthropic, or Google, through open-source model deployments, or through AI-powered SaaS applications built on these models — represent a distinct layer of geopolitical risk. Model availability is subject to the service provider’s sanctions compliance policies, which may change in response to regulatory developments in ways that affect service continuity. Model training data provenance may create legal exposure in jurisdictions with data sovereignty requirements. And the intelligence embedded in AI models — the knowledge that enables their capabilities — may itself be subject to emerging controls that affect how models can be legally transferred or accessed across jurisdictional boundaries.
Layer 4 — Data and Knowledge Flows: The data that flows into and out of AI systems — training data, inference inputs, model outputs — creates the fourth layer of geopolitical risk. Data flows across borders may be subject to data localization requirements that prohibit specific transfers, to import/export controls on specific categories of sensitive data, or to the terms of data sharing agreements with governments or research institutions that impose geographic restrictions on data use. Organizations building AI systems that depend on cross-border data flows need to map those flows explicitly against the applicable legal frameworks in each jurisdiction involved — a task that requires legal analysis in multiple jurisdictions simultaneously and that is becoming more complex as both data localization requirements and AI-specific data governance rules proliferate.
Conducting an AI Geopolitical Risk Audit
A practical AI geopolitical risk audit follows the four-layer framework above to document the organization’s current supply chain dependencies and identify where those dependencies create exposure to specific geopolitical scenarios. The audit should produce, for each layer, a list of the specific vendors, models, data sources, and infrastructure components the organization depends on; the jurisdictions of manufacture, operation, and data storage for each; the specific sanctions, export control, and data governance requirements applicable to each; and an assessment of the organization’s exposure if specific geopolitical scenarios — US-China trade decoupling, sanctions expansion, supply chain disruption — were to materialize.
The output of the audit is not a binary “we are exposed / we are not exposed” assessment but a risk map that identifies where the organization’s dependencies are concentrated, which scenarios would have the most operational impact, and which mitigation investments would provide the most risk reduction per dollar invested. This risk map becomes the foundation for the resilience investments described in the next section. Our guide to AI Risk Assessment provides the evaluation methodology framework that informs this kind of supply chain risk assessment.
6. 🛡️ The Resilience Framework: Building AI Supply Chain Security
The appropriate response to AI geopolitical risk is not paralysis or withdrawal from AI investment — AI capability is too central to competitive position and operational effectiveness for any serious organization to make that choice. The appropriate response is deliberate resilience planning that reduces concentrated dependencies, builds operational flexibility, and maintains compliance discipline — creating an AI architecture that can sustain operations across a broader range of geopolitical scenarios than a single-vendor, single-jurisdiction approach would permit.
Diversification Across Providers and Geographies
The single most effective structural resilience strategy is avoiding single-vendor dependencies for critical AI capabilities — maintaining the ability to operate with alternative providers if a specific vendor becomes unavailable due to sanctions, export controls, service disruptions, or policy changes. For cloud AI services, this means maintaining tested integrations with multiple providers — not just primary and backup configurations on paper, but regularly exercised alternative pathways that the operations team can actually execute when needed. For frontier AI model access, it means maintaining the technical capability to switch between models from different providers, including open-source models that can be self-hosted if cloud API access becomes unavailable.
Geographic diversification of AI infrastructure — deploying AI workloads across data centers in multiple jurisdictions rather than concentrating in a single region or a single cloud provider’s infrastructure — provides resilience against both service disruptions and regulatory changes that affect specific geographic markets. This diversification strategy aligns naturally with data sovereignty objectives: organizations that need to comply with data localization requirements in multiple jurisdictions will naturally develop multi-region AI deployments that provide geographic resilience as a byproduct of compliance architecture.
On-Premises and Sovereign AI Deployment Capability
For organizations with the highest sensitivity to AI supply chain risk — critical infrastructure operators, defense contractors, organizations handling data subject to stringent sovereignty requirements — developing the capability to run AI workloads on owned or leased on-premises infrastructure rather than relying entirely on cloud services provides the deepest resilience against service disruptions driven by geopolitical events. On-premises AI deployment using open-source models eliminates dependency on cloud service providers’ sanctions compliance policies, avoids data sovereignty risks associated with cross-border cloud data flows, and provides operational continuity regardless of geopolitical developments affecting cloud service availability.
The Sovereign AI and Resilience framework provides the detailed technical and organizational guidance for building genuinely self-sufficient AI capabilities that can sustain operations through the range of disruption scenarios that geopolitical risk planning must address. The investment required for meaningful on-premises AI capability is significant — GPU hardware, software stack maintenance, MLOps capability — but for organizations where AI capability disruption would have severe operational consequences, this investment represents prudent resilience spending rather than optional enhancement.
Compliance Infrastructure and Legal Expertise
Building the compliance infrastructure to navigate AI geopolitical regulations as they evolve requires investment in both human expertise and process infrastructure that many technology organizations have not previously needed. Export control compliance for AI-related products and services requires legal expertise in multiple regulatory regimes — BIS Export Administration Regulations, OFAC sanctions programs, EU dual-use regulations, and equivalent national-level controls in relevant operating jurisdictions — that most technology legal teams did not have before AI became a trade policy priority. Organizations that have not yet built this expertise should assess whether their current legal capacity is adequate for the compliance obligations they face and engage specialized export control counsel for the gap analysis if they are uncertain.
On the process side, compliance infrastructure for AI supply chain risk includes: vendor screening processes that verify the sanctions status of AI service providers and their principals; transaction monitoring that identifies when AI-related transactions involve sanctioned jurisdictions or entities; technology classification processes that determine which AI components require export licenses for specific destinations; and a policy update process that keeps compliance procedures current as the regulatory landscape evolves. These processes must be integrated into procurement, product development, and commercial operations workflows — not maintained as separate compliance functions that operate in isolation from the business decisions they are supposed to govern.
7. 🌐 The Technology Decoupling Scenarios: Planning for Different Futures
Effective geopolitical risk planning for AI supply chains requires thinking explicitly about the range of future scenarios that could materialize — not just the current state of the regulatory environment — because the decisions organizations make now about AI architecture will persist for years and must be robust to futures that look different from today’s baseline. The following scenarios represent distinct potential futures that organizations should consider in their planning.
Scenario 1: Managed Decoupling (Most Likely Near-Term)
The most likely near-term scenario is a continuation of the current managed decoupling trajectory — successive rounds of export control tightening that progressively limit China’s access to the most advanced AI hardware and software, while maintaining enough economic interdependence in other areas that full technology separation is avoided. In this scenario, Chinese AI development continues with domestically produced chips and locally compliant AI tools, creating a divergent AI ecosystem with different capability profiles for different applications but with both ecosystems continuing to advance. For organizations operating in both markets, this scenario requires maintaining separate AI stacks for China-market and rest-of-world operations — a complexity cost that most large multinationals have already accepted as a baseline planning assumption.
Scenario 2: Accelerated Decoupling (Significant Risk)
A significant risk scenario involves acceleration of the decoupling trajectory — triggered by geopolitical events including a Taiwan Strait crisis, a major cybersecurity incident attributed to state actors, or a dramatic advancement in Chinese AI military capability that prompts emergency export control expansion. In this scenario, existing controls are substantially tightened in compressed timelines, potentially including restrictions that affect organizations currently able to operate comfortably within existing controls. Organizations that have concentrated their AI infrastructure in specific vendors or jurisdictions, or that have significant commercial relationships with Chinese technology companies, would face the most severe operational disruptions in this scenario.
Scenario 3: Regulatory Fragmentation Without Full Decoupling
A third significant scenario is regulatory fragmentation without full technology decoupling — a world in which AI regulatory frameworks diverge dramatically across major jurisdictions (EU, US, China, India, and emerging regulatory blocs), creating compliance complexity that affects organizations operating across these jurisdictions even without the supply chain disruptions of the decoupling scenarios. The EU’s AI Act, China’s Generative AI regulations, India’s proposed AI framework, and the US’s emerging sector-specific AI rules represent the early stages of this fragmentation — which may intensify into genuinely incompatible regulatory requirements that force organizations to maintain jurisdiction-specific AI deployments and compliance postures. Our guide to the EU AI Act provides the detailed regulatory framework for the most developed of these jurisdiction-specific compliance requirements.
8. 🔮 The Chinese AI Domestic Development Track: What Organizations Need to Know
A dimension of AI geopolitics that is often underappreciated in Western business planning is the pace and scope of Chinese domestic AI development — which is advancing faster than many Western analysts predicted and which is creating a Chinese AI ecosystem that, while not yet equivalent to the frontier capabilities of leading Western models in all domains, is viable for a growing range of commercial and government applications. Organizations operating in China or serving Chinese markets need to develop a realistic assessment of Chinese AI capabilities rather than assuming that Western AI services, if somehow accessible, are necessary for their Chinese operations.
Chinese Frontier Models: The Capability Trajectory
Chinese AI laboratories — including those operated by Baidu, Alibaba, Tencent, ByteDance, Zhipu AI, Moonshot AI, and state-affiliated research institutes — have released a series of large language models that have progressively narrowed the capability gap with Western frontier models. Chinese models in 2026 demonstrate strong performance on Chinese-language tasks (where training data advantages are significant), competitive performance on coding and mathematical reasoning tasks that have become benchmarks for evaluating frontier model capability, and improving performance on general reasoning and instruction following that has historically been an area of Western model advantage.
The relevance of this capability trajectory for business planning is that organizations with China operations should evaluate Chinese AI tools as potentially viable alternatives to Western services for many use cases — not from an ideological preference but from a practical risk management perspective. An operation that depends on Western AI services that are either blocked in China or accessible only through technically illegal circumvention methods has a more fragile AI infrastructure than one that has evaluated and tested Chinese alternatives that operate without legal or technical barriers within China’s regulatory environment.
The Huawei AI Chip Situation
Huawei’s Ascend series AI accelerators — developed in response to the export control restrictions that cut off Huawei from NVIDIA hardware — have advanced to the point where they are being used in commercial AI training and inference operations in China despite their performance limitations relative to NVIDIA’s current generation H100 and H200 GPUs. The Ascend 910B and subsequent iterations provide viable training capability for AI models at Chinese scale, supporting the domestic Chinese AI ecosystem in ways that the US export control regime’s architects underestimated. For organizations evaluating AI supply chain risk, the demonstrated viability of Ascend-based AI training means that Chinese AI development will continue on a credible domestic trajectory regardless of the success of the chip export control strategy — a reality that affects the medium-term competitive dynamics of the global AI industry.
⚖️ 9. The 2026 Regulatory Stack: Frameworks Every Compliance Team Needs
The landscape of regulatory frameworks governing AI technology exports has grown substantially more complex in 2026. Organizations that mapped their compliance obligations based on the 2023 or 2024 regulatory landscape are operating on outdated assessments — the January 2026 BIS rule revision, the EU’s accelerating dual-use control updates, and the November 2026 Affiliates Rule resumption deadline all require compliance posture reviews this year. For the complete picture of how these frameworks interact with broader AI governance obligations, our guide to AI Regulation in 2026 and the Colorado AI Act Explained provide the complementary domestic compliance context that export control programs must integrate with.
The Wassenaar Inflection Point: The Wassenaar Arrangement was built for weapons. In 2026, AI foundational models are being actively debated for explicit inclusion — a shift that would create export license requirements for the world’s most capable AI systems across all 42 participating member states simultaneously. Organizations that treat Wassenaar as background context rather than active compliance risk are underestimating the pace of this regulatory evolution.
The EU dimension of this regulatory stack is evolving on a compressed timeline. The European Commission updated the dual-use export control list in Annex I of Regulation (EU) 2021/821 on September 8, 2025, with enforcement intensifying in 2026. EU draft AI export control options began circulating among member states in early 2026, with proposed thresholds targeting AI accelerators exceeding roughly 300 TFLOPS — a threshold that would capture the most capable AI chips used in commercial training operations. The EU’s approach emphasizes aligning export controls with the AI Act and cybersecurity rules to create coherent governance over AI development and cross-border technology transfers, rather than implementing standalone chip-focused restrictions. This integration approach means EU-based organizations face compliance obligations that span multiple regulatory frameworks simultaneously — export control, AI Act deployer obligations, and GDPR data governance requirements may all apply to the same AI system.
| Framework | Administered By | Covers | Penalty |
|---|---|---|---|
| Export Administration Regulations (EAR) | U.S. BIS (23% budget increase in FY2026) | AI chips, software, technology; ECCN-classified items; deemed exports to foreign nationals | Up to $1M per violation or 2× transaction value; criminal prosecution |
| OFAC Sanctions Programs | U.S. Treasury / OFAC | Financial transactions with sanctioned entities; AI service provision to SDN-listed persons and blocked jurisdictions | Civil + criminal; disgorgement of profits; reputational action |
| EU Dual-Use Regulation (2021/821) | European Commission / member states | Dual-use AI technology; cyber-surveillance tools; updated Sept 2025; draft AI-specific controls in 2026 | Member state enforcement — ranges from fines to criminal prosecution by jurisdiction |
| UK Strategic Export Controls | UK DIT / ECJU (post-Brexit independent list) | UK-listed dual-use technology; broadly EU-aligned but diverging in some AI categories | Criminal prosecution; up to 10 years imprisonment for serious violations |
| Wassenaar Arrangement | 42 member states — multilateral coordination body | Dual-use goods and technologies; AI foundational models under active debate for inclusion | Via member state implementing law — penalties vary by jurisdiction |
The compliance implication of this multi-framework landscape is that organizations cannot rely on compliance with one framework as a proxy for compliance with others. A US-headquartered organization that is BIS-compliant may still face OFAC exposure from AI service provision to a non-sanctioned customer with SDN-listed beneficial owners. An EU-based organization compliant with Regulation 2021/821 may face additional UK export licensing obligations for the same technology transfer. And both organizations may face Wassenaar-derived obligations in the specific member states where they operate. The only defensible compliance posture is a comprehensive mapping of all applicable frameworks across all jurisdictions where the organization operates, procures, sells, or transfers AI technology — a mapping that requires qualified multi-jurisdictional legal expertise and regular updating as both the regulatory frameworks and the organization’s activities evolve. Our AI Governance Explained guide provides the accountability structure for organizing this multi-framework compliance program.
9. 📋 Compliance Checklist: What Organizations Must Do Now
The complexity of the AI geopolitical and sanctions landscape can feel paralyzing — but the practical compliance and risk management steps that organizations must take are clear and achievable. The following checklist provides the baseline actions that every organization with significant AI-related operations should have completed or have in active progress.
| Priority | Action | What This Involves | Who Owns It |
|---|---|---|---|
| P1 — Immediate | Complete AI supply chain audit across all four layers | Document all AI hardware, cloud providers, models, and data flows with jurisdiction mapping for each component | CTO / Chief Compliance Officer |
| P1 — Immediate | Engage qualified export control legal counsel | Retain counsel with specific expertise in BIS, OFAC, and EU dual-use regulations as applied to AI technology | General Counsel |
| P1 — Immediate | Implement vendor and customer sanctions screening | Screen all AI-related vendors and customers against OFAC SDN list; establish ongoing monitoring for list changes | Compliance / Legal |
| P2 — 90 Days | Classify AI products and services under export control schedules | Determine ECCN or EAR99 status for all AI products, services, and technology transfers with legal counsel guidance | Compliance / Legal / Technical |
| P2 — 90 Days | Develop China operations AI strategy | Evaluate Chinese AI alternatives; determine VPN policy; establish compliance framework for operating in the blocked AI service environment | CTO / Regional Operations / Legal |
| P2 — 90 Days | Identify AI supply chain concentration risks | Map single-vendor and single-jurisdiction dependencies; prioritize diversification investments based on criticality and disruption probability | CTO / Supply Chain |
| P3 — 6 Months | Build alternative provider capability and test failover | Establish tested integrations with backup AI service providers; exercise failover procedures; evaluate open-source alternatives for critical functions | Engineering / Operations |
| P3 — 6 Months | Establish regulatory monitoring program | Subscribe to BIS, OFAC, and EU regulatory update services; assign responsibility for monitoring and distributing updates; establish internal escalation process for material changes | Compliance / Legal |
✅ 10. The AI Geopolitics Compliance Checklist: What to Do in the Next 90 Days
The preceding sections describe what the regulations require and what the risks are. This section translates those requirements into a structured 90-day action program that converts a reactive, incident-driven compliance posture into a proactive, evidence-based one. Most organizations that will face BIS or OFAC enforcement attention in 2026 and 2027 are not organizations that made deliberate decisions to violate export controls — they are organizations that had no structured compliance process, made no deliberate decisions either way, and discovered their exposure only when a transaction or incident triggered scrutiny. A 90-day structured compliance program addresses the four critical areas that enforcement authorities examine first: inventory, screening, controls, and governance. For the AI tool governance layer that sits above these export compliance controls, the AI Audit Checklist and the Corporate AI Policy template provide the internal governance documents that make the compliance posture operationally enforceable.
The Cost of Reactive Compliance: The cost of proactive AI export compliance — legal fees, staff time, and screening tools — is a small fraction of a single enforcement action. BIS enforcement actions in 2024 and 2025 resulted in penalties ranging from $500,000 to $300 million for organizations that failed to implement the screening and due diligence controls that are now standard expectations for AI technology companies. Building the program now costs less than defending one enforcement action.
Days 1–30: Inventory and Risk Assessment
The first 30 days focus exclusively on visibility — you cannot screen what you have not identified, cannot control what you have not mapped, and cannot assess risk in supply chains you have not documented. The deliverables from this phase are the inputs to every subsequent compliance activity: an AI asset register, a jurisdiction risk map, and a deemed export risk assessment. These documents do not need to be comprehensive on day one — they need to be accurate for the highest-risk assets, and completeness can be built iteratively.
Days 31–60: Controls and Screening
The second 30 days convert the risk map from the first phase into active controls. Customer list screening against OFAC and BIS Entity Lists is typically the fastest control to implement — it requires a screening tool, a customer data extract, and a process for handling matches. Geo-restriction implementation for AI SaaS and API services is the second priority — the technical implementation varies by platform, but the policy decision (which jurisdictions to restrict) should be made by legal counsel based on the applicable OFAC program categories and BIS controlled-country tiers. Chip provenance documentation requests go to vendors as part of contract renewal or new vendor onboarding — they do not require waiting for the next procurement cycle.
Days 61–90: Governance and Ongoing Monitoring
The final 30 days establish the governance infrastructure that keeps the compliance program current as both the regulatory landscape and the organization’s activities evolve. A published internal AI export compliance policy — reviewed and approved by legal counsel — creates the documented governance foundation that demonstrates organizational commitment to compliance and provides the internal authority for the screening and control procedures implemented in phase two. Staff training for the functions with the most direct exposure — procurement, sales, engineering, and HR — converts the policy from a document into an operational practice. A quarterly Entity List screening schedule ensures that the SDN and Entity Lists — which are updated frequently — are reflected in customer and vendor screening on an ongoing basis rather than only at initial onboarding.
| Days | Action | Owner | Output |
|---|---|---|---|
| 1–30 | Inventory all AI tools, platforms, and hardware in use | IT + Procurement | AI asset register with vendor, chip origin, and jurisdiction data |
| 1–30 | Map all countries where AI services are sold or delivered | Legal + Sales | Jurisdiction risk map with applicable framework identification |
| 1–30 | Identify all foreign national staff with AI system access | HR + Legal | Deemed export risk assessment by role and nationality |
| 31–60 | Screen customer list against OFAC SDN + BIS Entity List | Legal + Compliance | Screened customer register with match-handling procedures |
| 31–60 | Implement geo-restriction on AI SaaS/API services | Engineering | Restricted jurisdiction block list active in production |
| 31–60 | Request chip provenance documentation from AI vendors | Procurement | Vendor compliance file with Entity List screening confirmation |
| 61–90 | Draft and publish AI export compliance policy | Legal | Published internal policy approved by General Counsel |
| 61–90 | Train procurement, sales, and engineering teams | HR + Legal | Training completion records by role and function |
| 61–90 | Set quarterly Entity List screening schedule | Compliance | Governance calendar entry with assigned owner and escalation path |
11. 🏁 Conclusion: Geopolitical Risk as Baseline, Not Tail Risk
The most important shift in organizational mindset that AI geopolitics demands is moving from treating geopolitical risk as a tail risk — an unlikely scenario that warrants acknowledgment but not systematic preparation — to treating it as baseline operational context that every AI architecture decision must account for. The organizations that made AI infrastructure decisions in 2021 and 2022 under the assumption that the global AI technology ecosystem would remain largely open and commercially accessible made decisions that are now proving more complicated and more costly to revisit than they would have been if geopolitical resilience had been a design criterion from the start.
The practical implications of this mindset shift are not about becoming paralyzed by geopolitical uncertainty or abandoning AI investment in favor of operational conservatism. AI capability is too central to organizational performance in 2026 for any serious organization to make that choice. The implications are about making AI infrastructure decisions that are durable across a broader range of geopolitical scenarios — choosing architectures that provide diversification rather than single-vendor concentration, investing in the compliance expertise needed to navigate the regulatory environment rather than hoping it will remain stable, and building the operational flexibility to adapt to new constraints rather than designing systems that would require complete rebuilding if specific components became unavailable.
The organizations that navigate the AI geopolitical landscape most successfully in the years ahead will be those that have internalized a simple but demanding principle: every AI capability decision is simultaneously a technology decision, a compliance decision, and a strategic resilience decision. Making all three dimensions explicit — not defaulting to the cheapest or most capable option without examining its geopolitical risk profile — is the discipline that separates organizations that will maintain AI capability through the disruptions ahead from those that will find their AI investments compromised by political events they should have anticipated. The framework provided in our guide to Buy vs. Build for AI provides additional decision structure for making these multi-dimensional AI architecture choices systematically — with geopolitical risk as an explicit evaluation criterion alongside capability, cost, and operational fit.
📌 Key Takeaways
| Takeaway | |
|---|---|
| ✅ | The January 15, 2026 BIS final rule replaced the “presumption of denial” regime for advanced AI chip exports to China with a case-by-case review system — but with strict conditions: a 25% tariff, a 50% volume cap, mandatory US-based third-party testing, and full KYC compliance. Re-exports remain under a presumption of denial. |
| ✅ | Congress approved a 23% increase in BIS’s FY2026 enforcement budget with specific funding for semiconductor enforcement — signaling that enforcement intensity is rising regardless of whether specific export control rules are eased or tightened. Organizations that assume reduced enforcement activity from policy changes are misreading the direction. |
| ✅ | AI geopolitical risk has six distinct vectors — semiconductor export controls, AI software restrictions, cloud service blocking, data localization requirements, rare earth supply controls, and AI standards fragmentation — each affecting different organizations differently based on their technology stack and geographic footprint. |
| ✅ | The BIS Affiliates Rule — extending export controls to foreign entities at least 50% owned by Entity List companies — is suspended until November 10, 2026. Organizations with complex ownership structures in AI supply chains must complete their beneficial ownership analysis before this deadline to avoid automatic non-compliance when the rule resumes. |
| ✅ | Downstream AI consumers — organizations that purchase cloud AI services, deploy AI SaaS internationally, or hire AI researchers from restricted countries — face compliance obligations under EAR, OFAC, and deemed export rules that most have not yet assessed. Being a consumer rather than a manufacturer of AI technology does not eliminate export control exposure. |
| ✅ | The EU is developing AI-specific export controls targeting accelerators above roughly 300 TFLOPS, building on the September 2025 update to Regulation (EU) 2021/821. EU-based organizations face a converging compliance obligation from the AI Act, GDPR, and dual-use export regulations that apply simultaneously to the same AI systems. |
| ✅ | A 90-day structured compliance program — covering AI asset inventory, jurisdiction risk mapping, customer and vendor screening, geo-restriction implementation, and governance documentation — converts reactive compliance exposure into a defensible, audit-ready posture. The cost of this program is a fraction of a single BIS enforcement action, which can reach $1 million per violation or twice the transaction value. |
| ✅ | Every AI infrastructure decision must be evaluated simultaneously as a technology decision, a compliance decision, and a strategic resilience decision — treating geopolitical risk as baseline operational context rather than a tail risk to be acknowledged but not systematically addressed. |
🔗 Related Articles
- 📖 Sovereign AI and Resilience: Protecting Your Workflows from Geopolitical Risk
- 📖 AI Regulation in 2026: 7 New Laws Reshaping How Businesses Use AI
- 📖 AI in Defense and Military: Autonomous Systems and Strategic Intelligence
- 📖 The AI Audit Checklist: How to Prove Your Company is Compliant in 2026
- 📖 EU AI Act Explained: A Beginner-Friendly Compliance Guide and Practical Checklist
❓ Frequently Asked Questions: AI Export Controls and Sanctions Compliance 2026
1. What did the January 2026 BIS rule change about AI chip exports to China?
The January 15, 2026 BIS final rule replaced the previous “presumption of denial” policy for advanced AI chip exports to China with a case-by-case review system. Chips with TPP below 21,000 (including NVIDIA H200 and AMD MI325X) are now eligible for review — but only with a 25% tariff, a 50% volume cap, mandatory US third-party testing, and full KYC documentation. Re-exports remain denied. See our AI Regulation in 2026 guide for the full regulatory context.
2. Does providing AI SaaS or API services internationally create export control exposure?
Yes — software-as-a-service is explicitly covered under US export control regulations. Providing AI-powered services to customers in sanctioned jurisdictions or to SDN-listed entities constitutes an export violation even without any physical product crossing a border. Organizations must implement geo-restriction controls and screen customer lists against OFAC and BIS Entity Lists before onboarding. The AI Vendor Due Diligence Checklist covers the vendor-side of this obligation.
3. What is a “deemed export” and why does it matter for AI companies?
A deemed export is the sharing of controlled AI technology with a foreign national inside the United States — which is legally treated as an export to that person’s country of citizenship. This applies to hiring decisions, research collaborations, and open-source contributions involving nationals of restricted countries working on controlled AI technology. US AI companies with internationally diverse research teams must assess deemed export risk with qualified legal counsel.
4. What is the BIS Affiliates Rule and when does it resume?
The BIS Affiliates Rule extends export control restrictions to foreign entities at least 50% owned (directly or indirectly) by companies on the BIS Entity List, Military End-User List, or OFAC SDN list. It was suspended pending further review and is scheduled to resume November 10, 2026. Organizations with complex ownership structures in their AI supply chains must complete beneficial ownership analysis before this date. Our Sovereign AI and Resilience guide covers the infrastructure resilience strategies that complement compliance programs.
5. What are the penalties for violating AI export control regulations?
Under the Export Administration Regulations, civil penalties for export control violations can reach $1 million per violation or twice the transaction value — whichever is greater. Criminal violations can result in substantial fines and imprisonment for responsible individuals. The BIS received a 23% budget increase in FY2026 specifically for enforcement, including dedicated semiconductor enforcement resources. See The AI Audit Checklist for the evidence documentation framework that demonstrates compliance to regulators.
📧 Get the AI Buzz Weekly Digest
Weekly AI insights, tools, and strategies — delivered every Monday. Free.
Leave a Reply