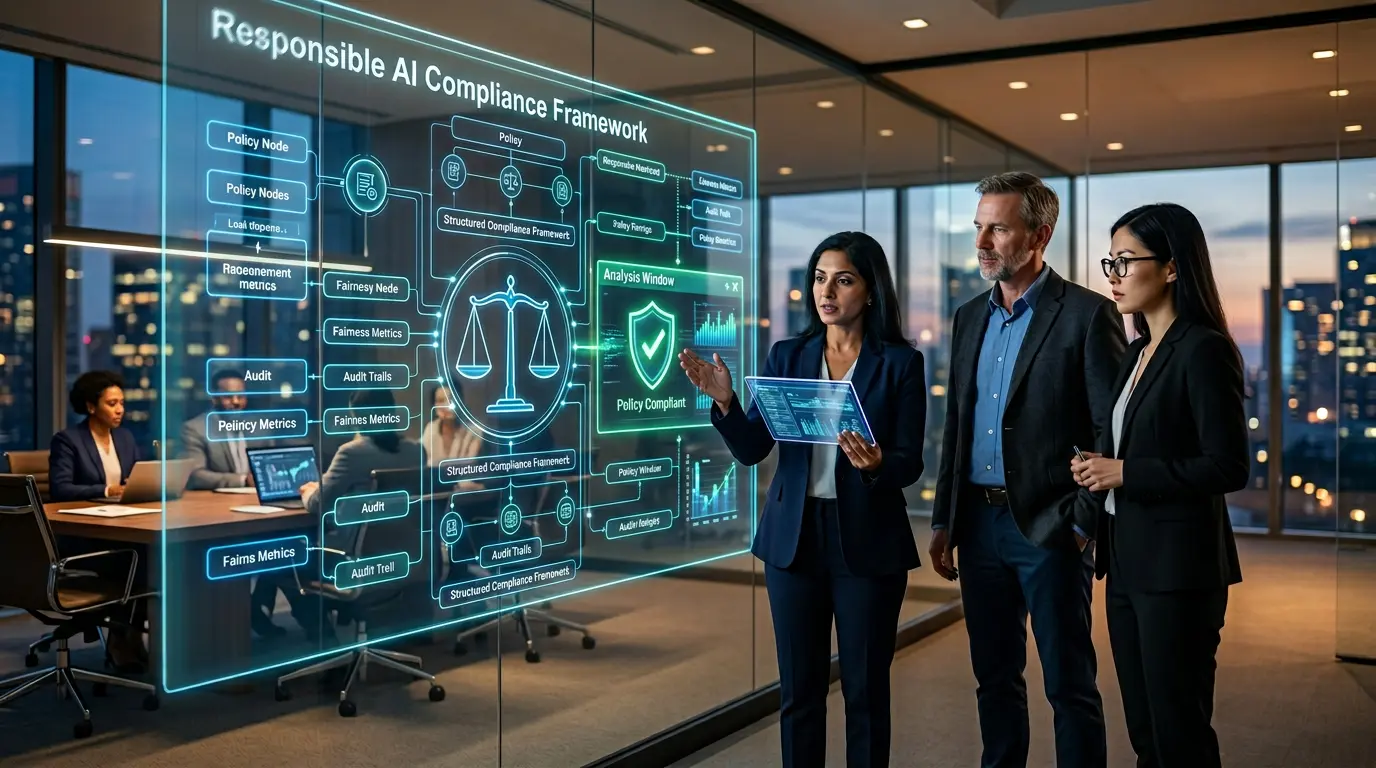
🏛️ 88% of organizations use AI — but only 8% have a comprehensive governance framework to manage it responsibly. This guide explains how to build an AI governance program from scratch: the structure, roles, inventory process, risk tiers, board reporting, regulatory mapping, and a 90-day implementation plan.
Last Updated: October 7, 2026
Most organizations that deploy AI do so without a formal governance structure. Not just without a written policy — without a program, without a named owner, and without a process for making AI decisions accountably. Aon data shows that 88% of organizations used AI in at least one business function in 2025. Economist Impact research finds that only 8% of those organizations maintain a comprehensive AI governance framework. IBM data adds a more uncomfortable finding: 87% of organizations claim they have clear AI governance frameworks — but fewer than 25% have fully implemented the controls needed to manage bias, transparency, and security risks. Claiming governance and running governance are two entirely different things, and the gap between those two numbers is where regulatory exposure, reputational incidents, and board-level accountability failures actually live.
This guide is about building the governance program — not the policy document. An AI Acceptable Use Policy is one document inside a governance program. It defines the rules. Governance is the organizational system that creates those rules, enforces them, updates them when circumstances change, and ensures that someone is accountable when they are violated. BCG’s 2026 research confirms that organizations implementing responsible AI governance are three times more likely to capture the full business benefits of AI than those that treat governance as a compliance checkbox. This guide covers what a governance program is, how to structure it, what roles it requires, how to build and maintain an AI system inventory, how to report AI risk to boards and executives, how to map your program to the major regulatory frameworks, and how to implement the foundations in 90 days regardless of your organization’s size or technical maturity.
The regulatory pressure for formal governance programs has accelerated dramatically in 2026. The EU AI Act’s general provisions became active August 2, 2026, with Annex III high-risk obligations following December 2, 2027 under the Digital Omnibus deferral. The Colorado AI Act took effect February 1, 2026. California’s AI Transparency Act and Texas’s Responsible Artificial Intelligence Governance Act both went live January 1, 2026. The global AI governance platform market — the software organizations use to run these programs — was valued at $308.3 million in 2025 and is projected to reach $3.59 billion by 2033 at a 36% CAGR, according to Grand View Research. That growth rate reflects genuine, urgent demand — organizations are investing in governance infrastructure because regulators, boards, and enterprise buyers are now demanding evidence that it exists.
📖 New to AI terminology? Visit the AI Buzz AI Glossary — 100+ essential AI terms explained in plain English, each linking to a full in-depth guide.
🗓️ 1A. AI Governance Framework Implementation Roadmap: A Practical 90-Day Plan
Most AI governance frameworks fail not at design — but at implementation. Organisations produce comprehensive policy documents, governance charters, and risk classification matrices that are reviewed once at a leadership offsite and never operationalised. The gap between “framework on paper” and “framework in practice” is precisely where regulatory risk lives — and precisely where regulators, auditors, and enterprise procurement teams look first when they need to assess whether governance is genuine. A well-designed framework that has not been operationalised is, from a compliance standpoint, indistinguishable from having no framework at all.
The cause of this implementation failure is almost always the same: the organisation attempts to implement everything simultaneously, becomes overwhelmed by the scope of the programme, and reverts to producing documentation rather than building workflows. A structured 90-day phased approach solves this problem by breaking implementation into achievable milestones — each phase building directly on the last, with a measurable output that serves as both an evidence artifact and a forcing function for the next phase. This roadmap is designed for COOs, CTOs, CISOs, and General Counsel who own governance rollout and need to demonstrate measurable progress at each reporting cycle. It does not require organisational transformation. It requires sequenced, owned action.
The Implementation Principle: An AI governance framework that exists only as a PDF is not a governance framework. Operationalisation — roles, workflows, monitoring cadence, and evidence collection — is where governance actually happens. The 90-day plan below converts policy documents into active governance infrastructure with a measurable output at every stage.
| Phase | Days | Key Actions | Owner | Output | Success Metric |
|---|---|---|---|---|---|
| Foundation | 1–30 | AI tools inventory, risk register creation, stakeholder mapping, draft policy | CTO / CISO | AI tools register + draft policy | Every AI system in use documented |
| Foundation | 1–30 | Define high-risk AI use cases per EU AI Act classifications | Legal / Compliance | Risk classification matrix | All use cases classified by tier |
| Structure | 31–60 | Assign AI governance roles (AI Officer, Risk Owner, DPO liaison) | COO / HR | RACI for AI governance | Roles assigned and documented |
| Structure | 31–60 | Deploy AI acceptable use policy to all staff | HR / Legal | Signed AUP records | 100% staff acknowledgement |
| Structure | 31–60 | Deliver EU AI Act Article 4 AI literacy training | HR / L&D | Training completion records | Documented per Article 4 requirement |
| Operationalisation | 61–90 | Activate monitoring cadence — quarterly reviews, trigger-based escalation | AI Officer | Governance calendar | First quarterly review scheduled |
| Operationalisation | 61–90 | Test AI incident response playbook via tabletop exercise | CISO / IR Team | Tabletop exercise report | Playbook validated and signed off |
| Operationalisation | 61–90 | Activate audit trail and evidence collection system | Legal / IT | Immutable log system live | First audit evidence collected |
Implementation timeline for mid-size organisations with an active AI governance owner. Larger enterprises with complex multi-jurisdiction deployments should allow 6–12 months for full operationalisation of all six governance stack layers.
The single most common implementation failure — and the one that most reliably collapses governance programmes before they reach the Operationalisation phase — is attempting to run Steps 2 and 3 simultaneously. The AI tools inventory must be complete before risk classification begins, because classification requires knowing what you are classifying. Attempting both in parallel produces an incomplete register and an inaccurate risk matrix. For the audit evidence framework that feeds into the Operationalisation phase, our AI Audit Checklist covers all eight compliance domains that a functioning governance programme must be able to evidence. For the incident response playbook that must be tested by Day 90, our AI Agent Incident Response Playbook includes a tabletop exercise template and escalation path documentation.
🏛️ 1. What Is AI Governance? (And Why It Is More Than a Policy)
AI governance is the organizational structure, processes, and accountability mechanisms that ensure AI systems are developed, deployed, and operated responsibly — in alignment with the organization’s values, risk appetite, and applicable legal obligations. It is not a document. It is not a set of rules written in a PDF and shared at an all-hands meeting. It is the live organizational system that creates those rules, enforces them, updates them when AI technology or regulatory requirements change, monitors whether they are working, and ensures that named individuals are accountable when they are not.
The governance vs. policy distinction: Think of an AI governance program like a sports league. The Acceptable Use Policy is the rulebook — the written document that defines what is and is not permitted. The governance program is the league itself: the committee that wrote the rules, the referees enforcing them, the appeals process for disputed calls, the system for updating rules when new situations arise, and the accountability structure for what happens when a team violates them. A rulebook without a league is a document. A league without a rulebook has nothing to enforce. Both are necessary — but they are different things.
The 3-layer model clarifies how governance, process, and policy relate to each other. Layer 1 — Policy is the written rules: what AI systems employees may use, what data they may process, what decisions require human review, and what constitutes a prohibited use. This layer is covered in the AI Acceptable Use Policy guide. Layer 2 — Process is how decisions get made in practice: the pre-deployment review workflow, the risk assessment procedure, the incident escalation path, the documentation requirements, and the change management process when new AI tools are onboarded. Layer 3 — Structure is who is accountable: the governance committee, the named roles, the escalation chain, the board reporting mechanism, and the external engagement model with regulators and auditors. Most organizations that claim to have AI governance have Layer 1 but not Layers 2 or 3. That is precisely why fewer than 25% have implemented the controls needed to manage actual AI risk.
AI governance also differs from data governance and information security management in ways that compliance teams frequently miss. IBM’s 2026 AI governance research confirms that AI governance extends beyond data governance by addressing model risk, algorithmic bias, explainability requirements, and human oversight mechanisms — dimensions that existing data governance programs were not designed to handle. Treating AI governance as a subset of your existing data program is a structural error. It requires its own ownership, its own committee, and its own accountability chain — even when it sits alongside and connects to existing data and security governance programs.
🗂️ 2. The AI Governance Stack — 6 Layers Every Organization Needs
A complete AI governance program operates across six interconnected layers, each addressing a distinct dimension of AI risk. Missing any one layer creates an exposure that the others cannot compensate for. Organizations that have Layer 1 (policy) but not Layer 5 (monitoring) are operating AI systems they cannot observe. Organizations that have Layer 3 (documentation) but not Layer 2 (inventory) are documenting systems they have not catalogued. The stack is sequential — each layer builds on the one below it — but all six must eventually be active for governance to function as a protective program rather than a compliance gesture.
| Layer | Name | What It Is | Example Output | Dedicated Guide |
|---|---|---|---|---|
| 1 | Policy | Written rules for how AI may be used, by whom, for what purposes, with what restrictions | AI Acceptable Use Policy | Corporate AI Policy Guide |
| 2 | Inventory | Complete register of every AI system in use — enterprise, departmental, and embedded AI features — with risk tier classification | AI system register with risk tiers, vendor details, data access scope | H2 4 (this article) |
| 3 | Risk Assessment | Formal process for evaluating each AI use case before deployment — impact, probability, mitigation | Pre-deployment risk review + AI risk register | AI Risk Assessment Guide |
| 4 | Documentation | Transparency artifacts for each deployed AI system — who is responsible, what it does, what it cannot do, how it is overseen | AI system cards, model cards, dataset datasheets | AI System Card Template |
| 5 | Monitoring | Post-deployment tracking of AI system performance, safety, quality, and drift — ongoing and systematic | Drift detection alerts, monthly performance dashboard | AI Monitoring Guide |
| 6 | Incident Response | Documented process for what happens when an AI system produces harmful, incorrect, or non-compliant outputs | AI incident playbook with escalation paths and regulatory notification timeline | AI Incident Response Playbook |
The average enterprise now operates 139+ AI-enabled SaaS applications, according to Security Boulevard’s 2026 enterprise AI analysis — and 23,021 SaaS applications were operating outside centralized IT visibility in the same survey. This is the scale of the inventory and monitoring challenge. A governance program that covers the 10 enterprise-approved AI tools but ignores the 130+ that have embedded AI features — Salesforce Einstein, Microsoft 365 Copilot, HubSpot AI, Slack AI — is not a governance program. It is a compliance artifact that covers a fraction of the organization’s actual AI footprint.
The foundation of the policy layer in any governance program is a written AI Acceptable Use Policy — the document that defines rules, boundaries, and expectations for how AI tools may be used across the organization. That guide provides the full 7-section template and implementation checklist. This article covers the program that runs above, behind, and around that document.
👥 3. AI Governance Structure — Who Owns What
The single most common governance failure is not a missing policy — it is a missing owner. Organizations that produce AI governance documents without assigning a named individual to maintain them, enforce them, and report on them have created documentation, not governance. The ISACA 2026 AI Pulse Poll found that effective AI governance starts with clear ownership and accountability — organizations without a defined governance structure cannot manage AI risk consistently because there is no one responsible for doing so when attention moves elsewhere.
Three governance models describe how organizations structure AI accountability. The Centralized model places all AI governance decisions in a central AI Center of Excellence (CoE) or AI Governance function. Business units request approval from the center before deploying any AI system. This model produces the most consistent governance and the lowest risk of ungoverned deployments — but it slows adoption and creates bottlenecks in large organizations. The Federated model gives business units ownership of AI decisions within central standards. Each unit has its own AI lead who enforces group-wide policy locally. This model scales better but creates inconsistency if central standards are not specific enough. The Hybrid model — the most common in 2026 — centrally owns Tier 1 and Tier 2 (high-risk) AI decisions while federating Tier 3 and Tier 4 (standard and minimal risk) decisions to business units with lighter-touch oversight requirements.
Key Roles Every AI Governance Program Needs
Every AI system in production should have an identifiable owner. Beyond system-level ownership, the governance committee requires defined functional roles. The committee should be chaired by a senior risk, compliance, or legal leader, with an executive sponsor — typically the CTO, CRO, or Chief AI Officer — providing strategic authority and board-level connection. Gartner’s AI governance platform research confirms that the CAIO role has become the fastest-growing C-suite title in 2026, with the US federal government’s mandate that all federal agencies designate a Chief AI Officer further legitimizing the role in the private sector.
| Role | Core Responsibilities | Typical Title | Required? |
|---|---|---|---|
| Executive Sponsor | Owns the governance mandate and budget. Final escalation point for high-risk AI approvals. Board-level accountability for AI risk posture. | CTO, CRO, COO, or Chief AI Officer | ✅ Mandatory |
| AI Governance Lead | Day-to-day governance operations. Maintains AI inventory. Coordinates risk reviews. Produces board reports. Runs governance committee meetings. | Director of AI Governance, Responsible AI Lead, or AI Risk Manager | ✅ Mandatory |
| AI Risk Officer | Owns the risk assessment process. Manages the AI risk register. Ensures governance aligns with the organization’s risk appetite. Chairs or co-chairs the committee in many models. | CISO, Chief Risk Officer, or Senior Compliance Director | ✅ Mandatory |
| Legal and Privacy Counsel | Manages regulatory mapping. Reviews vendor contracts for AI provisions. Advises on GDPR, EU AI Act, and state law applicability to specific deployments. | General Counsel, Chief Privacy Officer, or external legal counsel | ✅ Mandatory |
| AI Ethics Reviewer | Reviews AI use cases for bias, fairness, and ethical alignment. Escalates use cases that may cause disproportionate harm to specific populations. | Can be held by Legal, Compliance, or external Ethics advisory panel | ⚠️ Required for high-risk AI |
| Business AI Champions | Department-level AI points of contact. Bring operational context to risk reviews. Ensure governance decisions account for how AI systems are actually used on the ground. | Department heads or nominated senior staff per business unit | ✅ Mandatory in federated/hybrid |
| Data Governance Lead | Owns training data quality, provenance documentation, and data access controls for AI systems. Bridges AI governance and existing data governance programs. | Chief Data Officer or Data Engineering Lead | ✅ Required when training custom models |
The governance committee should meet monthly or quarterly depending on the volume of new AI initiatives entering the organization. Higher-volume environments — large enterprises actively deploying AI across multiple business units simultaneously — warrant monthly standing meetings with delegated authority for routine Tier 3 and Tier 4 decisions. The committee’s primary functions are reviewing AI deployment requests, classifying risk, monitoring the AI portfolio, and producing board reports. For small and mid-sized businesses, this does not require a large committee. An AI Governance Lead combined with an AI Risk Owner (often the same person who holds the CISO role), Legal counsel, and two or three business unit champions is a functional governance structure — and it is infinitely better than the alternative, which is no structure at all.
📋 4. The AI System Inventory — Your Governance Foundation
You cannot govern what you have not catalogued. The AI system inventory is the foundational data asset of any governance program — the complete register of every AI system the organization uses, owns, or has approved for use, enriched with enough context to make governance decisions about each one. Without a current, accurate inventory, every other governance function operates blind. Risk assessments cannot prioritize what they cannot see. Monitoring cannot track what it does not know exists. Board reports cannot be accurate about an AI portfolio that has not been mapped.
The inventory challenge in 2026 is larger than most governance teams initially anticipate. The average enterprise runs 139+ AI-enabled SaaS applications. Many of these are not “AI tools” in the traditional sense — they are productivity platforms, CRMs, HRIS systems, and marketing tools that have added AI features in the past 18 months without necessarily triggering a procurement review. Microsoft 365 Copilot, Salesforce Einstein, HubSpot AI, LinkedIn Recruiter AI, and Zoom AI Companion are AI systems for governance purposes — they process organizational data using machine learning models and produce outputs that influence business decisions. They belong in the inventory. A Shadow AI discovery process — typically a combination of SaaS access review, network traffic analysis, and employee survey — is the first step in building a complete inventory for any organization that has not previously catalogued its AI footprint.
AI Risk Tier Classification
Once the inventory is built, every system must be classified by risk tier. The tier determines the governance requirements — what documentation is needed, what monitoring must be in place, what approval process applies to deployment, and what regulatory obligations the organization must fulfill. Use the four-tier model below as your classification framework. It aligns with EU AI Act Annex III categories at Tier 1 and mirrors the NIST AI RMF risk prioritization approach across all tiers.
| Risk Tier | Definition | Examples | Governance Requirements |
|---|---|---|---|
| Tier 1 — Critical | High-risk AI per EU AI Act Annex III — consequential decisions affecting individuals’ rights or safety | HR screening AI, credit scoring, healthcare diagnostic AI, law enforcement AI, education access tools | Full compliance program: FRIA, system card, conformity assessment, adversarial robustness testing, continuous monitoring, incident reporting within 24–72 hours, 10-year record retention |
| Tier 2 — Significant | Consequential decisions or sensitive data — not Annex III but high organizational risk if the system fails | Customer segmentation AI, content moderation systems, fraud detection, AI used in regulated reporting | Enhanced monitoring, AI system card, AI risk assessment, human-in-the-loop requirement for consequential outputs, annual bias audit |
| Tier 3 — Standard | Productivity-enhancing AI with low stakes — output is used as a draft or suggestion, not a decision | Email drafting AI, meeting summarization, internal chatbots, code assistance tools | AUP compliance, mandatory staff training, lightweight system registration, periodic review — no formal system card required |
| Tier 4 — Minimal | Embedded AI with negligible governance risk — AI is incidental to the primary product function | Spell check, autocomplete, search ranking, recommendation features in approved enterprise tools | AUP awareness only — catalog in inventory for completeness but no additional governance action required |
What belongs in each inventory record: the system name and vendor, the version or model underlying it, the contract and renewal status, the data types it accesses (including whether it processes personal data), the risk tier, the current governance status (approved / under review / pending risk assessment), the named system owner, and the date of last governance review. The inventory should be reviewed at minimum quarterly — and any new AI deployment request should trigger an inventory update as the first step in the approval workflow, before any risk assessment or committee review begins. For the AI audit checklist that complements the inventory process when evaluating new AI tools, see the dedicated guide.
📊 5. Board and Executive Reporting on AI Risk
Boards are under growing pressure to oversee AI, with many actively working to identify the right tools, metrics, and expertise to do so effectively. McKinsey and the National Association of Corporate Directors confirmed at their 2026 RSA panel that AI is no longer just a technology topic — it is a core enterprise risk and strategic differentiator that belongs on the board agenda at the same level as cybersecurity and financial risk. What Directors Think 2026 found that 66% of directors already use AI for board work themselves — but only 22% have governance processes in place for their own board’s AI usage, and 28% now name AI expertise as a top board recruitment priority.
What boards need from AI governance reporting: Board members need enough context to ask the right questions — not technical briefings that exceed their expertise. The most effective AI governance reporting translates the governance program’s status into five business-language metrics: what we have, what risk it carries, whether it is compliant, what incidents have occurred, and how mature our program is relative to where it needs to be. A one-page dashboard showing current state, trend, and required action outperforms any detailed technical briefing.
The five metrics every AI governance board report should include, drawn from the Tyson Martin 2026 board governance framework: AI inventory coverage — what percentage of known AI systems have been catalogued and risk-classified; high-risk AI control maturity — the governance and compliance status of all Tier 1 and Tier 2 systems; incident response readiness — whether the organization has a tested AI incident playbook and whether it has been exercised in the past 12 months; regulatory compliance posture — current compliance status against all applicable regulations with upcoming deadlines flagged; and third-party AI risk coverage — what percentage of vendor-provided AI tools have completed the organization’s AI vendor due diligence process. Each metric needs a defined baseline and an escalation threshold — trend comparison across reporting cycles matters more than any single snapshot. For the AI audit checklist that generates the evidence feeding these metrics, see the dedicated guide.
Reporting cadence should match the pace of the organization’s AI deployment. Organizations actively onboarding new AI systems monthly should report to the board quarterly and to the executive risk committee monthly. Organizations with a stable AI portfolio and no active high-risk deployments can report to the board annually with a quarterly executive-level summary. The critical constraint is that board members need enough context to challenge management credibly — and “we left it to IT” is no longer a defensible governance posture in a regulatory inquiry or post-incident review.
🔒 6. Mapping Your Governance Program to Regulatory Frameworks
No single framework covers every enterprise AI governance requirement in 2026. Most global organizations operating across multiple jurisdictions use two or three frameworks simultaneously, layered by geography, industry, and the risk profile of specific systems. The three regulatory anchors for enterprise AI governance in 2026 are the EU AI Act, the NIST AI Risk Management Framework, and ISO 42001. Each approaches governance differently — but they share a common structural logic, and organizations that build their internal program around NIST AI RMF’s four functions (Govern, Map, Measure, Manage) find it significantly easier to map obligations across jurisdictions.
| Framework | What It Requires from Your Governance Program | Your Program Must Produce | Deadline / Status |
|---|---|---|---|
| EU AI Act | Documented risk management system, human oversight mechanisms, technical documentation for high-risk systems, Article 50 AI disclosure for all conversational AI | AI inventory (Tier 1+2) + risk register + system cards + FRIA + incident reporting process | Art. 50: Aug 2, 2026 ✅ ACTIVE. Annex III: Dec 2, 2027 |
| NIST AI RMF | GOVERN function: policies, accountability structures, risk tolerance defined and documented. MAP, MEASURE, MANAGE functions: risk identification, evaluation, and treatment processes | Governance charter + risk assessment process + risk register + monitoring dashboard | Voluntary (US) — but Texas TRAIGA safe harbor requires NIST RMF alignment ✅ Jan 1, 2026 |
| ISO 42001:2023 | Full AI Management System (AIMS) with defined objectives, controls, internal audit process, and management review. Certifiable standard. | Documented AIMS covering all 6 governance stack layers + internal audit program + management review records | Voluntary international standard — growing enterprise procurement requirement |
| Colorado AI Act | Algorithmic impact assessments for high-risk AI in employment, lending, healthcare, education, housing affecting Colorado residents. Consumer disclosures and appeal rights. | Pre-deployment impact assessment process + consumer disclosure mechanism + appeals workflow | ✅ Active Feb 1, 2026 |
| SR 26-2 (Banking) | Model risk management framework for traditional AI in banking (credit, fraud, underwriting). Excludes generative and agentic AI from scope — those require separate governance. | Model inventory + independent validation process + model performance monitoring + governance documentation | ✅ Active April 17, 2026 (banking sector) |
| California AI Transparency Act / Texas TRAIGA | AI-generated content disclosure (California). Risk assessment + NIST RMF alignment for safe harbor (Texas — applies by business activity, not headcount). | Content disclosure mechanism + NIST RMF-aligned governance documentation | ✅ Both active Jan 1, 2026 |
For a full walkthrough of EU AI Act compliance requirements across all risk tiers and conformity assessment obligations, see the dedicated guide. For the ISO 42001 AI Management System certification pathway, see the ISO 42001 guide. The key operational insight from organizations that have mapped their programs across all applicable frameworks is that the governance stack’s six layers are essentially the common implementation layer — build the inventory, risk assessment, documentation, monitoring, and incident response processes once, and then map each to the relevant framework requirements rather than building separate programs for each regulation.
🗺️ 7. The 90-Day AI Governance Build Plan
Building an AI governance program from scratch is achievable in 90 days at the foundation level — not perfect, not comprehensive across all six stack layers, but functional enough to manage immediate risk, demonstrate good faith to regulators and auditors, and provide a stable base for progressive maturity. The 90-day plan focuses on the three outputs that have the highest risk-reduction value per hour of effort: the AI inventory, the governance structure, and the documentation artifacts for the highest-risk systems.
| Phase | Days | Actions | Output (Evidence Artifact) |
|---|---|---|---|
| Phase 1: Foundation | Days 1–30 |
| AI system inventory register + Published AUP + Named governance owner |
| Phase 2: Structure | Days 31–60 |
| Risk-classified inventory + Governance committee charter + Approval workflow + Risk register (Tier 1 and 2) |
| Phase 3: Documentation | Days 61–90 |
| System cards (Tier 1+2) + Incident playbook + Training records + Board AI risk report |
One practical note on sequencing: the single most important action in the entire 90 days is appointing a named Governance Lead in Week 1. Without a named owner, every subsequent action depends on whoever happens to be paying attention that week — and governance programs without owners do not survive the first organizational distraction. Everything else in the 90-day plan can be imperfect and iterative. The ownership structure cannot be. For the AI incident response playbook that should be in place by Day 90, the dedicated guide includes a copy-paste template.
🔒 7A. How to Implement AI Governance: A Step-by-Step Framework
Understanding what AI governance is — and actually implementing it inside a real organization — are two very different challenges. Most organizations stall between awareness and action. The step-by-step framework below is designed to close that gap, moving from a blank slate to a functioning AI governance program in a structured, audit-ready sequence.
“The organizations that successfully implement AI governance in 2026 are not the ones with the most sophisticated frameworks on paper — they are the ones that assigned clear ownership, started with their highest-risk AI use cases, and built documentation habits before they were required to.”
The eight-step implementation sequence below applies regardless of your organization’s size, industry, or current AI maturity level. It is designed to be executed in order — each step builds on the one before it.
| Step | Action | Output / Evidence | Owner | Timeframe |
|---|---|---|---|---|
| 1 | Appoint an AI Governance Owner — designate a named individual (not a committee) accountable for the program | Written appointment. Role description. Reporting line to C-suite | CEO / Board | Week 1 |
| 2 | Inventory all current AI use — document every AI tool, model, and automated decision system in use across the organization | AI use case register. Vendor list. Data flow map | AI Governance Owner + IT | Weeks 1–2 |
| 3 | Classify AI use cases by risk — apply EU AI Act risk tiers (unacceptable, high, limited, minimal) to each use case | Risk-classified AI register. High-risk use cases flagged for priority action | AI Governance Owner + Legal | Weeks 2–3 |
| 4 | Draft your AI Policy — define acceptable use, prohibited use, data handling rules, and human oversight requirements | Published AI Policy document. Employee acknowledgment process | AI Governance Owner + HR + Legal | Weeks 3–4 |
| 5 | Implement risk controls on high-risk AI — human oversight gates, output validation, audit logging, and incident escalation paths | Control implementation log. Test results. Sign-off from system owner | AI Governance Owner + IT + Security | Weeks 4–6 |
| 6 | Train employees on AI literacy and policy — mandatory training covering AI basics, acceptable use, and how to report concerns | Training completion records. EU AI Act Article 4 compliance evidence | HR + AI Governance Owner | Weeks 5–7 |
| 7 | Establish ongoing monitoring — schedule quarterly AI audits, model performance reviews, and incident log reviews | Audit schedule. Monitoring dashboard. Incident register | AI Governance Owner | Month 2 onward |
| 8 | Align to ISO/IEC 42001 or equivalent standard — map your governance program to the international AI management system standard for audit readiness | Gap analysis. AIMS documentation. Certification roadmap if required | AI Governance Owner + Compliance | Month 3 onward |
Step 1 is the most commonly skipped — and the most damaging to skip. AI governance programs run by committees without a named owner consistently stall at Step 3 or 4. A single accountable person with C-suite access and cross-functional authority is the prerequisite for every other step working. For the full corporate AI policy template that supports Step 4, see How to Write a Safe Corporate AI Policy. For the audit evidence requirements that support Steps 5–8, see the AI Audit Checklist.
🔒 7B. 2026 Regulatory Drivers Every AI Governance Program Must Address
AI governance is no longer a voluntary best practice. In 2026, multiple binding regulatory frameworks are simultaneously active — and most organizations operating across borders are subject to more than one. An AI governance framework that does not map to these specific regulations is not audit-ready, regardless of how well-designed it is internally.
“In 2026, the question is no longer whether your organization needs an AI governance framework — it is whether your framework is specific enough to satisfy regulators, auditors, and enterprise procurement teams simultaneously.”
The table below maps the most critical 2026 regulatory requirements to their AI governance implications — and what your program must document to demonstrate compliance. For organizations subject to GDPR specifically, the AI and Data Privacy guide covers the full data protection obligations that sit alongside these broader governance requirements.
| Regulation | Who It Affects | Key AI Governance Requirement | What to Document | In Force |
|---|---|---|---|---|
| EU AI Act — High-Risk Provisions | Any organization deploying high-risk AI touching EU residents — healthcare, hiring, credit, law enforcement, critical infrastructure | Risk assessment, human oversight, transparency, data governance (Articles 10, 25, 50) | Technical documentation, conformity assessment, EU Declaration of Conformity, post-market monitoring logs | ✅ August 2026 |
| ISO/IEC 42001:2023 | Any organization seeking certified AI management system (AIMS) — increasingly required in enterprise procurement | Full AI management system — policies, risk controls, objectives, monitoring, continual improvement | AIMS policy, risk register, control evidence, internal audit records, management review minutes | ✅ Current |
| Colorado AI Act (Feb 2026) | Organizations using high-risk AI affecting Colorado residents — employment, credit, education, healthcare, housing | Impact assessments, bias controls, consumer disclosure, human oversight mechanisms | AI impact assessment reports, bias testing logs, consumer notice templates, oversight process documentation | ✅ February 2026 |
| U.S. Federal SR 26-2 | US banking and financial institutions using AI in credit, trading, customer-facing, or risk systems | Model governance documentation, validation, ongoing monitoring, collaborative AI training controls | Model inventory, validation reports, monitoring logs, data governance documentation | ✅ April 2026 |
| Maine AI Act (July 2026) | Organizations using AI in employment decisions affecting residents of Maine | Employee notification, human review rights, AI decision audit trails | Notification templates, human review process documentation, decision audit logs | ✅ July 2026 |
| GDPR — Articles 5 and 25 | Any organization processing personal data of EU residents using AI | Data minimization, Privacy by Design, lawful basis for AI processing | DPIA records, data flow maps, lawful basis documentation, DPA agreements with AI vendors | ✅ Current |
For organizations subject to multiple frameworks simultaneously — which includes most multinationals in 2026 — the most efficient approach is to build your governance program around ISO/IEC 42001 first, then layer regulation-specific requirements on top. ISO/IEC 42001 provides the structural foundation that satisfies the documentation and process requirements of most other frameworks. For a deep dive into ISO/IEC 42001 implementation, see ISO/IEC 42001 Explained. For the EU AI Act’s specific documentation requirements, see the EU AI Act Compliance Guide.
📈 8. AI Governance Maturity Model
AI governance is not a binary state — compliant or non-compliant. It is a maturity continuum, and understanding where your organization sits on that continuum is essential for prioritizing improvement efforts, reporting accurately to boards, and making informed decisions about where to invest governance resources. The four-stage maturity model below reflects the 2026 enterprise landscape and maps to the NIST AI RMF GOVERN function progression.
Stage 1 — Reactive: No formal governance program. AI tools adopted organically by departments without approval processes. No inventory. No named owner. Incidents handled case-by-case without a documented process. The majority of organizations are at Stage 1 — the gap between 88% AI adoption and 8% comprehensive governance defines this population. The risk at Stage 1 is not theoretical: 63% of organizations that experienced AI-related breaches lacked a governance policy, and 97% lacked proper AI access controls.
Stage 2 — Foundational: A written AUP exists. A named governance owner has been appointed. An AI system inventory is in progress or partially complete. Pre-deployment approval is required but informally applied. No systematic monitoring. Risk classification is incomplete. This stage corresponds to the end of Phase 1 in the 90-day build plan. Organizations at Stage 2 can demonstrate good faith to regulators — but they cannot yet produce the audit evidence that confirms their governance program is operating as documented.
Stage 3 — Structured: Full AI system inventory with risk tier classification. Formal governance committee meeting regularly. Pre-deployment approval workflow documented and enforced. System cards exist for Tier 1 and Tier 2 systems. Basic monitoring in place. Incident response playbook tested. Board receives quarterly AI risk reports using the 5-metric dashboard. This stage corresponds to the end of the 90-day build plan and represents substantial compliance with NIST AI RMF — satisfying the Texas TRAIGA safe harbor requirement. The AI audit checklist provides the evidence framework for demonstrating Stage 3 compliance to external auditors.
Stage 4 — Optimized: Governance integrated into product development lifecycle from ideation, not applied retrospectively at deployment. AI risk appetite formally defined and board-approved. Continuous monitoring across all Tier 1 and Tier 2 systems with automated alerting. Regular bias audits with results reported to the governance committee. External audit of governance controls completed annually. ISO 42001 certification in progress or achieved. Governance program actively updated as new regulatory requirements emerge — without waiting for enforcement action to trigger action. BCG’s 2026 research confirms that organizations operating at Stage 3 and above are three times more likely to capture the full business benefits of AI than those at Stage 1 or 2 — because their governance program enables faster, more confident AI deployment rather than slowing it down.
⚖️ 2A. 2026 Regulatory Mapping: How EU AI Act, Colorado AI Act, and SR 26-2 Shape Your AI Governance Framework
2026 is a watershed year for AI governance regulation — not because a single landmark law came into force, but because multiple binding frameworks became simultaneously enforceable across different jurisdictions for the first time. The EU AI Act’s high-risk provisions became enforceable in August 2026. The Colorado AI Act has been active since February 2026. SR 26-2 — the Federal Reserve’s replacement for the SR 11-7 model risk management guidance — took effect in April 2026, fundamentally updating how US banking institutions govern AI models. Maine AI Act covering employment decisions activated in July 2026. For any organisation operating across US states or serving EU residents, a governance framework that addresses only one of these obligations is not a governance framework — it is a compliance gap with documentation attached.
The challenge for organisations scaling AI adoption is that these frameworks do not share the same structure, scope, or evidence requirements. The EU AI Act is a product safety regulation — it classifies AI systems by risk and imposes obligations on developers and deployers. The Colorado AI Act is a consumer protection law — it focuses on algorithmic impact assessments and individual rights. SR 26-2 is a prudential banking supervisor — it focuses on model risk management, independent validation, and governance documentation. GDPR operates as a data processing regulation that intersects with AI at every point where personal data is involved. A SaaS company scaling AI across enterprise clients may be simultaneously subject to all four, and a governance framework that maps to only the EU AI Act — the most commonly referenced — is incomplete from a compliance standpoint from Day 1.
The 2026 Regulatory Reality: AI governance is no longer optional. EU AI Act high-risk provisions are enforceable now. The question is not whether to build a governance framework — it is whether yours maps to the specific obligations your jurisdiction imposes, with evidence that satisfies auditors, regulators, and enterprise procurement teams simultaneously.
| Regulation | Jurisdiction | Key Governance Obligation | Framework Component Required | Enforcement Date |
|---|---|---|---|---|
| EU AI Act Art. 4 | EU | AI literacy training for all staff using AI systems — proportionate to context and risk | Staff training programme + dated completion records per employee | ✅ Aug 2026 |
| EU AI Act Art. 9 | EU | Documented risk management system for all high-risk AI systems throughout lifecycle | AI risk register + documented review cadence + residual risk sign-off | ✅ Aug 2026 |
| EU AI Act Art. 10 | EU | Data governance for training, validation, and testing data used in high-risk AI | Data lineage documentation + dataset provenance records + bias examination evidence | ✅ Aug 2026 |
| EU AI Act Art. 14 | EU | Human oversight for high-risk AI decisions — natural persons able to understand, monitor, and intervene | HITL approval gates + escalation workflow + override capability documentation | ✅ Aug 2026 |
| Colorado AI Act | Colorado, US | Impact assessment for high-risk AI in employment, credit, education, healthcare, housing affecting Colorado residents | FRIA / algorithmic impact assessment process + consumer notice mechanism + appeal workflow | ✅ Feb 2026 |
| SR 26-2 | US Banking | Model risk governance for AI systems — replaces SR 11-7. Covers traditional AI; generative and agentic AI require supplementary governance. | Model risk management framework + independent validation process + performance monitoring logs | ✅ Apr 2026 |
| GDPR Art. 5 + 25 | EU | Data minimisation, purpose limitation, and Privacy by Design for all AI systems processing personal data | DPIA records + data flow maps + lawful basis documentation + DPA agreements with AI vendors | ✅ Active |
Regulatory mapping current as of October 2026. EU AI Act Annex III high-risk obligations delayed to December 2, 2027 under Regulation 2026/1744 (Digital Omnibus). Article 4 (AI literacy) and Article 50 (transparency) are in force now. Always verify current enforcement status with qualified legal counsel.
For SaaS companies and scaling organisations specifically: the scope question is the most commonly misunderstood element of this regulatory stack. Texas TRAIGA (active January 1, 2026) applies by business activity conducted in Texas — not by company headcount or physical presence. A 30-person SaaS company with enterprise clients in Texas is inside TRAIGA’s scope if its AI systems influence consequential decisions for Texas residents. SR 26-2 applies to any financial institution supervised by the Federal Reserve, OCC, or FDIC — regardless of size. Colorado’s AI Act applies to any developer or deployer of high-risk AI that affects Colorado residents in covered domains. Scoping errors — assuming a regulation does not apply without verifying the actual jurisdictional trigger — are the most common source of unintentional non-compliance in 2026. For the full EU AI Act compliance walkthrough, see our EU AI Act guide. For the risk assessment process that generates the impact assessments required under Colorado’s Act and the risk management documentation required under SR 26-2, see our AI Risk Assessment guide. For vendor-side obligations — including what to require from third-party AI providers in your supply chain — see our Third-Party AI Vendor Risk guide.
🏁 9. Conclusion: Governance Is What Makes AI Scale Safely
The 2026 consensus on AI governance is clear: organizations that treat it as a compliance burden will build programs that satisfy auditors on paper and fail in practice. Organizations that treat it as operational infrastructure — the program that makes it safe to say yes to AI at scale — build programs that compound value over time. BCG’s research confirms the counterintuitive business case: governance accelerates AI adoption rather than limiting it, because it creates the organizational confidence to deploy AI in higher-value, higher-stakes contexts than a governance-free environment would ever permit. The 90-day build plan in this guide is not a compliance project. It is the foundation for an AI-enabled organization that can demonstrate accountability to any audience — regulators, boards, enterprise buyers, or the individuals whose lives its AI systems affect.
Start with the two actions that matter most: appoint a named Governance Lead today, and run a Shadow AI discovery audit this week. Everything else in this guide builds on those two foundations. For the specific document that anchors Layer 1 of the governance stack, the AI Acceptable Use Policy guide provides the complete 7-section template. For the audit evidence that demonstrates your governance program is operating as documented, the AI audit checklist covers all eight compliance domains. The governance program you build in the next 90 days is the organizational foundation that every future AI deployment will depend on — build it deliberately, own it explicitly, and update it continuously.
As your governance program matures beyond the foundational 90-day build, agentic AI introduces a specialized governance challenge that requires dedicated attention. Autonomous agents can take actions, spawn sub-agents, and operate across systems without human approval at each step — creating identity, observability, and accountability gaps that general AI governance frameworks were not designed to address. For the specific security risks agentic deployments introduce, the OWASP Top 10 for Agentic Applications maps the 10 critical vulnerabilities every agentic AI deployment must address. Our Agentic AI Governance guide covers the complete organizational framework for governing autonomous agents — including autonomy classification, agent inventory, least-privilege controls, human oversight design, and a 2026 regulatory mapping for EU AI Act, SR 26-2, and NIST AI RMF.
📌 10. Key Takeaways
| Component | Action Item | Primary Goal |
|---|---|---|
| Policy | Draft AUP and vendor guidelines. | Set the rules of engagement. |
| Inventory | Catalog every AI tool and use case. | Eliminate Shadow AI. |
| Controls | Implement ZTNA and data tagging. | Prevent data leakage. |
| Culture | Mandate training and ethics reviews. | Ensure human accountability. |
| Compliance | Map to NIST and EU AI Act. | Future-proof against regulation. |
❓ AI Governance FAQ
Flag to Editor: The following FAQ section is currently embedded in the article body. Per AI Buzz Rule 12, this content must be moved to the RankMath FAQ Block at the bottom of the post in the WordPress editor to ensure correct Schema markup.
What is the difference between AI Governance and AI Ethics?
AI Ethics provides the moral principles (e.g., “AI should be fair”), while AI Governance provides the operational framework to enforce those principles (e.g., “Bias testing is required before deployment”).
Do small businesses need AI governance?
Yes. Even if using third-party tools like ChatGPT, small businesses are liable for data breaches and regulatory violations. A “lite” version of governance (AUP + Vendor Review) is essential.
Who should lead the AI Governance committee?
A cross-functional trio is ideal: the CTO/CISO for technical oversight, the CLO (Legal) for compliance, and a business lead (COO or CMO) to ensure the AI creates value.
Is the EU AI Act relevant to US companies?
Yes. Any US company offering AI systems in the EU market or using AI that affects individuals in the EU must comply with the Act.
📚 Related Articles
- AI Model Risk Management: A 2026 Enterprise Framework
- Third-Party AI Vendor Risk: 10 Questions to Ask Every Provider
- Zero Trust for AI: Securing the Future of Autonomous Systems
- How to Write a Safe Corporate AI Policy (Free Template)
- Shadow AI: How to Find and Secure Unmanaged AI Tools
Check out our Glossary of 100+ Essential AI Terms for more insights into the world of artificial intelligence.
📧 Get the AI Buzz Weekly Digest
Weekly AI insights, tools, and strategies — delivered every Monday. Free.
Leave a Reply