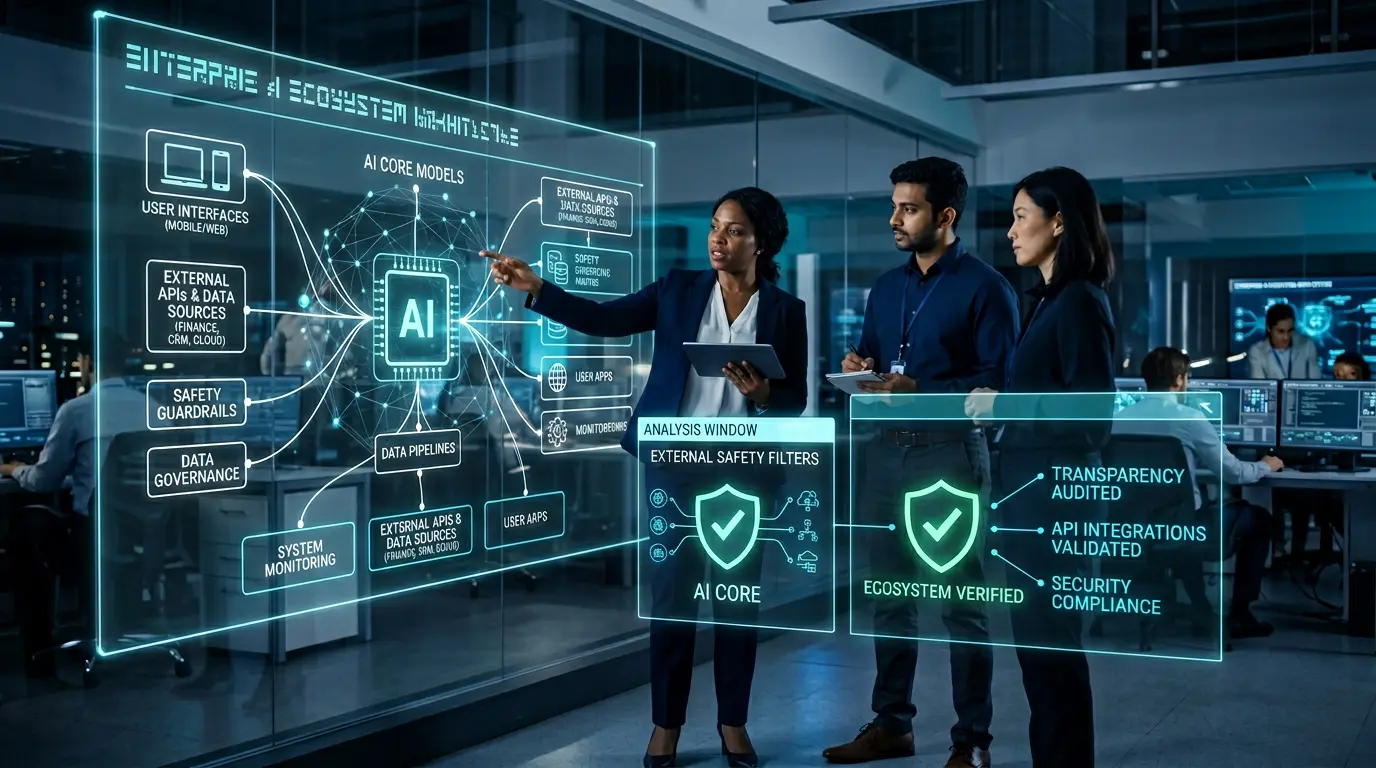
📋 An AI system card is the compliance document that describes your deployed AI application — not the model, not the data, but the live system users interact with. This guide explains what it is, how it differs from a model card, and includes a complete copy-paste template updated for EU AI Act Article 13 and 2026 regulatory requirements.
Last Updated: October 11, 2026
If your organization deploys an AI system — a customer-facing chatbot, an internal document review assistant, a hiring screening tool, or any other AI-powered application — you need a document that describes what it does, how it works, what it cannot do, who is responsible for it, and how users can seek redress if it fails them. That document is an AI system card. It is not a model card. It is not a dataset datasheet. It is the application-level documentation artifact that describes the deployed system your users actually interact with — and in 2026, it has become the primary documentation artifact that EU AI Act Article 13 compliance, enterprise procurement questionnaires, and AI governance frameworks demand as evidence that you are managing your AI responsibly.
This guide is the complete resource for AI system card documentation in 2026. You will find a plain-English explanation of what system cards are and how they differ from AI model cards and Datasheets for Datasets, a side-by-side comparison of all three documentation artifacts with a practical guide on when you need each one, a complete copy-paste 10-section template updated for current regulatory requirements, real examples from OpenAI, Anthropic, and Meta, a dedicated EU AI Act Article 13 and Article 50 compliance mapping table, a new section on who needs a system card in 2026, and a maintenance trigger checklist that addresses the most common audit failure — documentation that was never updated after initial deployment.
The 2026 regulatory reality has fundamentally changed the audience for this document. System cards were once published voluntarily by frontier AI labs as transparency gestures. Today, they are expected evidence in enterprise vendor due diligence processes, required documentation under EU AI Act Article 13 for high-risk system deployers, and demanded by procurement teams at large organizations before any AI tool is approved for use with sensitive data. Whether you are a vendor selling to enterprise clients or an organization deploying a third-party AI tool that affects consequential decisions, this guide gives you the structure and the content to produce a system card that satisfies both internal governance and external regulatory scrutiny. As part of any AI audit and due diligence process, requesting a system card from your AI provider is now standard practice.
📖 New to AI terminology? Visit the AI Buzz AI Glossary — 100+ essential AI terms explained in plain English, each linking to a full in-depth guide.
📋 AI System Card vs Model Card: What’s the Difference and When Do You Need Each?
The two most commonly confused AI documentation artifacts are the model card and the system card. They sound similar, they reference each other, and both are required under EU AI Act transparency obligations — but they answer fundamentally different questions, are written by different organizations, and satisfy different regulatory requirements. Confusing them is one of the most common documentation errors AI governance teams make when building their compliance programs from scratch.
A model card documents the AI model itself — its architecture, training methodology, benchmark performance, and known failure modes at the model level. It is written by the team that trained the model. A system card documents the AI application built on top of that model — the specific deployment context, the use case, the safety guardrails the operator has implemented, the human oversight mechanisms in place, and who is accountable when something goes wrong. It is written by the organization deploying the application. The critical practical consequence of this distinction: the same underlying model can power dozens of completely different system cards. OpenAI’s GPT-4o model card describes the model. Every organization that builds a customer-facing chatbot, a hiring screening tool, or an internal knowledge assistant on top of GPT-4o must write their own system card — because each deployment has different users, different risks, different safeguards, and a different accountability structure.
| Dimension | Model Card | System Card |
|---|---|---|
| What it documents | The AI model — architecture, training, benchmarks | The AI application — deployment, use case, safeguards |
| Who writes it | Model developer | Application deployer / operator |
| EU AI Act obligation | Article 10 — training data documentation | Article 13 — transparency to deployers and users |
| Scope | One model → one card | One model → many system cards |
| Primary audience | Researchers, developers, downstream operators | End users, regulators, auditors |
| Required for | Any model subject to EU AI Act | High-risk AI system deployments |
| Real example | GPT-4 model card (OpenAI) | ChatGPT system card (OpenAI) |
Key distinction: A model card answers: “What is this AI model?” A system card answers: “What does this AI application do, who is it for, and what guardrails are in place?” Both are now EU AI Act obligations — and they are not interchangeable. Submitting a model card in response to an Article 13 audit request does not satisfy the requirement.
For AI governance teams building their documentation stack, the practical sequencing is: request the model card from your AI vendor before deployment, then write your own system card that references the model card while adding the deployment-specific information only your organization can provide. The AI model cards guide covers what to request from your vendor and what the model card should contain. This guide covers what you add on top of it. For EU AI Act compliance, both are required — and it is the system card that your organization is directly accountable for producing. The full Article 13 compliance framework is covered in the EU AI Act compliance guide.
🏢 Who Must Produce AI System Cards in 2026 — and What Regulators Expect to See
Before August 2026, system cards were a best practice promoted by AI labs as a voluntary transparency measure. After August 2, 2026 — when EU AI Act Article 50 transparency obligations became active and the broader high-risk AI compliance framework entered force — system cards became a legal documentation requirement for organizations deploying AI in the EU market. The shift is significant and the audience has expanded dramatically. System cards are no longer something only frontier labs produce voluntarily. They are now something every organization deploying high-risk AI must maintain, and something every enterprise procurement team now requests before approving an AI vendor.
What regulators and auditors expect to see when reviewing a system card in 2026 has also evolved. A voluntary 2023-era system card was a narrative document describing what the system does. A 2026-compliant system card is a structured evidence artifact that maps directly to regulatory requirements, names specific accountability owners, documents performance metrics disaggregated by relevant subgroups, and carries a version history that proves it has been actively maintained since deployment. Auditors checking Article 13 compliance are not reading system cards for general understanding — they are checking whether specific required fields are present, whether performance data is disaggregated, and whether the document reflects the current state of the system rather than its state at the time of initial deployment. An undated or unmaintained system card is treated as evidence of governance failure, not documentation.
| Organization Type | Obligation | Regulation | Deadline / Status |
|---|---|---|---|
| EU high-risk AI deployer | System card equivalent documentation mandatory | EU AI Act Article 13 | Dec 2, 2027 ✅ Prepare now |
| Any EU AI system (user-facing) | AI disclosure to users — Article 50 transparency obligations | EU AI Act Article 50 | Aug 2, 2026 ✅ Active now |
| US federal AI deployer | AI use case inventory and transparency documentation | OMB AI memoranda | Current |
| Financial services (US) | Model documentation including system context (traditional AI only — GenAI/agentic excluded) | SR 26-2 (Fed/OCC/FDIC) | Apr 17, 2026 ✅ Active now |
| Healthcare AI deployer (US) | Intended use documentation and limitation disclosure | FDA AI/ML guidance | Current |
| All organizations deploying AI | System card as governance best practice | NIST AI RMF | Recommended |
The 2026 regulatory shift: Before August 2026, system cards were a best practice promoted by AI labs. After August 2, 2026 — when EU AI Act Article 50 obligations became active — system cards became a legal documentation requirement for any organization deploying AI that interacts with users in the EU market. The transition from voluntary practice to legal obligation took less than two years.
The practical implication for governance teams is clear. Organizations that treated system cards as optional in 2024 now face a concrete legal exposure if their EU-facing AI systems lack proper Article 13 documentation. The full landscape of 2026 AI regulatory obligations — including which US state laws have passed, which are pending, and what each requires — is covered in the AI Regulation in 2026 guide. For organizations using the NIST AI Risk Management Framework as their governance standard, the NIST AI RMF guide covers how system card documentation maps to the GOVERN and MANAGE functions of the framework.
📝 AI System Card Template: The 10 Sections Every Card Must Include (2026)
The practical barrier most organizations face when producing their first system card is not understanding what a system card is — it is knowing exactly what to put in each section. Generic guidance to “document your system” is not actionable. The 10-section framework below is the structured content reference that converts the regulatory requirement into a completable task. Every section maps directly to at least one EU AI Act Article 13 requirement, an ISO 42001 documentation obligation, or an enterprise procurement expectation. Every field that is left blank is a compliance gap.
Two principles govern effective system card content. First, specificity beats comprehensiveness: a system card that says “the system may produce incorrect outputs in some scenarios” satisfies no one. A system card that says “the system has a documented 4.1% error rate on multi-step calculation tasks and should not be used as the sole source for financial reporting without human review” is the kind of specific, actionable disclosure that satisfies Article 13 and builds genuine user trust. Second, the audience for a system card is not the ML team — it is the business decision-maker, the end user, the procurement officer, and the regulator. Write for that audience, not for the data scientist who built the system.
| Section | What to Document | Example Entry |
|---|---|---|
| 1. System Overview | Name, version, deployment date, operator | “CustomerAssist v2.1 — deployed March 2026 by [Org]” |
| 2. Intended Use | Primary use case, intended users, geographic scope | “Customer service triage for UK retail customers” |
| 3. Underlying Model | Model name, version, provider, model card reference | “GPT-5.x via Azure OpenAI — see OpenAI model card [link]” |
| 4. System Inputs | What data the system receives | “Customer chat text, order ID, account tier” |
| 5. System Outputs | What the system produces | “Suggested response, escalation flag, sentiment score” |
| 6. Safeguards and Guardrails | Content filters, output restrictions, human review gates | “Profanity filter active; medical/legal topics escalate to human” |
| 7. Known Limitations | What the system cannot reliably do | “Cannot process non-English queries; accuracy drops on technical returns” |
| 8. Bias and Fairness | Evaluated populations, known disparities | “Tested across 6 customer segments — no statistically significant disparity found” |
| 9. Human Oversight Mechanism | How humans monitor, override, or intervene | “Supervisor dashboard — all escalations reviewed within 4 hours” |
| 10. Incident Reporting | How to report failures or harmful outputs | “Report to [contact] — logged in AI incident register within 24 hours” |
Critical compliance gap: A system card without a human oversight section (Section 9) does not satisfy EU AI Act Article 14. Documenting what the system does is not enough — you must document how humans monitor it, how they can override it, and who is accountable when it fails. Article 14 makes human oversight a design requirement, not an afterthought.
Two sections consistently produce the weakest content in first-draft system cards. Section 7 (Known Limitations) is frequently vague — “the system may produce errors in some contexts” tells no one anything actionable. A complete Section 7 names specific failure modes, specific task categories where accuracy degrades, and specific input types the system handles poorly. Section 8 (Bias and Fairness Assessment) is frequently omitted entirely or completed with “no known biases” — which satisfies neither Article 13’s requirement for disaggregated performance data nor the expectations of a procurement reviewer who has seen AI systems fail across demographic groups. Both sections require honest, specific, named disclosures. For the full human oversight design framework that feeds into Section 9, the human-in-the-loop implementation guide covers approval gates, override mechanisms, and accountability structures in detail. For incident reporting procedures that align with Section 10 requirements, the AI incident response playbook provides the operational framework.
⚠️ When AI System Cards Are Not Sufficient — 4 Limitations to Plan For
A well-maintained system card is a necessary component of responsible AI deployment. It is not, by itself, sufficient. Four specific scenarios consistently produce situations where organizations rely on their system card as evidence of compliance or governance maturity, when in fact the system card is documenting a deployment context that has fundamentally changed — or covering a system type for which the standard system card format is inadequate. Understanding these limitations before they surface in an audit or incident is the mark of a mature AI governance programme.
Dynamic Systems That Change Post-Deployment
A system card documents a point-in-time deployment — the system as it existed on the date the card was written. If the underlying model is updated by the vendor, the RAG knowledge base is refreshed with new documents, the system prompt is revised, or any other material change is made to the system’s behavior, the system card is immediately outdated. This is not a theoretical concern: most enterprise AI deployments are dynamic systems that change frequently. Cloud-hosted models are updated without notice by providers. RAG pipelines are refreshed on weekly or monthly cycles. System prompts are revised by product teams between governance reviews. An organization that writes a system card at deployment and treats it as a static document will have a card that describes a system that no longer exists within months. The governance requirement is not to write a system card — it is to maintain a current system card. Every material change triggers an update obligation, and that obligation must be built into the change management process before deployment, not discovered during an audit.
Agentic AI Systems with Tool Access
Standard system card templates — including the 10-section framework above — were designed for conversational or analytical AI systems that receive inputs and produce outputs. Agentic AI systems that plan multi-step tasks, execute code, call external APIs, read and write files, and take real-world actions are fundamentally different systems. They require additional documentation that standard system card formats do not provide: the specific tools the agent can access, the permissions granted to each tool, the action boundaries beyond which the agent cannot operate, and the rollback mechanism that can reverse agent actions if they go wrong. An agentic system documented only with a standard system card has a documentation gap that will be visible to any sophisticated reviewer. The agentic AI governance guide covers the additional documentation and governance controls that agentic deployments require beyond the system card.
Third-Party Model Dependencies and the Version-Pinning Problem
A system card that documents a deployment built on a closed-source model faces a fundamental accuracy limitation: the system card’s guarantees about system behavior are only as accurate as the provider’s model behavior — and closed-source providers can update their models without notice. When OpenAI, Anthropic, Google, or another provider updates their model, the safety properties, performance characteristics, and known failure modes documented in your system card may no longer be accurate, even though nothing on your side has changed. Organizations relying on closed-source models should address this in two ways: first, include a contractual model version pinning clause in vendor agreements that requires notice before model updates; second, treat vendor-initiated model updates as a mandatory system card review trigger. Without both measures, your system card can become factually inaccurate through no action of your own. Third-party AI risk management — including how to contractually protect your governance documentation accuracy — is covered in the third-party AI vendor risk framework.
Legal Accountability in Regulated Decisions
A system card demonstrates transparency. It does not, by itself, demonstrate legal compliance. This distinction matters significantly for organizations deploying AI in regulated contexts. For EU AI Act Annex III high-risk systems, a completed system card is one input to the formal conformity assessment process — it is not the conformity assessment itself. Conformity assessment for high-risk systems requires formal risk registers aligned with Article 9, technical documentation meeting the full Annex IV requirements, in some cases third-party audit by a notified body, and a CE marking process that a system card alone cannot satisfy. Organizations that present their system card as their Article 13 compliance evidence without the supporting technical documentation package will face a significant gap when a notified body or market surveillance authority requests the full conformity assessment record. The system card is the most visible part of the documentation stack. It is not the whole stack.
🔒 Building an AI governance framework? Browse the AI Buzz Governance & Security Hub — in-depth guides covering OWASP, NIST, ISO 42001, AI risk management, and enterprise AI security frameworks.
🤔 1. What Is an AI System Card? (And How It Differs From a Model Card)
An AI system card is a structured document that describes a deployed AI application — the complete system that end users interact with. It covers the intended use, capabilities, limitations, safety measures, human oversight mechanisms, data handling practices, and accountability structures of the live product. It is written at the application layer, not the model layer. This distinction matters more than it might initially appear, and confusing the two is the most common documentation error organizations make when building their AI governance programs.
Plain-English definition: A model card describes the AI model — its training data, benchmark scores, and technical characteristics. A system card describes what your organization built on top of that model — the application, its safety policies, its users, its deployment context, and who is responsible when something goes wrong. A hospital deploying an AI triage tool writes a system card. The company that trained the underlying model writes the model card. Both documents are required. They cover different layers.
The practical difference can be illustrated with a concrete example. OpenAI publishes model cards for its GPT model family — documenting training methodology, benchmark performance, and known failure modes at the model level. When a healthcare organization deploys an internal documentation assistant built on GPT-5.x, that organization is responsible for writing a system card that describes their specific application: what patient data it accesses, what clinical decisions it is prohibited from making, what human review process is in place before its outputs are acted upon, and how a clinician can escalate a concern. The model card tells you about the engine. The system card tells you about the car — and who is driving it, under what rules, for what purpose.
A third document — the Datasheets for Datasets format — covers the training data used to create the model. In a complete AI documentation program, all three documents exist and reference each other. The system card is the top-level artifact: it points to the model card of the underlying model and to the dataset documentation, while adding the application-specific governance layer that neither of those documents can provide. For a complete understanding of how AI risk assessment feeds into system card documentation, see the risk assessment guide — a completed risk register is the primary input to the system card’s limitations and risk mitigation sections.
🏢 2. Who Needs an AI System Card in 2026?
System cards are no longer only for frontier AI labs publishing voluntary transparency reports. The combination of EU AI Act enforcement, US state-level AI legislation, and enterprise procurement standards has expanded the mandatory audience significantly. The practical question is not “are we big enough to need one?” — it is “do we deploy AI that affects consequential decisions?” If the answer is yes, you need a system card.
IBM’s 2026 AI governance research confirms that enterprise AI documentation requirements have cascaded from frontier labs to enterprise deployers, with 78% of large organizations now requiring system-level documentation from AI vendors before procurement approval. The EU AI Act’s Article 13 obligations apply to providers of high-risk AI systems — but critically, Article 4(10) defines a “deployer” as any natural or legal person that uses an AI system under their authority, and deployers of high-risk systems carry their own compliance obligations including ensuring that operators receive the information required by Article 13. In practice, this means any organization that deploys a third-party high-risk AI system must maintain their own system-level documentation, even if they did not build the underlying model.
| Organization Type | System Card Required? | Why / Which Obligation |
|---|---|---|
| Enterprise deploying third-party AI via API (e.g., GPT-5.x for document review) | ✅ Required | EU AI Act deployer obligations under Article 26 + Article 13 information requirements. Enterprise procurement standards increasingly require it regardless of EU scope. |
| Organization building custom AI application on foundation model (e.g., fine-tuned Claude for internal HR workflows) | ✅ Required | Provider + deployer obligations both apply. ISO 42001 Section 6.1.2 requires documented AI system information at the application layer. |
| EU AI Act Annex III high-risk deployer (hiring screening, credit scoring, healthcare triage) | ✅ Mandatory | Article 13 (transparency) + Article 11 (technical documentation via Annex IV) are mandatory obligations. Non-compliance: fines up to €15 million or 3% of global turnover. |
| Organization responding to enterprise procurement questionnaires or vendor security reviews | ✅ Expected | 78% of large enterprises now require system-level AI documentation before procurement approval (IBM, 2026). Absence of a system card frequently blocks sales cycles. |
| AI vendor selling to enterprise clients | ✅ Required | Enterprise clients will request it before signing. EU deployer clients cannot fulfill their Article 13 obligations without receiving adequate system documentation from providers. |
| SMB using AI tools for internal workflows (e.g., Copilot for email, ChatGPT for drafting) | 💡 Recommended | Not legally mandatory for non-high-risk internal tools. But a lightweight system card creates an accountability trail, supports employee policy training, and demonstrates diligence if a data incident occurs. |
| US bank deploying AI for credit decisions or fraud detection | ✅ Required | SR 26-2 (Fed/OCC/FDIC, April 17, 2026) requires model risk documentation for traditional AI models in banking. ECOA and fair lending obligations apply regardless of AI governance rules. |
| Colorado employer using AI for hiring or employment decisions | ✅ Required | Colorado SB 26-189 (signed May 14, 2026, effective January 1, 2027) requires impact assessments and consumer disclosures for high-risk AI in employment. System card documentation is the primary evidence artifact. |
📊 3. System Card vs Model Card vs Dataset Datasheet — Side-by-Side
The three core AI transparency documents address different layers of the AI stack and serve different audiences. Understanding which document covers what — and when you need each — prevents both documentation gaps and duplication of effort. All three documents reference each other and together form a complete AI transparency record, but only the system card addresses the deployed application layer that regulators and enterprise buyers are asking about.
| Dimension | AI System Card | AI Model Card | Dataset Datasheet |
|---|---|---|---|
| Describes | The deployed application users interact with | The ML model artifact — weights, benchmarks, architecture | The training dataset — provenance, quality, bias characteristics |
| Written by | The organization deploying the AI application | The team that trains the model | The team that created or curated the dataset |
| Primary audience | End users, regulators, procurement teams, executives | Data scientists, ML engineers, AI governance teams | ML researchers, data governance teams, auditors |
| Key content | Safety policies, human oversight, permitted uses, redress mechanisms, accountability owner | Training data summary, benchmark scores, known failure modes, demographic performance | Data provenance, collection methods, known biases, intended and prohibited uses |
| Update trigger | Deployment context change, model version update, safety policy change, security incident | New model version, new evaluation results, new known failure mode | Dataset update, new bias audit, correction of data provenance |
| EU AI Act Article 13 role | ✅ Primary compliance artifact | ⚠️ Supporting artifact (model-layer evidence) | ⚠️ Supporting artifact (data-layer evidence) |
| ISO 42001 layer | Application layer documentation | Model layer documentation | Data layer documentation |
When Do You Need Each Document? A Practical Decision Guide
The table above shows what each document covers. The practical question is: given your specific situation, which documents are you responsible for creating? The answer depends on your role in the AI value chain. Use this decision guide before your next AI audit checklist review:
| Your Situation | System Card | Model Card | Dataset Datasheet |
|---|---|---|---|
| Deploying a third-party AI tool (e.g., via API) | ✅ You create it | Request from vendor | Request from vendor |
| Fine-tuning an open-weight model on your data | ✅ You create it | ✅ You create it | ✅ For fine-tuning data |
| Building custom AI from scratch | ✅ You create it | ✅ You create it | ✅ You create it |
| EU AI Act Article 13 compliance | ✅ Primary artifact | ⚠️ Supporting artifact | ⚠️ Supporting artifact |
| ISO 42001 documentation requirement | ✅ Application layer | ✅ Model layer | ✅ Data layer |
| Enterprise vendor due diligence request | ✅ Provide this | ✅ Provide this | ✅ If applicable |
📝 4. The Complete AI System Card Template (Copy-Paste Ready — 10 Sections)
The template below is structured to satisfy EU AI Act Article 13 requirements, ISO 42001 Section 6.1.2 documentation standards, and enterprise procurement questionnaire expectations simultaneously. Every field maps to at least one regulatory or governance requirement. Complete every section before deploying any AI system that affects consequential decisions. Sections marked ⚠️ are mandatory for EU AI Act high-risk systems.
How to use this template: Complete every section in plain English — avoid technical jargon wherever possible, since the primary audience for a system card is not the ML team but the people making deployment decisions, users seeking accountability, and regulators verifying compliance. Assign a named owner to each section. Every field that is left blank or marked “TBD” is a compliance gap and an audit risk. Version this document from the first draft — do not treat it as a living document without version control.
Section 1: System Overview ⚠️
- System Name: [The product or internal name of the AI application]
- System Card Version: [e.g., v1.0 — increment on every material update]
- Date Last Updated: [Must match actual current state of the system]
- Card Owner: [Named individual — not a team or department]
- System Description: [2–3 sentences: what it does, what input it receives, what output it produces]
- Underlying Model(s): [Name and version of all AI models used — e.g., GPT-5.x, Claude Sonnet 4.5]
- Model Card Reference: [Link or document reference to the model card for each underlying model]
- Deployment Status: [In development / Beta / Production / Deprecated]
Section 2: Intended Use and Users ⚠️
- Primary Use Cases: [Specific tasks this system is designed to perform — be precise]
- Intended Users: [Who uses this system — role, technical level, organizational context]
- Deployment Contexts: [Where it is deployed — which teams, which geographies, which workflows]
- Out-of-Scope Uses: [Explicitly list tasks or contexts this system is NOT designed for and must not be used for]
- High-Risk Classification: [Is this system high-risk under EU AI Act Annex III? Yes / No / Under assessment — explain]
Section 3: Capabilities and Known Limitations ⚠️
- Core Capabilities: [What the system does well — be specific, not promotional]
- Known Limitations: [Specific failure modes, accuracy boundaries, unsupported languages or formats]
- Performance Metrics: [Disaggregated by relevant subgroups — not aggregate only. Aggregate accuracy is insufficient for Article 13 compliance.]
- Hallucination/Error Risk: [Describe the nature and frequency of incorrect outputs in this deployment context]
- Bias and Fairness Assessment: [Document any known demographic or contextual performance disparities and mitigations]
Section 4: Safety Measures and Content Policies ⚠️
- Content Filters Active: [List all active safety filters and what content categories they block]
- System Prompt and Guardrails: [Summarize the system prompt scope — do not expose the full system prompt if confidential, but document its protective intent]
- Adversarial Input Mitigations: [What protections exist against prompt injection, jailbreaking, and misuse?]
- Prohibited Outputs: [Explicitly list output types this system will not produce]
- Safety Policy Last Reviewed: [Date — must be current]
Section 5: Human Oversight and Review ⚠️
- Human-in-the-Loop Design: [Describe where human review is required before AI output is acted upon]
- Approval Gates: [Which output types require mandatory human approval before use?]
- Override Mechanism: [How can a human override or correct the system’s output?]
- Consequential Decision Restriction: [Explicitly state whether this system can make final consequential decisions autonomously or whether human review is mandatory]
Section 6: Data Handling and Privacy
- Input Data Types: [What data does this system receive as input?]
- Data Retention: [How long is input and output data retained? Where is it stored?]
- Training on User Data: [Is this system’s model trained or fine-tuned on user inputs? Yes / No — explain]
- PII Handling: [What controls prevent PII from being processed or retained inappropriately?]
- AI Disclosure to Users (Article 50): [How are users notified they are interacting with an AI system? What disclosure mechanism is in place?]
- Dataset Datasheet Reference: [Link or document reference for training data documentation, if applicable]
Section 7: Accountability and Contact
- System Owner: [Named individual with governance responsibility for this system]
- Technical Owner: [Named individual responsible for technical maintenance and monitoring]
- Feedback Channel: [How can users report issues, errors, or concerns?]
- Escalation Path: [Who does the technical owner escalate to for safety or compliance concerns?]
- EU Authorised Representative: [Required for non-EU providers — name and contact details]
Section 8: Regulatory Compliance ⚠️
- EU AI Act Article 13 Status: [Compliant / In progress / Not applicable — explain]
- EU AI Act Article 50 Status: [Disclosure obligations — compliant / in progress / not applicable]
- FRIA Completed: [Fundamental Rights Impact Assessment — Yes / No / In progress]
- Colorado SB 26-189: [Impact assessment and consumer disclosure obligations — applicable? Compliant? Effective January 1, 2027.]
- Other Applicable Regulations: [GDPR, HIPAA, SR 26-2, Illinois HB 3773, Connecticut PA 26-15 — list all applicable and compliance status for each]
- Conformity Assessment: [For EU Annex III high-risk systems — completed / in progress / not required]
Section 9: Incident Response
- Incident Reporting Channel: [Where are safety incidents or system failures reported internally?]
- External Incident Reporting: [EU AI Act Articles 72–73: serious incidents reported to market surveillance authority within 24 hours (immediate threat) or 72 hours (other serious incidents)]
- Rollback Procedure: [What is the documented process for disabling or reverting the system in an emergency?]
- Post-Incident Review Process: [Who conducts the review? What outputs are required?]
Section 10: Version History and Retention
- Version Log: [Table of all previous versions — version number, date, summary of changes, change author]
- Retention Period: [Minimum 10 years for EU AI Act high-risk systems (Article 12). State your organization’s retention policy.]
- Review Schedule: [Minimum annual review. State next scheduled review date and owner.]
- Related Documents: [Links to model card, dataset datasheet, risk register, FRIA, DPA/DPIA]
🌍 5. Real Examples: How OpenAI, Anthropic, and Meta Do System Cards in 2026
The three organizations whose system cards have most influenced industry practice each take a distinct approach — reflecting their different deployment models, risk profiles, and regulatory postures. Studying their approaches reveals what effective system card documentation looks like at scale, and which elements your organization should adapt for your context.
OpenAI publishes detailed system cards for each major model release that combine the model-level technical documentation with application-layer safety information. Their system cards include specific red-teaming results, dangerous capability evaluations (CBRN, cyberweapons, persuasion), and explicit prohibited use policies. The GPT-4o system card documents specific jailbreak evaluations and the mitigations applied — setting a benchmark for safety transparency that enterprise deployers are increasingly expected to reference in their own system cards.
Anthropic structures its system cards around Claude’s Constitutional AI framework — documenting how the model’s values and safety behaviors were instilled through RLHF and Constitutional AI training. Anthropic’s approach is distinctive for its explicit documentation of model behavior in adversarial conditions and its transparency about what Claude will and will not do in specific scenarios. For enterprise deployers building applications on Claude, Anthropic’s system card serves as the primary reference for which behaviors are hardcoded (cannot be overridden by system prompt) versus instructable (can be modified by the deployer).
Meta publishes system cards for its open-weight model releases that are particularly valuable for organizations fine-tuning and self-hosting Meta models. Meta’s documentation focuses heavily on responsible use guidelines, acceptable use policies, and the specific evaluation frameworks applied before release — including MMLU benchmark results disaggregated by category. For organizations building on open-weight models like Llama 4, Meta’s system card is the starting point for their own application-level system card — organizations must then add their deployment-specific safety measures, data handling policies, and accountability structures on top of what Meta provides.
What the best system cards have in common: The system cards that consistently satisfy enterprise procurement reviews and regulatory audits share four characteristics. First, they are specific — not “this system may produce incorrect outputs” but “this system has a documented 3.2% error rate on financial calculation tasks, disaggregated by calculation type.” Second, they are current — dated within the last 90 days and reflecting the actual current state of the system. Third, they name owners — a person, not a team. Fourth, they describe limitations honestly — systems with no documented limitations are treated as untrustworthy by experienced procurement teams, because every AI system has limitations.
⚖️ 6. EU AI Act Article 13 and Article 50: System Card Compliance Mapping
EU AI Act Article 13 (Transparency and Provision of Information) requires providers of high-risk AI systems to design and develop systems in a way that ensures deployers receive sufficient information to use the system appropriately and fulfill their obligations. Article 50 (Transparency Obligations for Certain AI Systems) applies from August 2, 2026 to all AI systems that interact with humans — requiring users to be notified they are interacting with an AI system. Together, these two articles define the minimum content requirements for a compliant system card for high-risk EU deployments.
Critical 2026 compliance update: the EU’s Digital Omnibus agreement reached May 7, 2026 and endorsed by the European Parliament on June 16, 2026 delayed the Annex III (high-risk AI) full obligation deadline from August 2, 2026 to December 2, 2027. However, this delay applies only to Annex III systems. Article 50 transparency obligations — AI disclosure requirements — apply in full from August 2, 2026 with no deferral. Organizations should plan all Annex III compliance work to the December 2027 date while treating Article 50 obligations as active now. Colorado SB 26-189 (signed May 14, 2026, effective January 1, 2027) applies independently of EU law to any organization using high-risk AI in consequential decisions affecting Colorado residents — including employment, lending, healthcare, education, and housing.
| EU AI Act Requirement | Article | System Card Section That Satisfies It | Deadline | Your Status |
|---|---|---|---|---|
| System identity, intended purpose, and provider identity disclosed to deployers | Art. 13(1) | Section 1 (System Overview) + Section 2 (Intended Use) | Dec 2, 2027 | ☐ |
| Performance characteristics, limitations, and known failure modes disclosed | Art. 13(3)(b) | Section 3 (Capabilities and Limitations) — must be disaggregated by relevant subgroup | Dec 2, 2027 | ☐ |
| Human oversight measures documented — how and by whom oversight is exercised | Art. 13(3)(e) + Art. 14 | Section 5 (Human Oversight and Review) | Dec 2, 2027 | ☐ |
| Automatic logging capability documented — technical capacity for Article 12 logs | Art. 12 | Section 4 (Safety Measures) + Section 9 (Incident Response) | Dec 2, 2027 | ☐ |
| Users notified they are interacting with an AI system | Art. 50(1) | Section 6 (AI Disclosure to Users) | Aug 2, 2026 ✅ ACTIVE NOW | ☐ |
| Content generated by AI is disclosed as AI-generated (deepfakes, synthetic media) | Art. 50(2) | Section 6 (Data Handling and Privacy) | Dec 2, 2026 (transitional for systems already on market) | ☐ |
| Serious incident reporting to national market surveillance authority | Art. 72–73 | Section 9 (Incident Response) — must specify 24h/72h reporting timeline | Dec 2, 2027 | ☐ |
| Technical documentation retained for minimum 10 years | Art. 12(1) | Section 10 (Version History and Retention) | Dec 2, 2027 | ☐ |
For a complete walkthrough of your organization’s EU AI Act obligations beyond Article 13, the EU AI Act compliance guide covers all risk tiers, conformity assessment requirements, and the full implementation timeline including the Digital Omnibus deferral details. For US-specific obligations, Colorado SB 26-189 (effective January 1, 2027) applies to any organization using high-risk AI in consequential decisions affecting Colorado residents. SR 26-2 — issued by the Federal Reserve, OCC, and FDIC on April 17, 2026 — applies to traditional AI models in banking and requires model risk documentation aligned with the system card framework, though SR 26-2 explicitly excludes generative and agentic AI from its scope.
📋 7. AI System Card Maintenance Checklist: When and How to Update
The 2026 compliance standard for AI system cards: “A system card written once and never updated is not a compliance document — it is a historical record that describes how the system used to work. EU AI Act Article 13 requires that deployers receive information about the system’s current state. A static document describing a previous model version, an outdated safety policy, or a performance characteristic that no longer applies is not compliant documentation — it is evidence of a governance failure.”
The single most common system card failure identified in EU AI Act compliance audits and enterprise procurement reviews is not a missing section — it is a document that was written before deployment and never updated. Every time the underlying model is updated by your vendor, every time your safety policy changes, every time you extend the system to a new use case or deployment context, the system card must be updated before that change goes live. Treating the system card as a living document with version control is not optional — it is the difference between a compliance artifact and a historical record.
The maintenance framework below defines the trigger events that require a system card update, the action required, the responsible owner, and the maximum acceptable timeline. Organizations should configure their AI governance calendar to include these triggers as formal review events, not ad hoc checks. For the full governance process that integrates system card maintenance with ongoing monitoring, see the AI Audit Checklist.
| Trigger Event | Action Required | Owner | Maximum Timeline |
|---|---|---|---|
| Model version update by vendor | Review and update Section 1 (model reference), Section 3 (capabilities/limitations), Section 4 (safety measures if changed) | AI Governance Lead + Technical Owner | Within 14 days of change going live |
| Safety policy or content filter change | Update Section 4 (Safety Measures and Content Policies). If change expands permitted outputs — escalate to legal review before implementation. | Compliance Team + System Owner | Before change goes live — not after |
| New deployment context added | Full system card review — Section 2 (Intended Use), Section 8 (Regulatory Compliance) especially if new geography triggers new legal obligations | Product Owner + Legal + Compliance | Before new deployment goes live |
| Performance degradation alert from monitoring | Update Section 3 (Capabilities and Known Limitations) to reflect confirmed drift. Notify affected users if performance is materially different from documented levels. | Technical Owner + AI Governance Lead | Within 7 days of confirmed drift |
| Regulatory change affecting the system | Update Section 8 (Regulatory Compliance). Assess whether new obligation triggers a FRIA or conformity assessment. Engage legal counsel for material changes. | Legal / Compliance | Within 30 days of regulatory effective date |
| Security incident or safety event | Update Section 4 (Safety Measures) and Section 9 (Incident Response). For EU AI Act serious incidents: report to national market surveillance authority within 24h (immediate threat) or 72h (other serious incidents). | CISO + System Owner | Within 72 hours of incident confirmation |
| Annual scheduled review (minimum cadence) | Full system card review against current system state. Verify all 10 sections reflect actual current operation. Update version number even if no material changes — confirms active maintenance. | Named Card Owner | Every 12 months — calendar this as a hard deadline |
Version control requirements for compliant system cards: Every update creates a new version number using semantic versioning (v1.0, v1.1, v2.0 for major changes). Previous versions are archived — not deleted or overwritten. Every material change is documented in the changelog with a date, a description of what changed, and the name of the person who made the change. For EU AI Act high-risk systems, Article 12 requires records to be retained for a minimum of 10 years — which means your version history and all previous versions must be stored in a durable, auditable location from day one of deployment.
🏁 8. Conclusion: A System Card Is Your Organization’s AI Accountability Record
The 2026 consensus is clear: AI system cards have moved from voluntary transparency practice to operational necessity. For any organization deploying AI in consequential decisions — and for any vendor selling AI tools to enterprise clients — a well-maintained system card is the evidence artifact that answers the question every regulator, procurement team, and board member is now asking: “How do you know this AI system is working as intended, within appropriate limits, with proper human oversight, and in compliance with applicable law?” A system card that cannot answer all of those questions is not a compliance document. It is a gap waiting to become a liability.
The most important principle from the enterprise AI governance experience of 2026 is that documentation written once and never updated is worse than no documentation at all — it creates a false impression of compliance while describing a system that no longer exists. Build your system card maintenance triggers into your AI governance calendar before you deploy. Assign a named owner. Version every update. And use the EU AI Act Article 13 compliance table above as your minimum content standard — not your ceiling. The organizations that treat system card documentation as operational infrastructure rather than a compliance exercise are the ones whose AI deployments survive regulatory scrutiny, pass enterprise procurement reviews, and maintain user trust when issues arise. For a complete governance program that goes beyond the system card, the AI governance framework guide covers the full accountability structure your organization needs in 2026.
📌 9. Key Takeaways
| 📌 | Takeaway |
|---|---|
| ✅ | An AI system card documents the deployed application — not the underlying model. A model card documents the ML artifact. A dataset datasheet documents the training data. All three exist in a complete AI documentation program, but only the system card satisfies EU AI Act Article 13’s deployer-facing transparency requirement. |
| ✅ | EU AI Act Article 50 transparency obligations (user disclosure) are active from August 2, 2026 with no deferral. Annex III high-risk AI obligations are deferred to December 2, 2027 under the Digital Omnibus agreement — but compliance preparation must begin now. |
| ✅ | 78% of large enterprises now require system-level AI documentation from vendors before procurement approval (IBM, 2026). The absence of a system card is increasingly a direct blocker in enterprise sales cycles. |
| ✅ | SR 26-2 (Federal Reserve, OCC, FDIC — April 17, 2026) requires model risk documentation for traditional AI in banking. It explicitly excludes generative and agentic AI from scope — banks deploying LLMs or AI agents must look to separate governance frameworks for those systems. |
| ✅ | The most common system card audit failure is a document that was never updated after initial deployment. Every model version change, safety policy update, new deployment context, and security incident requires a system card update with a new version number before the change goes live. |
| ✅ | Article 13 requires disaggregated performance data by relevant subgroups — not aggregate accuracy figures. A system card reporting only an overall accuracy percentage does not satisfy Article 13’s requirement for information sufficient to assess deployment-specific risks. |
| ✅ | EU AI Act Article 12 requires technical documentation for high-risk systems to be retained for a minimum of 10 years — meaning every version of your system card must be archived from the date of first deployment. |
| ✅ | Colorado SB 26-189 (signed May 14, 2026, effective January 1, 2027) applies independently of EU law — any organization using high-risk AI in consequential decisions affecting Colorado residents must maintain impact assessments and consumer disclosures that align directly with system card documentation requirements. |
| ✅ | A model card and a system card serve different purposes and satisfy different EU AI Act obligations — model cards address Article 10 (training data documentation) while system cards address Article 13 (transparency to deployers and users). Both are required for high-risk AI deployments — neither substitutes for the other. |
| ✅ | Key residual risk: A system card documents the AI system as deployed at a point in time. Any material change — model update, system prompt change, RAG knowledge base refresh, new user population — creates an obligation to update the system card. Outdated system cards create compliance gaps under EU AI Act Article 13. |
🔗 Related Articles
- 📖 AI Model Cards Explained: How to Document an AI System for Transparency, Risk, and Trust
- 📖 EU AI Act Explained: A Practical Compliance Guide and Checklist
- 📖 Datasheets for Datasets Explained: How to Document AI Data for Quality, Privacy, and Bias Risk
- 📖 Agentic AI Governance: How to Govern Autonomous AI Agents in 2026
- 📖 AI Regulation in 2026: 7 New Laws Reshaping How Businesses Use AI
❓ Frequently Asked Questions: AI System Card Template
1. What is an AI system card and how does it differ from a model card?
An AI system card documents the deployed application your users interact with — its safety policies, permitted uses, human oversight, and accountability structures. An AI model card documents the underlying ML model — its training data, benchmarks, and technical limitations. You need both: the vendor provides the model card; you create the system card for your deployment. See our AI model cards guide for the model-layer equivalent.
2. Is an AI system card required for EU AI Act Article 13 compliance?
Yes, for high-risk AI systems under Annex III. Article 13 requires providers to give deployers sufficient information about the system’s capabilities, limitations, and oversight mechanisms — and a system card is the primary artifact that satisfies this requirement. EU AI Act Article 50 (user disclosure) is active now from August 2, 2026. Annex III obligations were deferred to December 2, 2027 under the Digital Omnibus agreement. See our EU AI Act compliance guide for the full timeline.
3. Who is responsible for writing the AI system card — the vendor or the deployer?
Both may need one, but for different reasons. The vendor (provider) is responsible for supplying information that satisfies Article 13 obligations. The deployer is responsible for creating application-level documentation covering their specific deployment context — safety policies, human oversight, permitted use restrictions, and accountability structures that the vendor cannot know. If you deploy a third-party AI tool, you create the system card for your deployment; you request the model card from the vendor.
4. How often does an AI system card need to be updated?
At minimum annually, but specific trigger events require immediate updates: any model version change by the vendor (within 14 days), any safety policy change (before it goes live), any new deployment context (before deployment), any confirmed performance degradation (within 7 days), and any security incident (within 72 hours). For EU AI Act high-risk systems, all versions must be archived for 10 years under Article 12. Our AI monitoring and observability guide explains how to detect the trigger events that require updates.
5. Does SR 26-2 require banks to produce AI system cards?
SR 26-2 (Federal Reserve, OCC, FDIC — April 17, 2026) requires model risk documentation for traditional AI models used in banking — credit scoring, fraud detection, model-based decisions. However, SR 26-2 explicitly excludes generative AI and agentic AI from its scope. Banks deploying LLMs or AI agents must apply separate governance frameworks for those systems. An AI system card aligned with the template in this guide satisfies the documentation spirit of SR 26-2 for in-scope traditional models, while also preparing banks for the broader governance requirements that will eventually cover generative and agentic systems. See our AI governance framework guide for the complete accountability structure.
📧 Get the AI Buzz Weekly Digest
Weekly AI insights, tools, and strategies — delivered every Monday. Free.
Leave a Reply