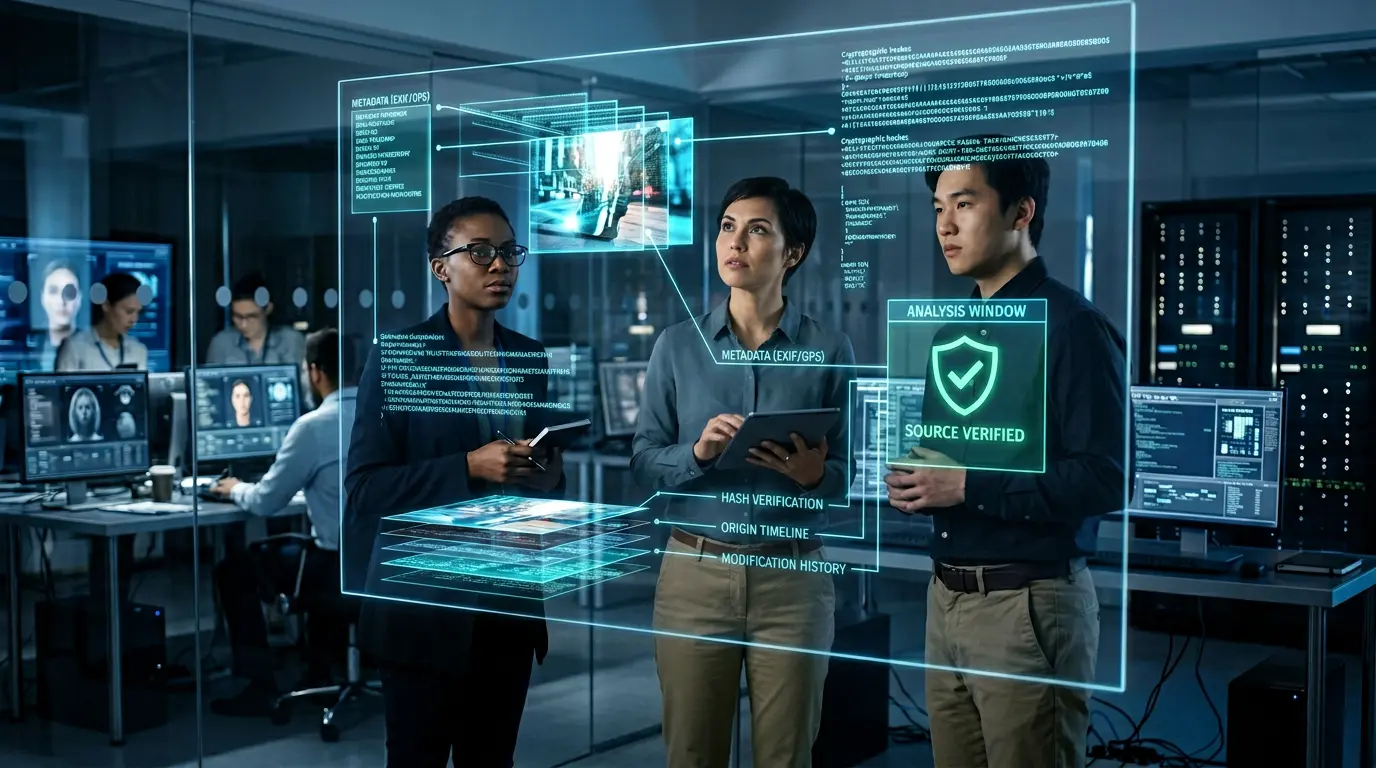
🔍 Can You Trust What You See Online? In 2026, AI-generated images, videos, and text are indistinguishable from reality to the naked eye. Digital provenance — the science of verifying where content came from and whether it has been altered — is the most important tool we have for protecting truth online. This guide explains exactly how it works and why it matters.
Last Updated: October 6, 2026
A photograph of a world leader signing a document that never existed. A video of a CEO announcing a product recall that never happened. An audio clip of a judge delivering a ruling that was never made. In 2026, none of these require a sophisticated nation-state actor or a Hollywood production budget to create. They require a consumer AI tool, a few minutes, and a basic understanding of how to write a prompt. The technology to fabricate convincing digital content has democratized at extraordinary speed — and the systems we rely on to distinguish real from fake have not kept pace. The result is an information environment under unprecedented stress, where the question “Is this real?” has become one of the most consequential questions a person can ask.
Digital provenance is the field dedicated to answering that question systematically — not through human judgment alone, but through technical standards, cryptographic verification, and metadata frameworks that allow any piece of digital content to carry a verifiable record of its origins, its creator, and every modification it has undergone. Think of it as a chain of custody for information — the same principle that makes a signed legal document or a notarized contract more trustworthy than an unsigned copy, applied to every photograph, video, audio file, and text document that circulates online. According to the World Economic Forum’s research on digital trust, the erosion of content authenticity is now ranked among the top five global risks to democratic institutions and economic stability — making digital provenance not just a technical challenge but a societal imperative.
This guide provides a comprehensive, plain-language explanation of digital provenance in 2026 — covering the core technical standards (C2PA, Content Credentials, and AI watermarking), the real-world tools and platforms already implementing these systems, the limitations that honest advocates must acknowledge, and the practical steps that journalists, businesses, creators, and everyday users can take to participate in a more trustworthy information ecosystem. Whether you are a content creator who wants to authenticate your original work, a journalist evaluating the credibility of submitted content, a business leader concerned about deepfake threats to your brand, or simply a citizen trying to navigate an increasingly unreliable information environment, this guide gives you the framework to do so with confidence. For a detailed comparison of the specific technical methods used to embed provenance — including AI watermarking, metadata standards, and C2PA content credentials across platforms, see our guide to AI Watermarking vs Metadata vs Fingerprinting.
📖 New to AI terminology? Visit the AI Buzz AI Glossary — 100+ essential AI terms explained in plain English, each linking to a full in-depth guide.
📷 1A. C2PA-Enabled Cameras and Devices: Which Hardware Supports Content Credentials in 2026
Hardware-level provenance is the gold standard of content authentication — and the reason is straightforward. When a camera’s signing key is provisioned at the factory and stored in a dedicated hardware security chip, the cryptographic signature is embedded in the image file at the exact moment of capture, before any human has had the opportunity to edit, manipulate, or alter the content. There is no gap in the chain of custody between the sensor and the signed file. This is fundamentally different from software-applied credentials — which can be added to any file, by anyone, at any time after capture — and it is why camera manufacturers implementing C2PA at the hardware level are providing the most tamper-resistant form of provenance available in the ecosystem today. A journalist’s photograph taken on a C2PA-enabled camera carries a credential that says: this specific camera, with this serial number, captured this frame at this timestamp — and the mathematical seal on that claim cannot be forged without compromising the hardware itself.
The 2026 C2PA hardware ecosystem has expanded rapidly from a single manufacturer in 2023 to a meaningful cross-industry deployment spanning professional cameras, broadcast video equipment, and — critically — the first mainstream consumer smartphones. The comparison between hardware signing and software-based watermarking approaches reveals why hardware adoption matters so much: software credentials can be stripped by passing an image through a non-compliant platform, but hardware credentials, when properly implemented using a secure processing unit, establish a verifiable origin point that persists independently of what happens to the file downstream. The table below reflects the current verified C2PA hardware support status as of October 2026, drawn from manufacturer documentation, the C2PA Conformance Programme registry, and independent tracking sources.
| Brand | Supported Model(s) | C2PA Support Method | Content Credentials Level | Status / Notes |
|---|---|---|---|---|
| Leica | M11-P, M11-D, SL3-S, Q3 family (Dec 2025 firmware); Leica SL3-P (Jun 2026) | Dedicated hardware encryption chip provisioned at factory — strongest implementation available | Capture-level signing. Certificate signed via CAI Trust Infrastructure. Records camera serial, timestamp, lens data. | 🟢 Live — first manufacturer to ship (2023). Original SL3 does not support C2PA (lacks hardware chip). M11-P signs by default; M11-D/SL3-S require menu activation. |
| Sony | Alpha 1, Alpha 1 II, Alpha 9 III, Alpha 7S III, Alpha 7 IV, Alpha 7R V, Alpha 7 V, Alpha 7R VI; Video: PXW-Z300, FX3, FX30 (video C2PA) | Firmware update via Sony Creators’ App (paired mobile); signing keys provisioned through Sony Camera Authenticity Solution | Capture-level signing for stills and video. PXW-Z300 was the world’s first video camera to support C2PA. 9 models across stills and video lines covered. | 🟢 Live — founding C2PA member. Piloting with news organizations since 2024. Broadest model coverage of any manufacturer. |
| Nikon | Z9, Z8, Zf (firmware update, 2024); Z6 III (Nikon Authenticity Service, Aug 2025 — note: certificate vulnerability discovered and revoked shortly after launch) | Firmware + cloud-based Nikon Authenticity Service. Signing key stored in Secure Processing Unit (SPU) on main processor board. | Capture-level signing for Z9/Z8/Zf. Z6 III certificates revoked after security researcher found a vulnerability allowing fake images to carry valid signatures — illustrating why hardware implementation rigour matters. | 🟡 Live (Z9/Z8/Zf); ⚠️ Z6 III certificates revoked — do not treat Z6 III credentials as validated until Nikon issues a fix and new certificate. |
| Canon | EOS R1, EOS R5 Mark II (firmware, July 2025). Canon Authenticity Imaging System launched May 2026 (scoped to registered news agencies) | Firmware update + Canon Trust List. C2PA steering committee member — helps define the specification. | Capture-level signing. Initial access limited to registered news organizations. Canon Trust List separate from CAI Trust Infrastructure. | 🟢 Live on R1 and R5 Mark II. Broader consumer access anticipated. Canon is a C2PA steering committee member. |
| Google Pixel | Pixel 10 (native C2PA in Pixel Camera app, all photos signed by default); Pixel 9 (partial support via Proofmode app) | Hardware-backed keys via Titan M2 chip + Tensor G5 on-device timestamping. Achieves C2PA Assurance Level 2 — highest security rating in the Conformance Programme. | Capture-level signing for every photo by default (not just AI-edited images). Credentials viewable in Google Photos. Works offline. First mainstream consumer smartphone with native C2PA. | 🟢 Live — milestone for consumer-scale provenance. Apple has not publicly committed to C2PA as of October 2026. |
| Samsung Galaxy | Galaxy S25 series (AI-edited photos only); Galaxy S26 series (broader support announced) | Qualcomm Snapdragon 8 Elite Secure Processing Unit. C2PA credentials attached automatically when using Samsung AI editing features (Generative Edit, Sketch to Image, Portrait Studio, Drawing Assist, AI Sticker). | AI-edit-level signing only — standard photos taken without AI editing do NOT receive a C2PA credential. Important limitation vs. Pixel 10’s all-photos approach. | 🟡 Live but limited scope. First Android phone to ship C2PA (S25, Jan 2025), but narrower than Pixel 10 implementation. |
| Qualcomm (platform) | Snapdragon ISP pipeline (any phone using Snapdragon with enabled OEM implementation) | C2PA signing integrated at chipset level into Snapdragon ISP since 2024. OEM must enable and provision certificates — Qualcomm supplies the capability, not the trust chain. | Platform-level enabler — multiple Android OEMs can implement C2PA without building their own signing infrastructure. | 🟢 Platform available — OEM activation required. Foundational to Samsung S25 and future Android C2PA deployments. |
The Hardware Provenance Principle: Capture-level signing is the gold standard because it establishes chain of custody from the moment of capture — before any human intervention is possible. Software-applied credentials are useful but answerable to a different question: they tell you what happened to a file after it was created. Hardware credentials tell you what the file was at the moment of creation. For forensic verification, journalism authentication, and legal evidentiary contexts, the distinction is decisive. Always verify current model support at verify.contentauthenticity.org before purchase — the conformance status of specific models can change as vulnerabilities are discovered and certificates are revoked, as the Nikon Z6 III case illustrates.
🔍 2A. How to Verify an Asset’s Provenance Before Publishing: Step-by-Step Workflow (2026)
The most common question content teams, journalists, and publishers ask about digital provenance is practical: how do you actually verify an incoming image or video before you publish it? The answer in 2026 is more accessible than most people realize — the primary verification tools are free, browser-based, and require no specialist software installation. What they require is a clear understanding of what a verification result means, what information it exposes, and — critically — what it cannot tell you. A valid Content Credential is not a guarantee of truth. It is a verified chain of custody record that tells you where a file came from and what has happened to it. That distinction determines how you act on the result.
Three verification pathways are available in 2026, each suited to different workflows and technical environments. The first is the browser-based verify tool at verify.contentauthenticity.org — which requires no account, no installation, and no technical knowledge. Drag and drop a file (or paste a URL) and the tool reads the C2PA manifest, validates the cryptographic signature, and presents the provenance information in a human-readable format. All processing happens in-browser — no file is uploaded to a server. The second pathway is the Adobe Photoshop Content Credentials panel — the professional standard for creative teams and photojournalists who are already working inside Photoshop. The panel surfaces the full provenance record of any image opened in the application, including edit history, AI generation flags, and certificate issuer details. The third is Adobe Bridge, which allows batch verification across large asset libraries — enabling an editorial team to check provenance across an entire set of submitted photographs before beginning the selection process, rather than checking files one at a time.
When using the Content Credentials verify tool, the metadata it can surface includes: the capture device (camera make, model, and serial number if disclosed); the cryptographic certificate issuer (identifying whether the signing authority is a recognized manufacturer or organization); the editing history (which tools processed the file and in what sequence); AI generation or AI editing flags (whether any AI tool was used in creation or modification); the timestamp of each signed event; and the geographic location of capture if the creator chose to include it. What it cannot tell you is whether the scene depicted is accurate, whether the context in which an image is being used is honest, or whether the signing organization itself is trustworthy — provenance verifies the chain of custody, not the credibility of the source. See our guide to AI and Misinformation for the human verification layer that must accompany technical provenance checking in any serious editorial workflow.
| Step | Action | Tool | What to Look For | ⚠️ Red Flag |
|---|---|---|---|---|
| 1 | Get the original file — not a screenshot, re-saved copy, or platform download that may have stripped metadata | Any file manager | Original camera output or source file from submitter — not a social media download | If only a screenshot or social download is available, metadata has almost certainly been stripped — provenance cannot be verified from that file |
| 2 | Upload to Content Credentials verifier — drag and drop or paste URL; all processing is in-browser, no server upload | verify.contentauthenticity.org | Validation status: Valid / No C2PA data / Invalid or corrupted. Valid = manifest cryptographically intact. | “Invalid / corrupted” = manifest exists but signature check fails — treat provenance as unconfirmed; do not publish as verified |
| 3 | Check the certificate issuer — who signed the credential? | Content Credentials panel (verifier or Photoshop) | Recognised issuer: Sony, Leica, Canon, Adobe, AP, Reuters, or other known C2PA Trust List member | Self-signed certificate or unknown issuer = unverified origin. A valid signature from an unknown signer proves only that the file hasn’t been tampered with since signing — not that the signer is trustworthy |
| 4 | Check capture device — what hardware created the original? | Content Credentials panel | C2PA-enabled camera listed with make, model, and serial number — confirms hardware-level provenance | Unknown or missing device = software-origin credential only; does not confirm the content was captured on a physical camera |
| 5 | Review the editing history — what tools processed this file, and in what sequence? | Content Credentials panel / Adobe Photoshop | Complete declared tool sequence: camera → Lightroom → Photoshop → export. Photoshop records use of Generative Fill, Generative Expand, and other AI tools within the edit history. | Unexplained gaps in editing history, or a jump directly from camera capture to a published format with no intermediate tools declared, may indicate processing through a non-C2PA-compliant tool |
| 6 | Check for AI generation or AI editing flag — was AI involved in creating or modifying this content? | Content Credentials panel | Clear “AI Generated” or “AI Edited” flag — C2PA 2.4 added a dedicated AI disclosure assertion | Absence of AI flag does not prove no AI was used — it only proves no AI was declared in the manifest. Undisclosed AI involvement requires editorial judgment beyond the technical check. |
| 7 | Cross-reference metadata — do EXIF date, GPS location, and context match what the submitter claims? | Adobe Bridge / Photoshop File Info / ExifTool | EXIF timestamp, GPS coordinates (if present), and camera settings consistent with the claimed context (e.g., lighting conditions match time of day) | Inconsistent metadata — e.g., EXIF shows a date different from the claimed capture date, or GPS location doesn’t match the claimed scene — is a serious flag requiring independent verification |
| 8 | Document the verification result — screenshot or export the provenance panel before publication | Internal records / editorial CMS | Documented verification result, verifier used, date of check, and name of verifying staff member attached to the asset record | No audit trail = no defence in the event of a disputed publication. Under EU AI Act Art. 13 and emerging US disclosure requirements, documented verification records are increasingly a compliance expectation |
The Chain of Custody Principle: Provenance verification is not an expression of distrust toward the content submitter — it is the establishment of a documented chain of custody before publication. The same principle that makes a signed evidence log more valuable than an unsigned one in legal proceedings makes a documented provenance check more valuable than an undocumented editorial judgment. Build verification into your pre-publication workflow as a standard step, not an exception triggered by suspicion. The 30 seconds a provenance check takes is negligible compared to the reputational and legal cost of publishing content that was later identified as fabricated.
1. 🧩 What Is Digital Provenance and Why Does It Matter Now?
Provenance is a word borrowed from the art world. When an auction house sells a painting attributed to Rembrandt, the provenance is the documented history of that painting’s ownership, exhibition, and authentication — the chain of evidence that supports the attribution claim. A painting with strong provenance commands a premium. A painting with gaps in its provenance history raises questions about authenticity. The same principle, applied to digital content, is what the field of digital provenance is building.
In the context of digital media, provenance answers three fundamental questions about any piece of content: Who created it? (the source question), When and where was it created? (the context question), and Has it been modified since creation? (the integrity question). These three questions matter in every context where content is used to inform decisions — journalism, legal proceedings, corporate communications, medical imaging, government records, and the everyday social media posts that shape public opinion.
Why 2026 Is the Critical Year
Digital provenance is not a new concept — photographers have embedded metadata in image files for decades, and forensic authentication has been a specialized discipline for longer. What makes 2026 different is the convergence of two simultaneous developments: the dramatic acceleration of AI-generated synthetic media quality on one side, and the first large-scale deployment of standardized content authentication infrastructure on the other. For the first time, the tools to both create and verify authentic content are reaching mainstream deployment simultaneously — making the choices made by platforms, creators, and regulators in the next 12–18 months critically important for the long-term health of the information ecosystem.
The Stakes in Plain Language: In a world without digital provenance standards, a fabricated video of a political leader saying something they never said is, to most viewers, indistinguishable from a genuine recording. With digital provenance standards in place, that same video — lacking the cryptographic signature of a verified camera or the content credentials of a legitimate news organization — can be immediately flagged as unverified, giving viewers the information they need to apply appropriate skepticism before sharing it.
The Trust Deficit Driving Urgency
The urgency behind digital provenance investment is driven by measurable erosion in public trust in digital media. Research from the Reuters Institute for the Study of Journalism found that trust in online news and social media content has declined every year since 2016 across every major market — a trend that accelerated dramatically following the first wave of accessible AI image generation tools in 2022 and 2023. The paradox of the current moment is that the erosion of trust is affecting genuine content as much as fabricated content: a genuine photograph of a real event is now routinely dismissed as “AI-generated” or “manipulated,” not because there is evidence of manipulation, but because the environment of general distrust has made skepticism the default stance. Digital provenance offers a path out of this paradox — not by asking people to trust content blindly, but by giving them verifiable evidence on which to base their trust decisions.
2. 📋 The C2PA Standard: The Technical Foundation of Digital Trust
The Coalition for Content Provenance and Authenticity — known as C2PA — is the international standards body that has developed the primary technical framework for digital content provenance. Founded in 2021 by Adobe, Microsoft, Intel, the BBC, Sony, and Truepic, C2PA has grown to include over 100 member organizations including camera manufacturers, social media platforms, news organizations, and AI companies. Its technical specification defines exactly how content authenticity information should be embedded in, attached to, and verified for digital media files across the entire content lifecycle.
What the C2PA Standard Actually Defines
The C2PA specification is technically complex, but its core architecture rests on three straightforward concepts that are worth understanding clearly before examining how they work in practice.
The first concept is the Content Credential — a structured data package that travels with a piece of content and contains a record of its provenance information: who created it, what tools were used, when it was created, where the creator was located (if disclosed), and what modifications have been made since creation. Content Credentials can be embedded directly in a file’s metadata, attached as a sidecar file, or stored in a cloud-based registry that can be queried when the file is accessed.
The second concept is cryptographic signing — the mechanism that makes Content Credentials trustworthy rather than just informative. Any actor in the content chain — a camera manufacturer, a news organization, an AI platform, or an individual creator — can cryptographically sign a Content Credential using a digital certificate issued by a trusted certificate authority. This signature mathematically ties the credential to the specific file it describes and to the identity of the signer. If the file is subsequently modified, the signature becomes invalid — flagging the modification automatically to any verification system checking the credential.
The third concept is the Manifest — the structured record of all the Content Credentials that have been added to a piece of content throughout its lifecycle. Every time a file is processed — captured by a camera, edited in software, exported by a platform, published by a news organization — a new signed entry is added to the Manifest. The result is a complete, cryptographically verifiable history of everything that has happened to that file from the moment of creation to the moment of viewing.
| C2PA Component | What It Does | Real-World Analogy |
|---|---|---|
| Content Credential | A structured data package containing provenance information about the content | The label on a prescription bottle — stating what it is, who made it, when, and under what conditions |
| Cryptographic Signature | A mathematical seal that proves the credential was issued by a verified entity and has not been tampered with | A notary’s stamp — it does not just say who signed; it proves the signature is authentic and unaltered |
| Manifest | The complete, ordered record of all Content Credentials added throughout the content lifecycle | A passport with all its stamps — a verifiable record of every country (tool or platform) the content has passed through |
| Certificate Authority | The trusted third party that issues digital certificates to legitimate signers | The government agency that issues official ID documents — the trusted root that makes other verification possible |
| Verification Tool | The software that reads and validates a content’s Manifest and presents the provenance information to the user | A UV light used to check a banknote’s security features — the tool that makes the invisible verification visible |
Who Has Adopted C2PA in 2026?
C2PA adoption has accelerated significantly in 2025 and 2026, moving from an industry pilot project to mainstream deployment across major platforms and hardware manufacturers. Adobe’s entire Creative Cloud suite — Photoshop, Lightroom, Premiere Pro, and Firefly AI — now supports Content Credentials by default, embedding provenance information in files at the point of creation and preserving that information through the editing workflow. Microsoft’s responsible AI framework includes C2PA implementation across its AI image generation tools, including the Bing Image Creator and Designer. Sony has integrated C2PA signing into its professional camera hardware — the Alpha series mirrorless cameras can now cryptographically sign images at the point of capture, providing the strongest possible chain of custody starting at the sensor level.
On the platform side, LinkedIn has implemented Content Credential display in its feed, showing a verified badge and provenance details for images that carry valid C2PA credentials. Google has announced integration of C2PA verification into Google Search image results. YouTube is piloting Content Credential display for AI-generated video content. These platform adoptions are critical — the C2PA standard only delivers its full value when content is verified at the point of consumption, not just at the point of creation.
3. 🤖 AI Watermarking: Marking Content at the Point of Generation
While C2PA focuses on provenance throughout the content lifecycle, AI watermarking addresses a specific and increasingly urgent challenge: how do you mark AI-generated content at the moment it is created, in a way that persists even when the content is downloaded, screenshotted, re-uploaded, or processed through other tools?
Visible vs. Invisible Watermarking
AI watermarking comes in two fundamentally different forms, each with distinct use cases, strengths, and limitations. Visible watermarking adds a human-readable label to AI-generated content — a text overlay, an icon, or a banner — that explicitly identifies the content as AI-generated. This approach is simple, immediately understandable, and requires no specialized tools to detect. Its limitation is equally simple: it is trivially easy to remove by cropping, editing, or screenshotting the image without the watermark region.
Invisible watermarking — sometimes called “imperceptible watermarking” or “steganographic watermarking” — embeds a signal within the content itself that is undetectable to the human eye or ear but detectable by specialized software. The watermark is encoded in subtle patterns of pixel values, audio frequencies, or text token distributions that survive many common processing operations. When the content is later analyzed by a compatible detection tool, the watermark signal can be extracted and decoded to reveal information about the content’s AI origin.
Google’s SynthID: The Leading Invisible Watermarking System
The most widely deployed invisible AI watermarking system in 2026 is SynthID, developed by Google DeepMind. SynthID embeds an imperceptible watermark in images, audio, video, and text generated by Google’s AI systems — including Imagen, Lyria, and Gemini. The watermark is designed to survive common image processing operations: resizing, cropping, color adjustment, JPEG compression, and format conversion. For audio content, the watermark survives re-recording, pitch shifting, and audio compression. For text, SynthID uses a token distribution approach that subtly shifts the probability distribution of word choices in a way that is statistically detectable by the verification system but indistinguishable from normal human writing to a reader.
The important caveat about SynthID — which Google is transparent about — is that it is a proprietary system designed to detect content generated specifically by Google’s AI tools. It cannot detect AI-generated content from other providers, and it does not verify that non-AI-generated content is genuine. It is one component of a larger content authenticity ecosystem, not a universal solution.
Watermarking for Large Language Models: The Text Challenge
Watermarking AI-generated text presents unique challenges compared to images or audio. Text does not have pixel values that can be subtly modified — it consists of discrete characters and words where even small changes are immediately visible to readers. The most promising approaches to LLM text watermarking work at the token selection level — introducing subtle statistical biases in the model’s word choices that are invisible to readers but detectable by a classifier trained to recognize the pattern. Research from leading AI research institutions has demonstrated the viability of this approach, but significant challenges remain around robustness when text is paraphrased or translated, and around the risk of false positives flagging genuine human writing as AI-generated.
Important Limitation: No current AI watermarking system is both unremovable and imperceptible. A watermark robust enough to survive aggressive processing tends to introduce detectable artifacts. A watermark subtle enough to be truly imperceptible tends to be removable by determined actors with the right tools. Watermarking is a valuable layer of the content authenticity system — but it is not a complete solution on its own.
4. 🏛️ Real-World Applications: Who Is Using Digital Provenance Today?
Digital provenance is not a future technology — it is being deployed in production environments across journalism, advertising, healthcare, legal services, and government today. Understanding where it is already working helps clarify both its current value and its trajectory.
Journalism and News Media
News organizations face the dual challenge of authenticating the user-generated content they receive — photographs and videos submitted from conflict zones, disaster areas, and breaking news events — and demonstrating the authenticity of their own original reporting to audiences who have been conditioned to distrust media. The Associated Press, Reuters, and the BBC have all implemented C2PA-based content credentials in their publishing workflows, embedding provenance information in photographs and videos published under their bylines. This allows readers and platform verification systems to confirm that an image labeled as an AP photograph was genuinely processed through AP’s verified signing infrastructure.
For user-generated content verification, organizations like the First Draft Coalition and Bellingcat have developed forensic verification workflows that combine C2PA credential checking with traditional open-source intelligence methods — cross-referencing metadata, geolocation analysis, and shadow direction analysis — to assess the authenticity of content submitted from conflict zones. The result is a more rigorous and documented verification process than was previously possible with subjective human assessment alone.
Advertising and Brand Protection
For brands and advertisers, digital provenance is increasingly relevant as a tool for protecting against AI-generated brand impersonation — fake advertisements, fabricated product endorsements, and synthetic spokesperson videos created without authorization. According to IBM’s research on AI-generated brand threats, incidents of AI-generated brand impersonation increased by over 200% between 2023 and 2025, with financial services and pharmaceutical brands among the most targeted sectors.
Brands are responding by embedding Content Credentials in all official digital assets — establishing a cryptographically verifiable baseline of genuine brand content that allows platforms, partners, and consumers to distinguish authentic brand communications from AI-generated impersonations. This is analogous to the SSL certificate system that allows web browsers to display a padlock icon for verified websites — a familiar, trusted visual indicator that requires cryptographic verification in the background.
Healthcare and Medical Imaging
In medical contexts, the integrity of imaging data is a patient safety issue. A radiological image that has been altered — whether maliciously or accidentally — could lead to an incorrect diagnosis with serious consequences for the patient. Digital provenance frameworks are being implemented in healthcare imaging systems to provide cryptographic verification of image integrity from the point of capture through storage, transmission, and clinical review. When a radiologist opens a scan for review, the provenance system can confirm that the image has not been modified since it left the imaging device — providing a level of integrity assurance that is particularly valuable in telemedicine contexts where images travel across multiple systems and geographic boundaries before reaching the reviewing clinician.
Legal and Evidentiary Contexts
Courts have long grappled with the authentication of digital evidence — the legal standards for establishing that a digital photograph, video, or document is what it purports to be and has not been altered. Digital provenance frameworks provide a technical foundation for evidentiary authentication that goes significantly beyond the traditional approach of relying on witness testimony and chain of custody documentation. A photograph with a valid C2PA credential — signed by a verified camera manufacturer, with an unbroken Manifest recording every subsequent edit — provides a level of cryptographic authentication that is significantly more robust than traditional approaches. Several US federal courts have begun accepting C2PA-credentialed evidence as satisfying authentication requirements under Federal Rule of Evidence 901, establishing important precedents for the legal admissibility of provenance-verified digital content.
🔒 Building an AI governance framework? Browse the AI Buzz Governance & Security Hub — in-depth guides covering OWASP, NIST, ISO 42001, AI risk management, and enterprise AI security frameworks.
5. 📊 The Current Landscape: Platforms, Tools, and Standards in 2026
The digital provenance ecosystem in 2026 consists of a growing but still incomplete infrastructure of hardware manufacturers, software platforms, content creation tools, distribution networks, and verification applications. Understanding the current state of deployment helps organizations and individuals make practical decisions about where provenance verification adds genuine value today.
| Category | Key Players | Implementation Status | Verification Method |
|---|---|---|---|
| Camera Hardware | Sony Alpha, Leica M11-P, Nikon Z9 | C2PA signing at sensor level — strongest chain of custody | Cryptographic hardware signing |
| Creative Software | Adobe Creative Cloud, Canva | Content Credentials embedded at export — editing history recorded | C2PA Manifest with edit history |
| AI Generation Tools | Adobe Firefly, Microsoft Designer, Google Imagen | AI-generated label embedded in Content Credentials at generation | C2PA + Invisible Watermark |
| Social Platforms | LinkedIn, YouTube (pilot), Meta (announced) | Credential display in feed — varying levels of verification depth | C2PA verification at upload |
| News Organizations | AP, Reuters, BBC, New York Times | Editorial Content Credentials on published photography and video | Organizational C2PA signing |
| Verification Tools | Content Credentials Verify, Truepic Lens | Consumer-facing verification — browser extensions and web tools | C2PA Manifest reading |
| Search Engines | Google Search (announced) | Provenance signals integrated into image search results | C2PA verification at index |
6. ⚠️ The Honest Limitations: What Digital Provenance Cannot Do
Any responsible discussion of digital provenance must honestly address its current limitations — because overselling the technology’s capabilities creates a false sense of security that could be more dangerous than no verification system at all. Digital provenance is a powerful and important tool, but it is not a complete solution to the problem of online misinformation.
Provenance Does Not Prove Truth
The most fundamental limitation to understand is that digital provenance verifies the origin and integrity of content — not its truth. A photograph with a perfect, unbroken C2PA credential chain, signed by a verified camera at the point of capture and preserved through every subsequent edit, can still depict a staged scene, a misleading context, or a manipulated situation that the camera recorded accurately. The camera faithfully recorded what was in front of it — but what was in front of it was arranged to deceive. Provenance verification tells you the photograph is genuine; it cannot tell you that the scene it depicts is what it appears to be.
The “Provenance Gap” Problem
A significant portion of digital content — particularly content captured on older devices, processed through tools that do not support C2PA, or shared through platforms that strip metadata — will not carry Content Credentials. The absence of a Content Credential does not mean content is fake. It simply means it cannot be verified through the provenance system. In a world where provenance-credentialed content is the exception rather than the rule, the presence of credentials provides positive evidence of authenticity, but their absence provides no evidence either way. As adoption grows, this asymmetry will diminish — but it will remain a significant limitation for years.
The Determined Adversary Problem
Digital provenance systems are effective against casual and automated content manipulation — the kind of deepfake factories producing synthetic content at scale for social media distribution. They are less effective against a determined, sophisticated adversary with significant resources and technical expertise. A nation-state intelligence agency or a well-resourced criminal organization could potentially compromise certificate authorities, create fraudulent signing infrastructure, or exploit implementation vulnerabilities in ways that a casual content manipulator cannot. This does not undermine the value of provenance systems — it simply means they should be understood as raising the cost and difficulty of convincing forgery, not eliminating it entirely.
The Metadata Stripping Problem
Many social media platforms automatically strip metadata — including embedded Content Credentials — from images and videos uploaded to their services. This is done for file size optimization and privacy reasons, but it has the side effect of destroying provenance information in the process. Until all major platforms implement the C2PA standard and preserve credentials through their processing pipelines, a significant portion of content will lose its provenance information the moment it is uploaded to the most widely used distribution channels. This is why the platform adoption decisions of Meta, TikTok, and Twitter/X — which collectively distribute the majority of viral social media content — are critical for the long-term effectiveness of the C2PA ecosystem.
7. 🛠️ Practical Steps: How to Use Digital Provenance Tools Today
Despite the limitations discussed above, there are concrete, practical steps that creators, journalists, businesses, and everyday users can take right now to participate in a more trustworthy digital information ecosystem.
For Content Creators and Photographers
- Enable Content Credentials in Adobe tools: In Photoshop, Lightroom, and Premiere Pro, enable “Content Credentials” in the export settings. Your finished files will carry a verifiable record of your creative work
- Use C2PA-compatible cameras: If you shoot professionally, consider hardware that supports in-camera signing — Sony Alpha series and Leica M11-P are current leaders
- Register your signing identity: Adobe’s Content Authenticity Initiative offers a free tool to attach your verified identity to your Content Credentials, linking your creative output to your professional profile
- Label AI-assisted work explicitly: If your workflow involves AI generation or AI-assisted editing, use the AI-generated label in your Content Credentials to maintain transparency with your audience
For Journalists and News Organizations
- Verify credentials before publishing: Use the free Content Credentials Verify tool to check the provenance of any image or video before publication
- Implement organizational signing: Establish a C2PA signing workflow for your organization’s published content — this allows readers and platforms to verify your content as genuinely from your newsroom
- Document verification workflows: Maintain written records of your content verification process — in legal and regulatory contexts, a documented process is as important as the technical verification itself
- Train staff on provenance tools: Ensure every journalist on your team understands how to check Content Credentials and what the results mean — and what they do not mean
For Business Leaders and Organizations
- Audit your AI content disclosure practices: Review whether AI-generated content in your marketing, communications, and customer-facing materials is appropriately labeled — the EU AI Act and emerging US state regulations increasingly require this
- Protect your brand with Content Credentials: Embed Content Credentials in official digital assets to establish a verifiable baseline that distinguishes genuine brand content from AI-generated impersonations
- Assess deepfake risk: Consider whether your organization — particularly its executives and brand spokespeople — faces meaningful deepfake impersonation risk, and develop a response protocol before an incident occurs
- Review vendor AI disclosure practices: Include AI content labeling requirements in your vendor contracts — if a marketing agency or content supplier is using AI generation tools, you need to know what they are disclosing and to whom
For Everyday Users
- Install a Content Credentials browser extension: Adobe’s free browser extension displays provenance information for images on web pages, showing you at a glance whether an image carries verified credentials
- Check before sharing: Before sharing an image or video that seems surprising, alarming, or emotionally provocative, take 30 seconds to check its provenance using the Content Credentials Verify tool
- Understand what “no credentials” means: Absence of Content Credentials does not mean content is fake — most genuine content does not yet carry credentials. Use absence as a prompt for additional scrutiny, not as proof of inauthenticity
- Read the label, not just the badge: A Content Credential badge means the content has provenance information attached — read what that information says before concluding the content is trustworthy
8. 🔮 The Road Ahead: Digital Provenance in 2027 and Beyond
The digital provenance ecosystem is at an early but rapidly advancing stage of development. Several developments in the next 12–24 months will determine how effective these systems become at scale.
Regulatory Mandates Accelerating Adoption
The EU AI Act, which entered enforcement in 2026, includes explicit requirements for AI-generated content labeling — mandating that content generated by AI systems be clearly identified as such when it could reasonably be mistaken for authentic human-created content. Similar legislation is advancing in multiple US states, with California’s AB 2355 requiring disclosure of AI-generated political advertising content already in effect. As regulatory requirements for AI content labeling expand, the business case for implementing C2PA and watermarking systems strengthens — compliance becomes an additional driver alongside the reputational and trust benefits.
Hardware Proliferation: Smartphones as Provenance Anchors
The most significant near-term opportunity for digital provenance at consumer scale is smartphone integration. Currently, C2PA hardware signing is available only in professional camera equipment. If Apple and Google implement C2PA signing in iPhone and Android camera hardware — an active area of industry discussion — every photograph taken on a smartphone could carry a hardware-verified provenance credential from the point of capture. Given that smartphones account for the overwhelming majority of photographic content shared online, this single development would transform the practical reach of digital provenance more than any other single change.
AI Detection as a Complementary Layer
Alongside provenance-based verification, AI-based detection tools — systems trained to identify statistical patterns characteristic of AI-generated content — are improving rapidly. While AI detection tools are not reliable enough to serve as primary authentication methods on their own, they can serve as a useful complementary signal alongside provenance verification. The combination of “this content carries no provenance credentials” AND “this content scores 87% probability of AI generation on our detection model” is a meaningfully stronger signal than either data point alone. You can explore the current state and limitations of these detection approaches in our guide to AI watermarking versus metadata versus fingerprinting.
🏢 3A. Content Authenticity Vendors: Adversarial Robustness Comparison (2026)
For procurement decision-makers and enterprise content teams evaluating content authenticity solutions, the most important question is not which vendor is C2PA-compliant — most major vendors are, at least nominally — but which implementation is most resistant to adversarial attack. Adversarial robustness in this context means how well a vendor’s implementation resists three specific attack vectors: stripping (removing credentials by passing content through a non-compliant tool or platform), spoofing (creating fraudulent credentials that appear valid but were not issued by a legitimate certificate authority), and manipulation (altering content in ways that do not trigger the signature invalidation check). No current vendor achieves full adversarial robustness across all three vectors — the honest answer from every serious vendor in 2026 is that their implementation significantly raises the cost and difficulty of forgery, but does not make it impossible against a sufficiently resourced adversary.
The 2026 C2PA ecosystem has reached a meaningful scale: the Content Authenticity Initiative reported more than 6,000 members in January 2026, C2PA 2.4 (the current specification, published April 2026) added a dedicated AI disclosure assertion and receipt recording capability, and the C2PA Conformance Programme has established a public registry of products that have passed formal compliance testing. A critical nuance for procurement teams: not every product marketed as “C2PA-capable” has passed Conformance Programme testing — the programme’s conforming products list is the authoritative reference, and the gap between “capable” and “conforming” is meaningful for adversarial robustness assessment. An important 2026 research finding also deserves attention: a peer-reviewed study demonstrated an “Integrity Clash” vulnerability in which a digital asset can simultaneously carry a cryptographically valid C2PA manifest asserting human authorship and a SynthID watermark identifying it as AI-generated, with both signals passing their respective verification checks independently. This desynchronization between provenance and watermarking layers — because the two systems are technically independent and neither conditions on the other — is a structural limitation that no single vendor has fully resolved. See the Content Authenticity Initiative for the current conforming products list and governance standards.
| Vendor / Solution | C2PA Compliant | Adversarial Robustness Profile | Stripping Resistance | AI Detection Layer | Best For |
|---|---|---|---|---|---|
| Truepic | ✅ Yes — founding C2PA member. Truepic Lens mobile app and Vision API achieve C2PA Conformance Programme listing. | Highest hardware-backed robustness available for mobile capture. Truepic Lens captures images through a controlled pipeline that signs content at capture using hardware-attested keys — bypassing the camera roll entirely to prevent post-capture manipulation before signing. | Strong for capture-time content (cannot strip hardware-backed credentials without breaking the cryptographic chain). Moderate for content that passes through downstream platforms that strip metadata. | C2PA manifest-based provenance — does not include proprietary invisible watermarking. Relies on C2PA credential presence for detection. | Insurance claims, legal evidence capture, financial services document verification, journalism field capture requiring court-admissible provenance |
| Adobe Content Credentials | ✅ Yes — Adobe is C2PA founding member and primary specification author. Adobe tools use C2PA Interim Trust List certificates. Note: as of mid-2026, no Adobe desktop application has yet achieved formal C2PA Conformance Programme listing. | Strong for software-layer provenance. Adobe’s implementation is the most comprehensively deployed in creative workflows — Photoshop, Lightroom, Premiere Pro, Firefly, and Illustrator all read, write, and preserve credentials. The editing history record is detailed enough to surface AI tool use (Generative Fill, Generative Expand) within the credential chain. | Moderate. Adobe credentials embed in file metadata — susceptible to stripping when files pass through platforms that do not preserve C2PA manifests. Cloud-stored credentials (hosted manifest) provide a fallback when embedded credentials are stripped. | Integrates with Firefly AI generation disclosure. C2PA AI-generated flag embedded automatically for Firefly outputs. Does not detect AI content from other generators. | Creative agencies, photo journalism workflows, brand asset authentication, editorial teams already inside Adobe Creative Cloud ecosystem |
| CAI verify.contentauthenticity.org | ✅ Yes — the official public verification reference tool for the C2PA ecosystem, maintained by the Content Authenticity Initiative (Adobe-led). Free, open-source, browser-based. | Verification tool, not a signing solution. Reads and validates C2PA manifests from any conforming signer — camera, creative software, AI platform, or news organization. Presents provenance data in human-readable format. Does not add credentials to content. | Detects stripped credentials (shows “No C2PA data” result) but cannot recover stripped credentials. Invalid/corrupted result flags tampered manifests. All processing in-browser — no server upload. | Does not detect SynthID or other invisible watermarks — a separate check at SynthID Detector or OpenAI Verify is required for watermark detection. | Universal pre-publication verification for journalists, content teams, and any organization needing a free, zero-install provenance check |
| Microsoft (Bing / Designer / Azure) | ✅ Yes — C2PA founding member. Bing Image Creator and Microsoft Designer automatically tag AI-generated images with C2PA credentials. Edge browser surfaces provenance data in image search. | Strong for AI generation disclosure within the Microsoft ecosystem. Credential application is automatic for all Bing Image Creator and Designer outputs — no user action required. Azure AI Content Safety API provides content moderation and provenance signal integration for enterprise deployments. | Moderate — credentials embedded in generated image files. Susceptible to stripping when images are downloaded and re-shared through non-C2PA platforms. No proprietary invisible watermark layer beyond C2PA manifest. | AI-generated flag embedded via C2PA for Bing/Designer outputs. Azure Content Safety provides AI content moderation signals as a complementary layer for enterprise applications. | Enterprise organizations within Microsoft 365 and Azure ecosystems; organizations requiring AI content disclosure compliance for outputs from Microsoft AI generation tools |
| Google SynthID / DeepMind | ✅ Partial — Google is expanding C2PA credential support across Gemini, Search, and Chrome. Pixel 10 achieves C2PA Conformance Programme Assurance Level 2. SynthID is a separate, proprietary watermarking layer that operates independently of C2PA. | SynthID represents the strongest invisible watermarking robustness in the 2026 ecosystem for Google-generated content. The watermark is designed to survive resizing, cropping, color adjustment, JPEG compression, re-recording (audio), and format conversion. However, 2026 research demonstrated the Integrity Clash vulnerability — a C2PA manifest can assert human authorship while SynthID simultaneously detects AI generation, with both signals passing independently. | High for pixel-level watermark survival through common processing. Low for metadata-stripping resistance (SynthID survives metadata stripping because it is embedded in the content pixels, not the file metadata — this is its primary adversarial robustness advantage over C2PA alone). | Best AI detection layer available for Google-generated content specifically. Cannot detect AI content from non-Google generators. SynthID has expanded to partner ecosystems including OpenAI and ElevenLabs as of May 2026. | Organizations verifying Google AI-generated content; Pixel 10 users wanting hardware-level capture provenance; enterprises requiring pixel-persistent watermarks that survive metadata stripping |
The 2026 Layered Defence Principle: No single content authenticity vendor is fully adversarially robust in 2026. The strongest current defence architecture combines three layers: hardware credentials (C2PA signing at capture by a Conformance Programme-listed camera or device), software credentials (C2PA manifest updated through the editing workflow by tools like Adobe Creative Cloud), and invisible watermarking (pixel-level signals like SynthID that survive metadata stripping). Each layer closes a gap the others leave open. Hardware credentials establish the capture origin. Software credentials document the editing chain. Invisible watermarks survive the platform stripping that destroys metadata-based credentials. Organisations relying on any single layer are accepting meaningful adversarial robustness gaps. For the governance framework that should accompany any content authenticity deployment decision, see our guide to AI Governance 101 and our guide to LLM Red Teaming for Beginners for the adversarial testing approach that should precede any production deployment.
🏁 Conclusion: Provenance Is the Infrastructure of Truth
Digital provenance is not a technology story. It is a trust story. The technical standards, cryptographic systems, and platform implementations described in this guide are not ends in themselves — they are infrastructure for a more trustworthy information ecosystem, in the same way that roads are infrastructure for commerce and electrical grids are infrastructure for modern life. The value of the infrastructure is not in the infrastructure itself, but in what it enables: in this case, the ability of individuals, organizations, and institutions to make informed judgments about the content they encounter, share, and act upon.
The challenge ahead is not primarily technical — the technical standards exist and are working. The challenge is adoption, education, and cultural change. Every camera manufacturer that implements C2PA signing, every platform that preserves and displays Content Credentials, every journalist who checks provenance before publishing, and every user who pauses to verify before sharing is contributing to the infrastructure of truth in the digital age. The alternative — continuing to navigate an information environment where nothing can be trusted because nothing can be verified — is not a stable equilibrium. Digital provenance is the path toward something better. The work of building it is already underway. The question for every organization and individual reading this is whether they will be part of building it or waiting for others to do so. To understand how AI-generated misinformation connects to the broader challenges of information warfare, our guide to AI in geopolitics and information warfare provides the essential strategic context.
For the newsroom workflows where digital provenance and content verification matter most, our guide to AI in Media and Journalism covers how reporters and editors are integrating source verification, fact-checking tools, and content authentication into their daily workflows in 2026.
📌 Key Takeaways
| Takeaway | |
|---|---|
| ✅ | Digital provenance answers three questions about any piece of content: who created it, when and where, and whether it has been modified since creation. |
| ✅ | The C2PA standard — developed by Adobe, Microsoft, the BBC, and over 100 partners — is the primary technical framework for content provenance, using Content Credentials and cryptographic signing. C2PA 2.4 (April 2026) added a dedicated AI disclosure assertion. |
| ✅ | AI watermarking — including Google DeepMind’s SynthID — embeds imperceptible signals in AI-generated content that persist through common processing operations and can be detected by compatible tools. |
| ✅ | Sony, Leica, and Nikon have implemented C2PA hardware signing in professional cameras — providing the strongest possible provenance chain starting at the point of image capture. |
| ✅ | Digital provenance verifies origin and integrity — not truth. A provenance-verified photograph can still depict a staged or misleading scene. |
| ✅ | The absence of Content Credentials does not prove content is fake — most genuine content does not yet carry credentials. Use absence as a prompt for scrutiny, not as proof of inauthenticity. |
| ✅ | The EU AI Act mandates labeling of AI-generated content that could be mistaken for authentic human-created content — making C2PA implementation a compliance requirement for many organizations in 2026. |
| ✅ | The Google Pixel 10 is the first mainstream consumer smartphone to ship with native C2PA Content Credentials, achieving C2PA Conformance Programme Assurance Level 2 — signing every photo by default using hardware-backed keys in the Titan M2 chip. |
| ✅ | C2PA-enabled cameras (Sony Alpha series, Leica M11-P/M11-D/SL3-S, Canon EOS R1/R5 Mark II) embed cryptographically signed provenance at the moment of capture — the strongest available form of content authentication in 2026. Always verify model conformance status at verify.contentauthenticity.org before purchase. |
| ✅ | Before publishing any third-party asset, verify provenance at verify.contentauthenticity.org — it shows editing history, AI generation flags, capture device, and certificate issuer in seconds, with no account or software installation required. |
| ✅ | No single content authenticity vendor is fully adversarially robust in 2026 — layering hardware credentials, software C2PA signing, and invisible AI watermarking (such as SynthID) provides the strongest current defence against spoofing, stripping, and manipulation attacks. |
❓ Frequently Asked Questions About Digital Provenance
What is digital provenance and why does it matter in 2026?
Digital provenance is the verified record of where content came from, who created it, and how it was edited. In 2026, with AI-generated content indistinguishable to the human eye, provenance verification is the primary defence against misinformation and fake media. See our guide to AI and Misinformation for the full detection framework.
What is C2PA and how does it work?
C2PA (Coalition for Content Provenance and Authenticity) is the open technical standard for embedding cryptographically signed metadata into digital content. Supported by Adobe, Microsoft, Sony, and over 6,000 members as of January 2026, it creates a tamper-evident chain of custody from capture through editing to publication. C2PA 2.4 (April 2026) is the current specification.
How do I verify if an image was AI-generated or edited?
Upload it to verify.contentauthenticity.org. The tool shows Content Credentials if present — including AI generation flags, editing history, and capture device. For Photoshop users, the Content Credentials panel provides the same verification inside the application. For Google-generated images, also check the SynthID Detector portal separately, as C2PA and SynthID are independent systems.
Which cameras support C2PA content credentials in 2026?
Sony (Alpha 1, 9 III, 7 IV, 7S III, and more via firmware), Leica (M11-P, M11-D, SL3-S, Q3 family), Canon (EOS R1, R5 Mark II), and Nikon (Z9, Z8, Zf via firmware — note: Z6 III certificates were revoked after a security vulnerability). Google Pixel 10 is the first consumer smartphone with native C2PA at Conformance Level 2. Always verify current model support at verify.contentauthenticity.org before purchase.
What is the difference between AI watermarking and C2PA provenance?
C2PA embeds a signed certificate in the file’s metadata — verifiable but strippable if metadata is removed when content passes through non-compliant platforms. AI watermarking (like Google SynthID) embeds invisible signals in the content pixels themselves — harder to strip but requires the vendor’s detector to verify, and only works for that vendor’s AI-generated content. See our full comparison in AI Watermarking vs. Metadata vs. Fingerprinting.
🔗 Related Articles
📧 Get the AI Buzz Weekly Digest
Weekly AI insights, tools, and strategies — delivered every Monday. Free.
Leave a Reply