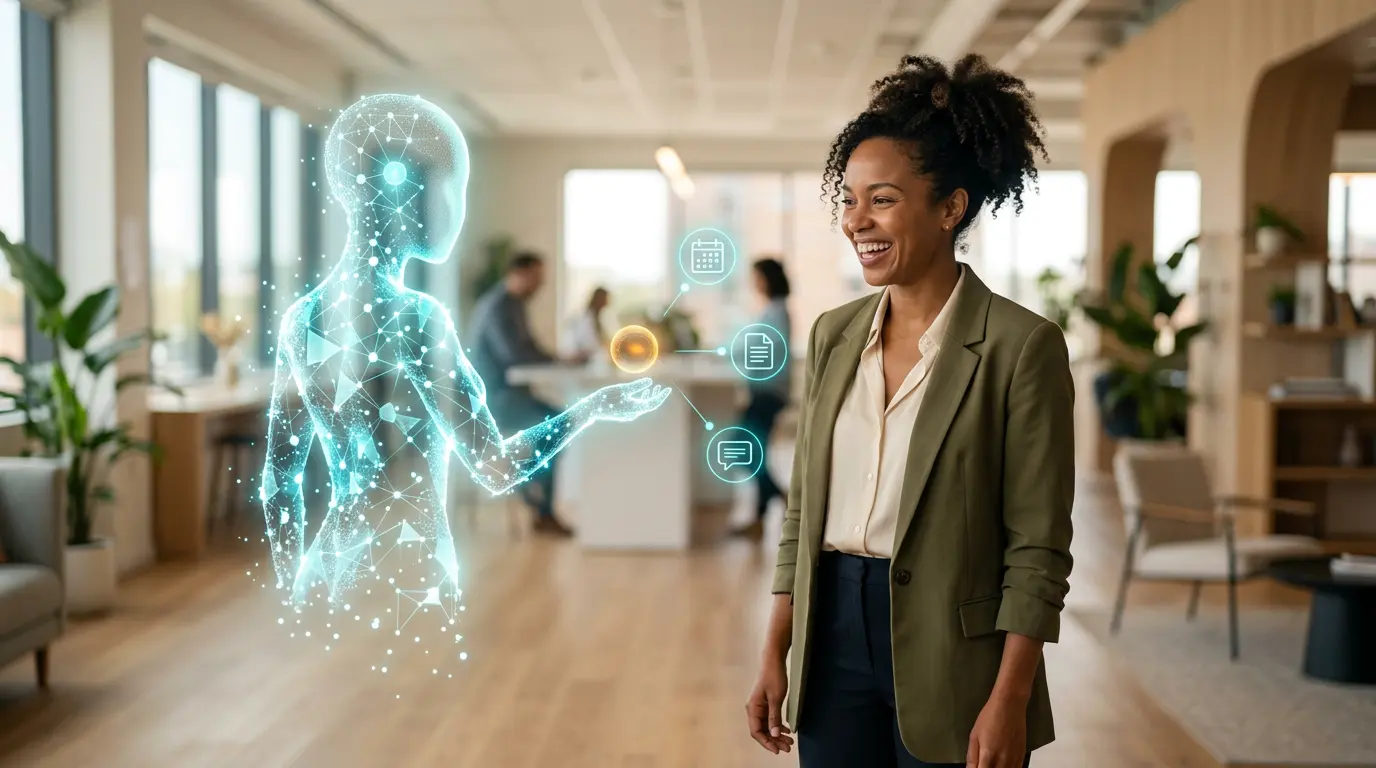
🤖 AI agents are the biggest shift in technology since the smartphone — and most people still do not know what they actually are. This guide explains exactly what an AI agent is, how it works, how it differs from a chatbot and a copilot, and what it means for your job, your business, and your daily life in 2026.
Last Updated: September 16, 2026
Something extraordinary is happening in the world of technology right now — and it is moving faster than most people realize. For the past few years, the most visible face of Artificial Intelligence has been the chatbot. You type a question. The AI types an answer. The interaction is helpful, occasionally impressive, and fundamentally passive. The AI waits for you. You drive the conversation. The machine responds. That model is being replaced — rapidly and comprehensively — by something fundamentally different. AI agents do not wait to be asked. They perceive their environment, make decisions, take actions, and pursue goals — autonomously, continuously, and across multiple systems simultaneously. An AI agent does not answer your question about scheduling a meeting. It checks your calendar, finds a suitable time, sends the invitations, books the conference room, and updates the project management tool — all without you lifting a finger after giving the initial instruction. Gartner expects 40% of enterprise applications to ship with task-specific AI agents by the end of 2026, up from less than 5% in 2025. The global AI agent market is estimated at $11–12 billion in 2026, growing at a 44% CAGR.
In 2026, AI agents are no longer a research concept or a science fiction premise. They are being deployed by businesses of every size, across every industry, to perform real work with real consequences. According to PwC, 79% of companies report that AI agents are already being adopted within their organisations. Understanding what they are, how they work, and — critically — how to use them safely is one of the most important skills any professional can develop right now. This guide gives you everything you need to start that journey, in plain English, with no technical background required.
This article covers four categories of knowledge. First, exactly what an AI agent is and how it differs from chatbots and the often-overlooked copilot category. Second, how agents actually work under the hood. Third, a practical decision framework for choosing between chatbots, copilots, and agents for your specific use case. And fourth, the security, governance, and risk controls that separate responsible agent deployments from dangerous ones.
📖 New to AI terminology? Visit the AI Buzz AI Glossary — 95+ essential AI terms explained in plain English, each linking to a full in-depth guide.
🤖 1. What Is an AI Agent? (The Plain English Definition)
An AI agent is a software system that can perceive its environment, make decisions, and take actions to achieve a defined goal — without requiring a human to approve every step along the way.
The word “agent” comes from the Latin agere — meaning “to do” or “to act.” That etymology is the key to understanding what makes an agent different from every other piece of software you have used before. Traditional software — including traditional chatbots — does things when you tell it to. An AI agent does things because it has a goal and the autonomy to pursue it.
Plain English Definition: An AI agent is like giving a highly capable assistant a task and the keys to your digital office — and trusting them to complete the work without checking in after every single step. You define the goal. The agent figures out how to achieve it.
According to IBM Research’s definition of AI agents, an agent is distinguished from a standard AI model by four core properties: it perceives inputs from its environment, it reasons about what actions to take, it executes those actions using available tools, and it learns from the outcomes to improve future performance. These four properties — perception, reasoning, action, and learning — are what separate a true AI agent from a chatbot that simply generates text in response to prompts.
💬 2. AI Agent vs. Chatbot: What Is the Actual Difference?
The most common point of confusion for beginners is the difference between an AI agent and the AI chatbots most people are already familiar with — tools like ChatGPT, Claude, or Gemini. The distinction is more fundamental than it might initially appear, and understanding it is essential for grasping why agents represent such a significant leap forward.
The Chatbot Model
A chatbot operates in a simple loop: you provide an input, the model generates an output, and the interaction ends. The chatbot has no memory of previous conversations unless you explicitly provide that context. It cannot take actions in the world — it can only produce text. It cannot check your email, update your CRM, book a flight, or send a message on your behalf. It is, fundamentally, a very sophisticated text generator that responds to prompts.
The Agent Model
An AI agent operates in a continuous loop of perception, reasoning, action, and observation. It can use tools — web browsers, email clients, databases, APIs, calendars, code interpreters — to take real actions in digital systems. It maintains memory across sessions, allowing it to build on previous work. It can break a complex goal down into sub-tasks, execute those sub-tasks in sequence, observe the results, and adjust its approach based on what it discovers. And — crucially — it can do all of this without requiring human approval at every step.
| Feature | AI Chatbot | AI Agent |
|---|---|---|
| How it works | Responds to a single prompt and stops. | Pursues a goal across multiple steps autonomously. |
| Tool access | Generates text only. | Uses real tools — email, calendar, browser, APIs. |
| Memory | No memory between sessions. | Persistent memory across sessions and tasks. |
| Human involvement | Human drives every interaction. | Agent drives the task — human supervises. |
| Real-world actions | Cannot take actions outside the chat window. | Can send emails, update databases, book meetings. |
| Best analogy | A knowledgeable colleague you ask questions. | A capable employee you assign projects. |
🧭 3. The Third Category Everyone Forgets: What Is a Copilot?
Most explanations of AI systems present a binary choice between chatbots and agents. In 2026, there is an important middle category that millions of professionals use every day without realising it has a specific name: the copilot. According to IDC, AI copilots will be embedded in 80% of enterprise workplace applications by the end of 2026.
A copilot is an AI system embedded within a human workflow — augmenting the human’s capabilities by providing suggestions, drafts, analyses, and recommendations in real time as the human works, while leaving all final decisions and actions to the human. Like the copilot in an aircraft cockpit, this category of AI is in the seat beside you — capable, informed, and actively contributing — but not flying the plane. The human pilot remains in command.
How a Copilot Differs from Both a Chatbot and an Agent
A chatbot is a separate application you interact with through a dedicated interface — you open the chatbot, ask it something, get a response, and then take that response back into your actual work environment. A copilot is embedded directly within the work environment — it reads what you are working on, understands the context of your current task, and provides assistance without requiring you to switch to a separate application.
Microsoft 365 Copilot is the canonical 2026 example. It is embedded within Word, Excel, PowerPoint, Outlook, and Teams. As you write a Word document, it can suggest the next paragraph, summarize what you have written, or rewrite a section in a different tone — without you leaving the document. As you draft an email in Outlook, it can suggest a complete reply based on the email thread’s context — without you copying the thread into a chatbot. Microsoft now has over 20 million paid Copilot seats across more than 450 million commercial Microsoft 365 paid seats — a distribution channel that standalone AI assistants cannot match.
Copilots share two defining characteristics. First, they are context-aware — they have access to the specific document, data, or workflow the human is currently engaged with. Second, they maintain human primacy — every action that results from a copilot interaction is explicitly initiated by the human. The copilot suggests; the human decides and acts.
Real-World Copilot Examples in 2026
- Microsoft 365 Copilot: Writing assistance, data analysis, meeting summaries, and email drafting embedded across the Office application suite
- GitHub Copilot (basic tier): Code completions and function suggestions embedded within code editors — the developer reviews and accepts or rejects each suggestion
- Google Workspace Gemini: Context-aware writing and analysis assistance embedded within Google Docs, Sheets, Slides, and Gmail
- Salesforce Einstein Copilot: Next-best-action suggestions, email drafts, and customer insight summaries embedded within Salesforce CRM based on live CRM data
- Power BI Copilot: Plain-language questions translated into data visualisations, narrative summaries of dashboard data
⚙️ 4. How Does an AI Agent Actually Work?
Understanding the mechanics of an AI agent does not require a computer science degree. The core architecture can be explained through a simple four-step loop that every agent — regardless of its specific application — follows continuously while working toward its goal.
Step 1: Perceive
The agent takes in information from its environment. This could be a user instruction, an email in an inbox, data from a database, a webpage, a document, or the output of a previous action. The agent’s ability to perceive is determined by the tools and data sources it has been given access to.
Step 2: Reason
The agent uses its underlying AI model — typically a large language model like GPT-5.x or Claude Sonnet 4.5 — to think about the information it has received and decide what to do next. This reasoning step is where the agent breaks down complex goals into manageable sub-tasks, evaluates options, and selects the best next action. This is the stage most associated with Chain-of-Thought reasoning — where the model thinks step by step before acting.
Step 3: Act
The agent executes its chosen action using the tools available to it. It might send an API request, write and run a piece of code, send an email, perform a web search, update a database record, or call another AI agent to handle a sub-task. The breadth of what an agent can do is directly determined by the tools it has been authorized to use.
Step 4: Observe and Adapt
After taking an action, the agent observes the result. Did the action succeed? Did it produce the expected output? Does the next step need to change based on what happened? This observation loop is what allows agents to handle unexpected situations — adapting their approach in real time rather than following a rigid, pre-programmed script.
Real-World Analogy: Think of an AI agent as a new employee on their first week. You give them a project goal. They read the brief (perceive), plan their approach (reason), start making calls and sending emails (act), and adjust their strategy when they discover something unexpected (observe and adapt). You do not stand over their shoulder approving every email — you check in at key milestones and trust them to handle the details.
📊 5. Chatbot vs. Copilot vs. AI Agent: The Complete Comparison
The following comparison covers the three major categories of AI system across ten dimensions that matter most for deployment decisions. Use this as a practical reference when evaluating which type of system your organisation actually needs.
Before reading the table, apply this single classification test to any AI system you encounter:
The Practical Test: Before accepting any AI vendor’s terminology for their product, ask this single question: “Can this system take actions in the world — sending emails, modifying records, calling APIs, executing transactions — without a human approving each individual action?” If yes, you are dealing with an agent or agent-adjacent system. If no, you are dealing with a chatbot or copilot. That single distinction determines more about the appropriate governance, security, and investment decisions than any other technical characteristic.
| Dimension | 💬 Chatbot | 🧭 Copilot | 🤖 AI Agent |
|---|---|---|---|
| Primary Function | Responds to questions with text | Assists human work with context-aware suggestions | Plans and executes multi-step tasks autonomously |
| Autonomy Level | None — purely reactive | Low — suggests but does not act independently | High — acts independently within boundaries |
| Real-World Actions | None — text only | None without human initiation | Yes — sends emails, modifies records, calls APIs |
| Tool Access | None or read-only | Read access to work context | Read and write to multiple systems |
| Oversight Model | Human decides on output use | Human initiates every action | Human sets goals and reviews outcomes |
| Security Risk | Low — cannot act | Low-Moderate — data access risk | High — can take harmful actions if compromised |
| Governance | Standard AI use policy | Data handling + output verification | NHI, audit logging, HITL gates required |
| Complexity | Low — deploy and configure | Moderate — workflow integration | High — architecture, security, monitoring |
| Best Use Cases | FAQ, info access, content drafting | Writing, data analysis, meeting summaries | Process automation, workflow execution |
| Examples | ChatGPT (consumer), FAQ bots | Microsoft 365 Copilot, GitHub Copilot | Salesforce Agentforce, Devin, GitHub Copilot Workspace |
📈 6. The 5 Levels of AI Agent Autonomy
Not all AI agents operate with the same level of independence. Just as self-driving cars are categorized by their level of driving autonomy (from Level 0 — fully manual — to Level 5 — fully autonomous), AI agents exist on a spectrum of autonomy that determines how much human oversight they require.
| Level | Name | What It Does | Example |
|---|---|---|---|
| Level 1 | Assisted | Suggests actions — human approves every one. | Email draft suggestions in Gmail. |
| Level 2 | Supervised | Acts autonomously — human reviews outputs. | AI that drafts and queues social posts for approval. |
| Level 3 | Collaborative | Acts autonomously — escalates edge cases to human. | Customer service agent that handles routine queries independently. |
| Level 4 | Delegated | Fully autonomous — human monitors outcomes. | AI agent managing a full marketing campaign end-to-end. |
| Level 5 | Fully Autonomous | Self-directed — sets and pursues its own goals. | Theoretical — does not yet exist in production. |
For most business deployments in 2026, the appropriate target is Level 2 or Level 3 — where the agent handles routine work autonomously but a human remains in the loop for high-stakes decisions. You can explore the full autonomy framework in our dedicated guide to the 5 Levels of AI Autonomy.
💡 7. What Can AI Agents Actually Do? (Real-World Examples)
The most effective way to understand what AI agents are capable of is through concrete, real-world examples across different business functions. Here are six scenarios where AI agents are already delivering measurable value in 2026:
Sales & CRM
A sales agent monitors the CRM for leads that have gone cold, identifies the optimal re-engagement moment based on activity signals, drafts a personalized outreach email, sends it at the statistically optimal time, logs the interaction in the CRM, and schedules a follow-up task — all without any manual input from the sales rep. Salesforce’s Agentforce platform — which has reached approximately $800 million in annual recurring revenue, up 169% year over year — is the clearest single revenue signal for enterprise agent adoption in 2026.
Customer Support
A support agent reads incoming tickets, retrieves the customer’s account history, identifies the issue category, resolves routine issues autonomously using pre-approved solution templates, escalates complex cases to a human agent with a full context summary already prepared, and updates the ticket system throughout.
Research & Analysis
A research agent receives a brief — “produce a competitive analysis of our top five competitors’ pricing strategies” — then autonomously browses their websites, reads their pricing pages, cross-references recent news, synthesizes the findings, and delivers a structured report — completing in 20 minutes what would take a human analyst half a day.
Finance & Accounting
An accounts payable agent monitors incoming invoices, cross-references them against purchase orders, flags discrepancies for human review, approves matched invoices within pre-authorized limits, initiates payment through the accounting system, and updates the financial records — all without manual data entry.
IT Operations
An IT operations agent monitors system performance metrics continuously, detects anomalies that indicate potential failures, runs pre-approved diagnostic scripts, applies standard remediation procedures for known issue types, and escalates novel issues to a human engineer with a complete diagnostic report already prepared.
Content & Marketing
A content agent monitors industry news feeds, identifies topics trending within the target audience, drafts article outlines aligned with the content strategy, generates first-draft content, checks it against brand guidelines, and queues it for human editorial review — maintaining a consistent content pipeline without requiring daily manual input from the marketing team.
🚀 New to AI? Start with the AI Buzz Beginner’s Guide to AI — 30+ plain-English guides organized into four clear learning paths: fundamentals, tools, prompting, and business adoption.
🎯 8. Which Type of AI Does Your Organisation Actually Need?
The right type of AI system for any given use case is determined by three factors: the nature of the task, the acceptable level of autonomous action, and the organisation’s current AI governance maturity. The decision framework below helps match use cases to the appropriate AI system category.
Choose a Chatbot When:
- The primary value you need is information delivery — answering questions, explaining policies, providing guidance — rather than task execution
- Every output of the AI system needs to be reviewed by a human before it influences any decision or action
- The interaction context is single-session — the user asks, the AI responds, and there is no ongoing workflow the AI needs to maintain
- Your organisation is early in its AI adoption journey and has not yet established governance infrastructure for autonomous action
- Budget is constrained — chatbot deployment is significantly less expensive than agent deployment
Choose a Copilot When:
- Your employees already have established workflows that would benefit from AI assistance embedded within those workflows rather than as a separate interaction
- The primary value you need is augmenting human productivity — making existing work faster and better — rather than replacing human involvement
- You want to maintain complete human control over all actions while benefiting from AI-generated suggestions and drafts
- Your organisation already uses a platform with a strong copilot offering — particularly Microsoft 365, Google Workspace, or Salesforce — making integration natural
- Data privacy requirements make it important that AI operates within your existing data boundary
Choose an AI Agent When:
- The use case involves multi-step workflows with interdependent tasks that are currently handled manually and where automation would deliver significant time savings
- The volume of routine operational tasks exceeds what human teams can handle with acceptable turnaround time, even with copilot assistance
- The tasks involved are sufficiently well-defined and the acceptable action boundaries sufficiently clear that an agent can operate safely within them
- Your organisation has the AI governance maturity — documented policies, human oversight gates, audit logging, and security controls — to deploy autonomous systems responsibly
- You have started with chatbot or copilot deployments and have built sufficient organisational AI experience to manage the additional complexity
The Maturity Sequence: The vast majority of organisations benefit from a sequential AI adoption path — chatbots and copilots first, then supervised agents, then more autonomous agents as operational experience and governance capability mature. Organisations that attempt to deploy fully autonomous agents before mastering chatbot and copilot governance consistently encounter security incidents, operational failures, and organisational resistance that set back their entire AI adoption programme. Walk before you run. Copilot before agent.
| Use Case | Right AI Type | Why | Complexity |
|---|---|---|---|
| Customer FAQ and information delivery | ✅ Chatbot | No action needed — information only | Low |
| Writing assistance in daily workflows | ✅ Copilot | Context-aware help without autonomy | Low-Medium |
| Meeting summaries and document drafting | ✅ Copilot | Augments human — human acts on output | Low-Medium |
| Customer service — routine queries at volume | ✅ Supervised Agent (Level 2–3) | Autonomous resolution + escalation | Medium |
| Sales prospecting and outreach sequences | ✅ Supervised Agent (Level 2–3) | Multi-step workflow + CRM actions | Medium |
| End-to-end process automation | ✅ Agent (Level 4) | High autonomy — requires strong governance | High |
| Complex research and competitive analysis | ✅ Agent (Level 2–3) | Multi-source, multi-step, structured output | Medium |
| IT ops monitoring and remediation | ✅ Agent (Level 3–4) | Autonomous detection + standard fixes | High |
⚠️ 9. What Are the Risks of AI Agents — and How Do You Stay Safe?
The power of AI agents comes with equally significant responsibility. Because agents can take real actions with real consequences — sending emails, processing transactions, modifying data — the risks of poorly governed agent deployments are substantially greater than those of a standard chatbot. According to Gartner’s 2026 AI governance research, ungoverned AI agent deployments are now the fastest-growing source of enterprise AI risk.
Risk 1: Agents Taking Unintended Actions
An agent that misinterprets a goal — or encounters an unexpected situation it was not designed to handle — can take actions that cause real harm. An agent instructed to “clear out old records” that interprets “old” too broadly could delete data that was still needed. This is why clearly defined task boundaries and a robust Human-in-the-Loop framework are essential for every agent deployment.
Risk 2: Prompt Injection Attacks
Because agents read and act on content from external sources — websites, emails, documents — a malicious actor can embed hidden instructions in that content designed to hijack the agent’s behavior. This is called a prompt injection attack, and it is one of the most serious security risks in agentic AI. Always ensure your agents are deployed with proper prompt injection defenses.
Risk 3: Runaway Costs
An agent that enters a loop — repeatedly calling tools or APIs without making progress — can generate enormous compute costs in a very short time. Always set hard limits on token consumption, API calls, and task iterations before deploying any agent in a production environment.
Risk 4: Data Privacy Violations
Agents with broad data access can inadvertently expose sensitive information — either by including it in outputs that reach unauthorized users, or by transmitting it to external systems without proper controls. Ensure every agent deployment includes AI Data Loss Prevention (DLP) controls from day one.
🔐 10. How Security Requirements Change as Autonomy Increases
The security implications of moving from chatbot to copilot to agent are not incremental — they are transformational. Each step up the autonomy spectrum introduces qualitatively new security requirements that the previous level does not face. Organisations that treat agent security as an extension of chatbot security are systematically underprotecting their most powerful — and most dangerous — AI deployments.
Chatbot Security: Content and Data Focus
The primary security risks of chatbot deployments are content risks — the risk that the chatbot generates harmful, biased, or confidential content — and data risks — the risk that sensitive information submitted to the chatbot is retained, used for training, or exposed to unauthorised parties. An AI Acceptable-Use Policy that defines approved chatbot tools and prohibited data types addresses the primary chatbot security risks.
Copilot Security: Data Access and Output Verification
Copilots introduce a new security dimension: they have access to organisational data — documents, emails, spreadsheets, CRM records — that chatbots typically do not. This data access creates exposure risks that require specific controls: ensuring the copilot operates within appropriate data access boundaries, that access to sensitive documents is appropriately scoped, and that outputs generated from sensitive data are reviewed before being shared or acted upon.
Agent Security: Autonomous Action and the Full Attack Surface
AI agents introduce a security attack surface that has no precedent in chatbot or copilot deployments. Because agents can take real-world actions, a successfully compromised agent can cause harm — not just generate problematic outputs. The OWASP Top 10 for Agentic Applications catalogues the most critical agent-specific vulnerabilities. The specific security requirements for agent deployments include: Non-Human Identity management with scoped credentials and automatic revocation; prompt injection detection at all input boundaries; comprehensive audit logging of every action taken; Human-in-the-Loop gates for high-stakes or irreversible actions; and system-level governance controls including maximum step counts, cost caps, and circuit breakers.
| Security Requirement | 💬 Chatbot | 🧭 Copilot | 🤖 AI Agent |
|---|---|---|---|
| AI Acceptable-Use Policy | ✅ Required | ✅ Required | ✅ Required |
| Data Handling Policy | ✅ Required | ✅ Required | ✅ Required |
| Output Verification | ✅ Required | ✅ Required | ✅ Required |
| AI DLP Controls | ⚠️ Recommended | ✅ Required | ✅ Required |
| Prompt Injection Detection | ⚠️ Recommended | ⚠️ Recommended | ✅ Mandatory |
| Non-Human Identity Mgmt | ❌ Not applicable | ⚠️ Recommended | ✅ Mandatory |
| Comprehensive Audit Logging | ⚠️ Recommended | ✅ Required | ✅ Mandatory |
| HITL Gates | ❌ Not applicable | ✅ Built into design | ✅ Mandatory for high-stakes |
| AI Incident Response Playbook | ⚠️ Recommended | ✅ Required | ✅ Mandatory |
❓ 11. The 5 Questions to Ask Before Deploying Your First AI Agent
Whether you are a solo entrepreneur experimenting with your first automation or a department head evaluating an enterprise agent platform, these five questions will protect you from the most common and costly mistakes:
- What is the maximum harm this agent could cause if it behaves unexpectedly? Define the “blast radius” before deployment — not after an incident.
- Which of its actions are reversible — and which are not? Irreversible actions (sending emails, deleting records, processing payments) always require human approval gates.
- How will I know if something goes wrong? Every agent needs real-time monitoring and alerting — not just periodic review.
- Can I stop it instantly if needed? Every agent must have a documented, tested kill switch that a non-technical person can activate in under 60 seconds.
- Is this agent documented? Every agent — its purpose, its permissions, its tool connections, and its oversight framework — must be documented before it goes live.
🏢 12. Three Real-World Scenarios: Matching the Right AI to the Right Problem
Abstract frameworks become clearer through concrete examples. These three scenarios illustrate how the same business function might be served by different categories of AI — and why choosing the right category matters.
Scenario 1: Customer Service
A mid-sized e-commerce company receives 10,000 customer service inquiries per week. Most are routine — order status, return policy, delivery estimates, basic product questions. Approximately 15% involve complex situations requiring judgment, negotiation, or system access to process returns or exchanges.
Right approach — layered: A chatbot handles the 85% of routine inquiries that require only information delivery, providing instant 24/7 responses. For the 15% of complex cases — where action is required — either a supervised agent with human-in-the-loop approval for refunds and exchanges, or escalation to a human agent who uses a copilot to assist. The mistake would be deploying a fully autonomous agent for the entire interaction volume without the human oversight gates needed for complex cases.
Scenario 2: Sales Development
A B2B software company wants to improve its sales development process — identifying prospects, researching them, crafting personalized outreach, and managing follow-up sequences. The current process is handled by a small SDR team whose capacity is the primary bottleneck on pipeline growth.
Right approach — supervised agent: An AI agent that autonomously researches prospects, drafts personalized outreach emails, manages follow-up timing, and updates CRM records — with human review of outreach drafts before sending and human approval of any prospect before they advance in the pipeline. A chatbot cannot do this — it cannot take the initiative to research and outreach autonomously. A copilot can assist an SDR but cannot multiply SDR capacity. A supervised agent with appropriate human oversight gates multiplies SDR capacity while maintaining the human judgment that high-quality prospect qualification requires. For organisations deploying multiple specialised agents working together — one for research, one for outreach, one for qualification — explore our guide to multi-agent systems.
Scenario 3: Internal Knowledge Management
A professional services firm wants to give its consultants instant access to the collective knowledge embedded in thousands of project documents, research reports, and client deliverables stored across its knowledge management system.
Right approach — retrieval-augmented chatbot: A system that answers questions about the firm’s accumulated knowledge by retrieving relevant documents and synthesising accurate answers from them. No autonomous action is needed — consultants ask questions and get answers. A full agent would be over-engineered and unnecessarily risky for this use case. A simple chatbot without retrieval augmentation would be limited to the model’s training data and unable to access the firm’s specific accumulated knowledge. A knowledge-retrieval chatbot is the right tool.
📌 13. Key Takeaways
| Key Takeaway | |
|---|---|
| ✅ | An AI agent is a software system that perceives its environment, makes decisions, and takes actions autonomously to achieve a defined goal. |
| ✅ | AI systems fall into three categories — chatbots (reactive text), copilots (embedded assistance with human primacy), and agents (autonomous multi-step action). |
| ✅ | The global AI agent market is estimated at $11–12 billion in 2026, growing at 44% CAGR, with 51% of enterprises running agents in production. |
| ✅ | The single classification test: “Can it take actions without human approval?” If yes, it is an agent and requires agent-level governance. |
| ✅ | Security requirements escalate at each autonomy level — agents require NHI management, prompt injection detection, audit logging, and HITL gates that chatbots do not. |
| ✅ | Most responsible deployments in 2026 target Level 2 or 3 autonomy — where agents handle routine tasks but humans oversee high-stakes decisions. |
| ✅ | The recommended maturity sequence is chatbot → copilot → supervised agent → autonomous agent. Skipping stages leads to security incidents and organisational resistance. |
| ✅ | Every agent deployment requires a defined blast radius, a kill switch, real-time monitoring, and full documentation before going live. |
🔗 Related Articles
- 📖 Agentic AI Explained: How AI Plans, Acts, and Completes Tasks Without You
- 📖 The AI Agent Economy: How Autonomous AI Is Replacing Software Subscriptions
- 📖 Multi-Agent Systems Explained: How Multiple AI Agents Coordinate
- 📖 Human-in-the-Loop Explained: How to Use AI Safely with Approval Gates
- 📖 The 10 Best AI Agents for Business Automation in 2026
❓ Frequently Asked Questions: What is an AI Agent?
1. What is the difference between an AI agent and an AI copilot?
An AI copilot is embedded within your workflow and provides context-aware suggestions while you remain in control of every action. An AI agent acts autonomously — it takes actions like sending emails, updating databases, and executing multi-step tasks without human approval at each step. Our guide to agentic AI explained covers the architecture in depth.
2. Are AI agents safe to use for business in 2026?
AI agents are safe when deployed with proper governance — including human-in-the-loop gates for high-stakes actions, Non-Human Identity management, audit logging, and kill switches. Without these controls, agents represent significant risk. Our Human-in-the-Loop explained guide covers the oversight framework.
3. What autonomy level should a business start with for AI agents?
Most organisations should start at Level 2 (supervised) or Level 3 (collaborative), where the agent handles routine tasks autonomously but escalates high-stakes decisions to a human. Our guide to the 5 levels of AI autonomy covers each level in detail.
4. Can an AI agent replace a chatbot or copilot entirely?
No. Each serves a different purpose. Chatbots are best for information delivery, copilots for augmenting human work within existing tools, and agents for autonomous multi-step task execution. Most organisations use all three. Our AI agent economy guide explains how these categories coexist.
5. How much does it cost to deploy an AI agent vs a chatbot?
Chatbot deployment is the lowest cost — often a SaaS subscription. Copilots add per-user licensing costs (e.g. $30/user/month for Microsoft 365 Copilot). AI agents require architecture, security controls, monitoring, and governance infrastructure that make them significantly more expensive to deploy responsibly. Our guide to the best AI agents for business compares platform pricing.
📧 Get the AI Buzz Weekly Digest
Weekly AI insights, tools, and strategies — delivered every Monday. Free.
Leave a Reply