⚖️ The EU AI Act is now in active enforcement — and most compliance guides still haven’t caught up. This updated guide explains exactly what is enforceable today, what the Digital Omnibus changed, and what your organization must do before the December 2027 deadline.
Last Updated: October 12, 2026
The EU AI Act’s implementation timeline shifted significantly in mid-2026 — and most EU AI Act compliance guides published before July 2026 are now outdated. The Digital Omnibus on AI (Regulation (EU) 2026/1744), which entered into force on July 27, 2026, deferred the most demanding obligations for standalone high-risk AI systems from August 2, 2026, to December 2, 2027. At the same time, a different and significant set of obligations — Article 50 transparency duties, GPAI enforcement powers, and EU AI Office fines — went live exactly as scheduled on August 2, 2026. Understanding which obligations are active now versus which have been deferred is the most important EU AI Act compliance question of the moment. This guide gives you the accurate, current answer as of October 12, 2026.
If your organization deploys chatbots, AI-generated content tools, or uses generative AI to produce text, images, audio, or video for EU audiences, you have active obligations from August 2, 2026. If your organization uses AI in hiring, credit scoring, biometric identification, critical infrastructure, or law enforcement, you are subject to the Annex III high-risk requirements — but your compliance deadline has moved to December 2, 2027. That is a preparation window. It is not a reason to delay: the classification analysis, AI system inventory, and documentation work must begin now. As the EU AI Office has made clear, the compliance architecture of the Act — risk classification, conformity assessment, human oversight, and data governance — is unchanged. Only the deadline moved. For organizations specifically focused on AI literacy training requirements under Article 4, see our dedicated AI Literacy (EU AI Act Article 4) guide. For GPAI model providers, our EU AI Act GPAI Code of Practice guide covers provider obligations in detail.
This guide covers the complete EU AI Act compliance framework as it stands in October 2026 — the accurate implementation timeline including the Digital Omnibus deferral, the four-tier risk classification system, what is active now under Article 50 and GPAI rules, high-risk AI system obligations and what you must prepare for December 2027, penalties for non-compliance, industry-specific impact, RAG pipeline compliance obligations, and a practical compliance checklist your team can begin using today. It is written for compliance officers, legal teams, CISOs, AI governance leads, and business leaders — not as a beginner introduction, but as a working reference for organizations assessing and managing their EU AI Act exposure in 2026. For foundational governance frameworks, see our guide on building an AI governance framework.
📖 New to AI terminology? Visit the AI Buzz AI Glossary — 100+ essential AI terms explained in plain English, each linking to a full in-depth guide.
📅 1. EU AI Act Timeline: What Has Happened and What Is Coming (Updated 2026)
The EU AI Act (formally Regulation (EU) 2024/1689 of the European Parliament and of the Council on Artificial Intelligence) entered into force on August 1, 2024, and applies in phased stages. The phased approach was designed to give organizations time to assess AI use cases, implement controls, and align governance before full enforcement. The August 2026 milestone brought a significant legislative development — the Digital Omnibus on AI — that has reshaped the compliance calendar in ways most organizations have not yet fully processed.
The Digital Omnibus on AI (Regulation (EU) 2026/1744) was adopted by the European Parliament on June 16, 2026, received final Council approval on June 29, 2026, was signed on July 8, 2026, published in the EU Official Journal on July 24, 2026, and entered into force on July 27, 2026 — six days before the original August 2 high-risk deadline. Its primary effect was to defer the Annex III standalone high-risk obligations from August 2, 2026, to December 2, 2027, and Annex I embedded system obligations from August 2027 to August 2, 2028. These are fixed dates — not conditional on standards being finalized. Organizations should treat December 2, 2027, as a hard compliance deadline for Annex III systems.
What did NOT move is equally important. The Article 50 transparency obligations — chatbot disclosure, AI-generated content labeling, deepfake disclosure, emotion recognition notification — took effect on August 2, 2026, exactly as scheduled. The EU AI Office’s enforcement powers over GPAI providers, including the power to impose Article 101 fines, also became active on August 2, 2026. The prohibited practices regime under Article 5 has been enforceable since February 2, 2025, and remains fully active. Organizations must not interpret the Omnibus deferral as a general pause — for transparency, GPAI, and prohibited practices, enforcement is the present reality, not a future planning date.
The 2026 EU AI Act Reality: The Digital Omnibus deferred the high-risk Annex III deadline to December 2, 2027 — but transparency obligations (Article 50), GPAI enforcement powers, and prohibited practice fines are active now. Organizations that interpret the deferral as a general pause are misreading the law and creating compliance exposure today.
| Date | Milestone | What Became Active | Status |
|---|---|---|---|
| Aug 1, 2024 | Act enters into force | Regulation (EU) 2024/1689 published. 20-day countdown to general provisions. | ✅ Complete |
| Feb 2, 2025 | Prohibited practices + AI literacy active | Article 5 prohibitions enforceable. Article 4 AI literacy obligations begin. Fines up to €35M / 7% turnover for violations. | ✅ Active & Enforced |
| Aug 2, 2025 | GPAI model obligations active | Articles 51–55 apply. GPAI providers must comply with transparency, copyright, and systemic risk rules. GPAI Code of Practice published July 10, 2025 — 26 signatories including Amazon, Anthropic, Google, Microsoft, OpenAI. | ✅ Active & Enforced |
| Jul 27, 2026 | Digital Omnibus on AI enters into force | Regulation (EU) 2026/1744 published. Annex III high-risk deadline deferred to Dec 2, 2027. Annex I embedded systems deferred to Aug 2, 2028. Transparency and GPAI obligations unchanged. | ✅ In Force |
| Aug 2, 2026 | Article 50 transparency + GPAI enforcement NOW ACTIVE | Chatbot disclosure, AI content labeling, deepfake marking, emotion recognition notification. EU AI Office gains fine powers over GPAI providers (Article 101). | 🔴 NOW ACTIVE |
| Dec 2, 2026 | AI content marking grace period ends | Generative AI systems on market before Aug 2, 2026 must complete machine-readable content marking (Article 50(2)). A new prohibition on AI-generated non-consensual intimate imagery also takes effect. | ⚠️ Approaching |
| Dec 2, 2027 | Annex III high-risk AI obligations DEADLINE | Standalone high-risk AI systems (hiring, credit, education, critical infrastructure, law enforcement, biometrics) must fully comply. Risk management, technical documentation, conformity assessment, EU AI database registration all required. | ⏳ Prepare Now |
| Aug 2, 2028 | Annex I embedded AI obligations DEADLINE | High-risk AI embedded in regulated products (medical devices, machinery, vehicles, toys) under EU harmonization legislation must comply. | ⏳ Plan Ahead |
⚡ 2. What Is Active Right Now — EU AI Act in Force (August 2026)
The single most important EU AI Act compliance question for organizations in late 2026 is this: what is actually enforceable right now, and what has been legitimately deferred? The Digital Omnibus has been widely misread — by both internal compliance teams and external advisors — as a general extension of the EU AI Act timeline. It is not. The Omnibus made targeted changes to specific deadlines. A substantial body of EU AI Act obligations took effect exactly as originally scheduled on August 2, 2026, and are fully enforceable today.
August 2, 2026 activated four distinct compliance obligations that apply to most organizations deploying AI for EU audiences. First, Article 50 transparency requirements became fully enforceable: every chatbot or AI conversational interface must disclose its AI nature at the start of every interaction. Every piece of AI-generated content — text, images, audio, video — produced for public communication must carry a machine-readable marker identifying it as synthetically generated. Deepfakes depicting real people must be labeled visibly. Emotion recognition and biometric categorization systems must disclose their nature to subjects. Second, the European Commission confirmed that from August 2, 2026, it began actively enforcing transparency requirements under Article 50, with violations subject to fines of up to €15 million or 3% of global annual turnover. Third, Article 4 AI literacy obligations — which technically began on February 2, 2025 — have been reaffirmed by the Digital Omnibus in amended form: providers and deployers must take proportionate measures to support AI literacy among staff who use AI systems. Fourth, the EU AI Office’s full investigatory and enforcement powers over GPAI model providers activated on August 2, 2026, including the power to impose fines under Article 101.
The Digital Omnibus itself — Regulation (EU) 2026/1744, in force July 27, 2026 — introduced important amendments beyond the deadline deferrals. It added new prohibitions to Article 5, including a ban on AI systems used to generate non-consensual intimate imagery (effective December 2, 2026) and child sexual abuse material (immediate). It tightened Article 4 on AI literacy, recasting it as a proportionate expectation calibrated to the risk and complexity of the AI use case rather than a prescriptive training mandate. It extended the EU AI Office’s oversight to cover GPAI models embedded in large online platforms and search engines. What it did not change: the core risk-classification framework, Article 50 transparency duties, GPAI model obligations, or national enforcement authority powers — all of which remained on their original August 2026 schedule.
The Digital Omnibus is frequently misread as a general extension of the EU AI Act timeline. It is not. It is a targeted deferral of Annex III high-risk system obligations only. Article 50 transparency requirements, GPAI model obligations, and national enforcement powers all applied on schedule from August 2, 2026. Any organisation that paused compliance work in response to the Omnibus has paused the wrong things.
| Provision | Status | Deadline | Key Obligation |
|---|---|---|---|
| Prohibited practices (Article 5) | ✅ Active | Feb 2, 2025 | Social scoring, biometric mass surveillance, subliminal manipulation — all banned |
| GPAI model obligations (Articles 53–55) | ✅ Active | Aug 2, 2025 | Foundation model transparency, copyright policy, GPAI Code of Practice |
| AI literacy (Article 4 — amended) | ✅ Active | Feb 2, 2025 | Proportionate AI literacy measures for deploying organisations — amended by Digital Omnibus |
| Article 50 transparency (chatbot, deepfake, content labeling) | 🔴 Active NOW | Aug 2, 2026 | Disclosure at every AI interaction + machine-readable content marking |
| National enforcement powers | 🔴 Active NOW | Aug 2, 2026 | Full investigatory and fine authority transferred to national market surveillance authorities |
| Machine-readable marking (pre-Aug 2026 systems) | ⚠️ Approaching | Dec 2, 2026 | Narrow grace period only for generative AI systems already on market before Aug 2, 2026 |
| Annex III standalone high-risk systems | 🔲 Planning | Dec 2, 2027 | Deferred by Digital Omnibus — full compliance obligations apply at deadline |
| High-risk AI in regulated products (Annex I) | 🔲 Planning | Aug 2, 2028 | Deferred by Digital Omnibus — medical devices, machinery, vehicles, aviation |
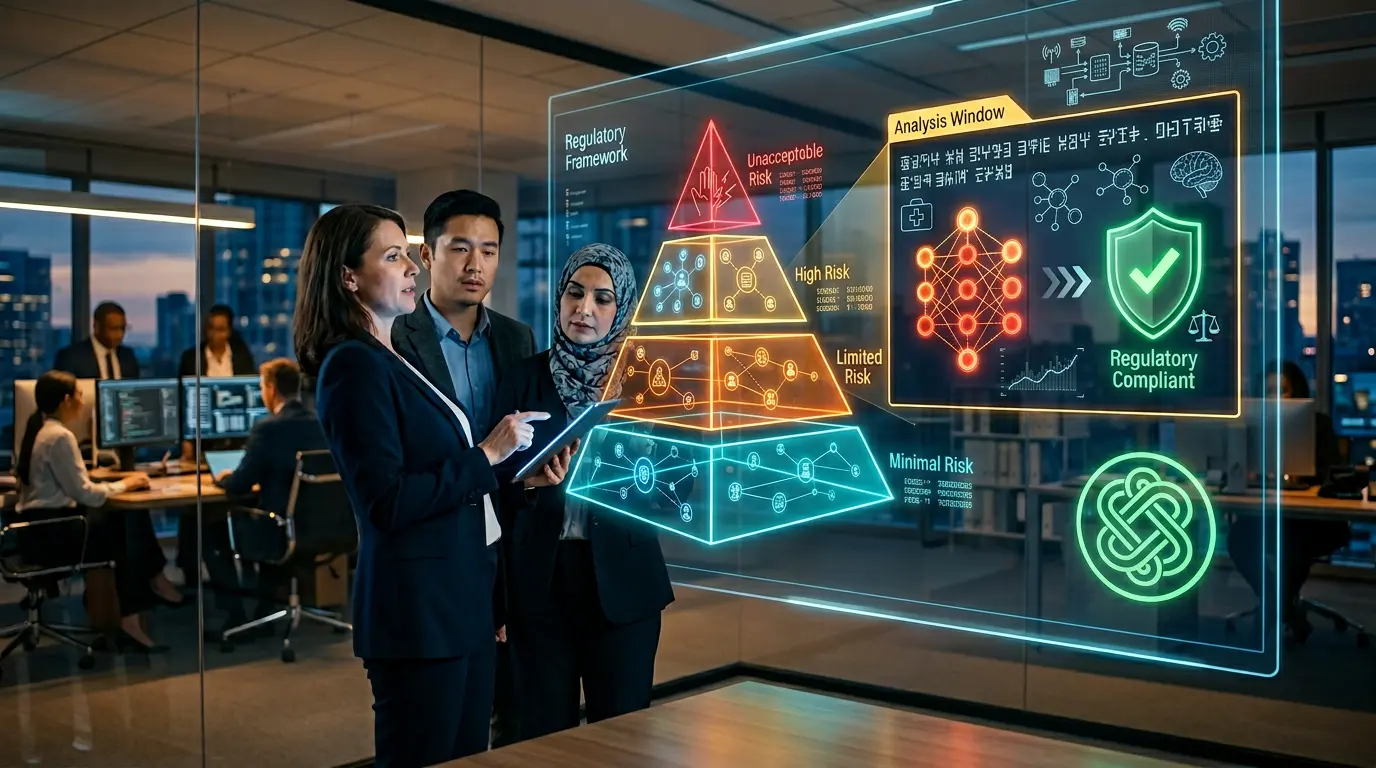
⚠️ 3. EU AI Act Risk Classification: The Four Levels Explained
The EU AI Act applies a risk-based approach — meaning your compliance obligations depend entirely on how your AI system is classified. The four-tier risk framework is unchanged by the Digital Omnibus: what moved was the enforcement date for high-risk systems, not the classification rules themselves. Organizations must complete their risk classification analysis now, using the current Article 6 framework and Annex III categories, regardless of the compliance deadline.
The Commission published draft guidelines on Article 6 classification on May 19, 2026 — a significant tool for organizations assessing whether their systems qualify as high-risk. The most important practical insight from those guidelines: a system that is integrated into an Annex III use case is high-risk by default, even if the AI component appears peripheral. CV screening software embedded in a recruiting workflow is high-risk. An AI tool that generates a score used in a credit decision is high-risk. The question is not whether your tool “looks like” high-risk AI — it is whether it is used in a context covered by Annex III.
One critical compliance error organizations make repeatedly: assuming that because their AI system is purchased from a third-party provider, the provider bears all the compliance burden. The EU AI Act distinguishes clearly between providers (who develop and place AI on the market) and deployers (who use AI systems in a specific operational context). Deployers of high-risk AI systems carry their own independent set of obligations — particularly around human oversight, record keeping, and fundamental rights impact assessment. Using ChatGPT or Claude via API in a high-risk application does not transfer your compliance obligations to Anthropic or OpenAI.
The most common misclassification error: Assuming your AI system is minimal risk because it feels routine. HR AI tools — including CV screening, interview scheduling, and performance management — are explicitly listed as high-risk under Annex III. If you use AI in hiring decisions affecting EU residents, you are almost certainly in scope for December 2027.
| Risk Level | Categories / Examples | Obligation Level | Compliance Date | Status |
|---|---|---|---|---|
| Unacceptable Risk (Prohibited) | Social scoring by governments; subliminal manipulation; real-time biometric ID in public spaces (narrow LE exceptions); exploitation of vulnerable groups; emotion recognition at work/school; untargeted facial image scraping; AI predicting crime by profiling alone; non-consensual intimate imagery AI (Dec 2026) | ❌ Banned — no compliance path. Must cease or not deploy. | Feb 2, 2025 (most); Dec 2, 2026 (NCII ban) | 🔴 Enforced Now |
| High Risk (Annex III — Standalone) | Biometric ID; critical infrastructure; education admissions & assessment; recruitment, CV screening, performance monitoring; credit scoring; insurance risk; law enforcement; border control; justice and democratic processes | ⚠️ Regulated — full compliance obligations. Risk management, documentation, human oversight, conformity assessment, EU AI database registration. | Dec 2, 2027 | ⏳ Prepare Now |
| High Risk (Annex I — Embedded) | AI in medical devices, machinery, vehicles, aviation, toys — where the AI is a safety component of an already-regulated product under EU harmonization legislation | ⚠️ Regulated — same obligations as Annex III; overlap with sector regulation (MDR, Machinery Regulation). | Aug 2, 2028 | ⏳ Plan Ahead |
| Limited Risk (Transparency) | AI chatbots & conversational agents; deepfakes and synthetic media; AI-generated text, images, audio, video for public use; emotion recognition (permitted cases); biometric categorization (permitted cases) | ✅ Disclosure required — inform users they are interacting with AI; label AI-generated content; machine-readable markers on synthetic output. | Aug 2, 2026 (NOW) | 🔴 Active Now |
| Minimal Risk | Spam filters; recommendation engines; AI in non-safety-critical manufacturing; AI video games; most B2B analytics tools not in Annex III contexts | ✅ No mandatory obligations. Voluntary codes of conduct encouraged. | N/A | ✅ No action required |
🔴 4. What Is Active Right Now: Article 50 Transparency Obligations
While the high-risk Annex III obligations do not apply until December 2027, a substantial set of legally binding obligations became enforceable on August 2, 2026. If your organization operates chatbots, AI-generated content tools, or uses AI to produce synthetic media for EU audiences, you are subject to these requirements today. Understanding Article 50 is the most immediate EU AI Act compliance task for most organizations in 2026.
Four specific transparency requirements are now active under Article 50. First, any organization running a chatbot or AI conversational interface must disclose at the start of every interaction — in plain, accessible terms — that the user is communicating with an AI system. This applies to customer service bots, HR recruitment chatbots, and any other automated conversational agent deployed to EU users. Second, providers of generative AI systems that produce synthetic audio, images, video, or text must embed machine-readable markers in those outputs so they can be detected as artificially generated. Systems already on the EU market before August 2, 2026, have until December 2, 2026, to implement this watermarking requirement. Third, organizations publishing deepfakes — AI-generated or AI-manipulated content depicting real people or events — must label that content visibly as AI-generated. Fourth, emotion recognition and biometric categorization systems must disclose their nature to the subjects.
In parallel, the EU AI Office’s power to investigate GPAI model providers and impose fines under Article 101 became active on August 2, 2026. This applies to providers of foundation models such as GPT-5, Claude Opus 4.7, Gemini 3.1 Pro, Llama 4, and similar systems. For deployers — organizations using these models in their products and services — this means the GPAI providers you rely on are now operating under active EU regulatory oversight, which adds a layer of accountability to your AI vendor assessment process.
🔴 5. High-Risk AI System Obligations — What You Must Prepare for December 2027
The deferral to December 2, 2027, does not reduce the compliance burden — it extends the preparation window. The obligations themselves are unchanged. Organizations that begin the compliance program now have time to build the required systems, documentation, and governance structures properly. Organizations that wait until mid-2027 will face a compressed, high-risk sprint. The hard part of EU AI Act compliance is not filling out documentation templates — it is identifying every AI system in your organization, classifying each one against Annex III, and building the ongoing governance infrastructure. None of that work depends on technical standards being finalized. It can and must begin now.
The high-risk obligations cover eight distinct areas under Chapter III of the Act. Each applies to both providers (who develop and place high-risk AI systems on the market) and deployers (who use high-risk AI systems in a specific operational context), though the specific obligations differ. Organizations that substantially modify an existing AI system or adapt it for a high-risk use case become a provider for that deployment and assume full provider-level obligations. See our AI Risk Assessment framework for a structured approach to working through these requirements. The Article 13 transparency obligation — supplying deployers with instructions covering capabilities, limitations, and human oversight requirements — is most effectively satisfied through a structured AI system card documentation required under Article 13, which serves as the primary accountability document for every deployed AI system.
Human oversight is not a checkbox. Article 14 requires technical measures that actively enable humans to understand, override, and halt high-risk AI systems. Logging access without genuine override capability does not satisfy the requirement. The human must be able to disregard or intervene in the system’s output — not merely observe it.
| Obligation (Article) | What It Requires | Who Is Responsible | Evidence Required |
|---|---|---|---|
| Risk Management System (Article 9) | Documented, continuous risk management throughout the AI system’s lifecycle. Identification, analysis, estimation, evaluation, and mitigation of risks — not a one-time assessment. | Provider (primarily); Deployer (operational risks) | Risk management documentation; risk register; mitigation records; periodic review evidence |
| Data and Data Governance (Article 10) | Training, validation, and testing datasets must meet quality criteria: relevant, representative, error-free, and bias-assessed. Data governance and management practices documented. | Provider | Dataset documentation; data quality assessments; bias evaluation reports; data governance policy |
| Technical Documentation (Article 11) | Comprehensive documentation prepared before market placement: system description, design specs, training methodology, performance metrics. Must be kept current. Stored for 10 years. | Provider | Annex IV technical documentation bundle; version-controlled records; changelog evidence |
| Record Keeping / Logging (Article 12) | Automatic logging of events throughout the system’s operation. Audit trail of decisions, inputs, and actions. Logs must enable post-incident reconstruction. | Provider (technical capability); Deployer (operational logs) | Automatic log files; log retention policy; audit trail samples; storage evidence |
| Transparency to Users (Article 13) | Instructions for use in accessible languages. Clear information on capabilities, limitations, and risks. Disclosure that system is high-risk AI. Contact information for provider. | Provider (documentation); Deployer (delivery to end users) | User instructions document; interface disclosures; language coverage evidence |
| Human Oversight (Article 14) | Technical measures enabling humans to understand outputs, disregard or override the system, and halt operation. Named responsible persons. Override mechanism must be genuinely functional. | Provider (technical); Deployer (operational governance) | Override mechanism test records; named oversight persons; training records; governance policy |
| Accuracy, Robustness, Cybersecurity (Article 15) | Appropriate accuracy levels for the use case. Resilience to errors, faults, and inconsistencies. Resistance to adversarial attacks across the full action layer including APIs. Cybersecurity measures proportionate to risk. | Provider (primarily); Deployer (operational configuration) | Performance benchmarks; robustness testing reports; penetration test records; cybersecurity assessment |
| Conformity Assessment + Registration | Before market placement: self-assessment or third-party audit (depending on category). CE marking required after assessment. Declaration of conformity. Registration in EU AI database before deployment. | Provider | Conformity assessment report; CE marking certificate; Declaration of conformity; EU AI database registration confirmation |
🤖 6. General Purpose AI (GPAI) Model Obligations — What Is Active Now
GPAI obligations are not deferred. They became active on August 2, 2025, and since August 2, 2026, the EU AI Office has full enforcement power over GPAI providers including the ability to impose fines. If your organization provides a GPAI model — meaning you develop and distribute a model capable of being used across a wide range of tasks — you have been subject to binding compliance obligations for over a year. August 2026 adds enforcement teeth to those obligations that did not exist before.
The GPAI Code of Practice, published on July 10, 2025, and endorsed by the EU Commission and AI Board, provides a voluntary compliance framework. The Code covers three chapters: Transparency (training data documentation, copyright summaries), Copyright (training data copyright policy, EU copyright law compliance), and Safety and Security (for systemic-risk models only — adversarial testing, incident reporting, cybersecurity). As of the time of this writing, 26 organizations have signed the Code, including Amazon, Anthropic, Google, IBM, Microsoft, OpenAI, Mistral AI, Cohere, and Aleph Alpha. Signatories receive a presumption of conformity — meaning the EU AI Office focuses enforcement activities on monitoring Code adherence for signatories, while non-signatories face more intensive scrutiny and must demonstrate compliance through other means. Learn more in our dedicated GPAI Code of Practice guide.
For organizations that are deployers rather than providers — meaning you use GPAI models like GPT-5, Claude Opus 4.7, or Gemini 3.1 Pro via API to build products or automate workflows — your obligations are different. You are not responsible for the provider’s GPAI compliance. However, if you deploy a GPAI model in a high-risk application context covered by Annex III, you become a high-risk AI system deployer and inherit the deployer-level obligations described in Section 5. You should obtain GPAI compliance documentation from your providers as part of your AI model documentation and vendor management processes.
| GPAI Obligation | All GPAI Models? | Systemic Risk Only? | Active Since |
|---|---|---|---|
| Technical documentation of model capabilities and training | ✅ Yes | No | Aug 2, 2025 |
| Copyright policy for training data | ✅ Yes | No | Aug 2, 2025 |
| Summary of training data (publicly available) | ✅ Yes | No | Aug 2, 2025 |
| Adversarial testing / model evaluation | ⚠️ Systemic risk only | Yes — models trained on 10²⁵ FLOPs or designated by Commission | Aug 2, 2025 |
| Incident reporting to EU AI Office | ⚠️ Systemic risk only | Yes | Aug 2, 2025 |
| EU AI Office fine enforcement power (Article 101) | ✅ Yes — all GPAI providers | No | 🔴 Aug 2, 2026 (NOW ACTIVE) |
🔒 Building an AI governance framework? Browse the AI Buzz Governance & Security Hub — comprehensive in-depth guides covering OWASP, NIST, ISO 42001, AI risk management, and enterprise AI security frameworks.
🏭 7. Industry-Specific Impact — Who Must Act First
The EU AI Act affects different industries in different ways and on different timelines. For some sectors — those deploying transparency-triggering AI tools today — the August 2026 obligations are already live. For others, the December 2027 deadline for Annex III systems is the primary planning horizon. In both cases, the classification analysis is the immediate action: organizations need to know now which category their AI systems fall into, even if the full compliance build is underway for December 2027.
Financial Services and Banking
AI credit scoring, insurance risk assessment, and loan decision tools are explicitly categorized as high-risk under Annex III’s “access to essential services” category. For banks and financial institutions operating in both US and EU markets, the EU AI Act creates compliance overlap with the US Federal SR 26-2 (April 2026), which governs AI/ML model risk in banking. Organizations should integrate both frameworks rather than treating them as separate workstreams. Fraud detection AI falls into a grey zone and must be assessed against the specific Annex III criteria — the determinant is whether the AI output materially influences an essential service decision. See our analysis of AI in Banking and Financial Services for broader context.
Human Resources and Recruitment
This is the highest-risk sector for most enterprises. AI CV screening, interview assessment tools, performance monitoring systems, and workforce management AI that influences employment decisions for EU workers are all explicitly high-risk under Annex III Point 4. The compliance obligation applies to the deployer — meaning the HR team using the tool — not only to the vendor who built it. If you use AI tools in your hiring, performance management, or termination processes for EU employees, begin your Annex III classification assessment immediately. The December 2027 deadline requires a compliance program that takes 12–18 months to build properly. Our AI in Human Resources guide covers the broader transformation context.
Healthcare and MedTech
AI embedded in medical devices regulated under the EU Medical Device Regulation (MDR) falls under Annex I of the EU AI Act and faces the August 2, 2028, deadline. Standalone AI diagnostic tools, AI clinical trial systems, and AI patient triage systems used outside regulated device frameworks must be assessed against Annex III criteria. Healthcare organizations using AI in critical clinical decision support — even tools not classified as medical devices — should conduct a thorough Annex III assessment against the “safety component of critical infrastructure” category.
Education
AI admissions systems, AI-powered assessment and grading tools, and AI monitoring systems used in educational institutions are high-risk under Annex III Point 3. AI tutoring tools and content recommendation engines typically fall in the limited risk or minimal risk categories — but any AI that influences admissions decisions or academic outcomes is in scope for December 2027.
| Industry | AI System Type | Risk Level | Deadline | Immediate Action |
|---|---|---|---|---|
| Finance / Banking | AI credit scoring, loan decisions, insurance underwriting | ⚠️ High Risk (Annex III) | Dec 2, 2027 | Begin classification + risk management now |
| HR / Recruiting | AI CV screening, interview assessment, performance monitoring, termination AI | ⚠️ High Risk (Annex III) | Dec 2, 2027 | Most urgent — highest volume of in-scope deployments |
| Healthcare (standalone) | AI clinical decision support, triage, diagnostics (non-MDR) | ⚠️ Assess against Annex III | Dec 2, 2027 | Classify now; consult legal |
| Healthcare (MedTech) | AI embedded in EU MDR-regulated medical devices | ⚠️ High Risk (Annex I) | Aug 2, 2028 | Coordinate with MDR compliance team |
| Education | AI admissions systems, AI assessment/grading, AI student monitoring | ⚠️ High Risk (Annex III) | Dec 2, 2027 | Audit admissions and assessment AI tools now |
| Law Enforcement | Real-time biometric ID in public spaces (narrow LE exception); predictive policing; evidence evaluation AI | ❌ Prohibited / ⚠️ High Risk | Feb 2025 (prohibited) / Dec 2027 (high risk) | Legal review required immediately |
| Retail | Recommendation engines, dynamic pricing, AI-generated product content, chatbots | 🟡 Limited Risk (chatbots, AI content) / ✅ Minimal Risk (recommendations) | Aug 2, 2026 | Implement Article 50 disclosures NOW |
| Any Industry | Customer-facing chatbots, AI-generated content for EU audiences, generative AI output tools | 🟡 Limited Risk — Article 50 | Aug 2, 2026 | ✅ Immediate action required |
💰 8. EU AI Act Penalties — What Non-Compliance Costs
The EU AI Act’s penalty structure is tiered by violation type and is among the most significant regulatory financial risks in AI governance — exceeding the maximum penalty under GDPR in its top tier. Enforcement is carried out by national market surveillance authorities designated by each EU member state, with the EU AI Office holding exclusive competence over GPAI providers. As of August 2, 2026, the EU AI Office’s enforcement powers are fully active for GPAI violations. For high-risk and other AI system violations, national authorities are building enforcement capacity, with formal cases expected to accelerate through 2027.
Penalties are calculated as the greater of a fixed maximum or a percentage of global annual turnover — meaning for large multinational organizations, the percentage-based calculation typically produces the larger number. The Act includes proportionality provisions for SMEs, with national authorities instructed to take company size, market position, and the nature of the infringement into account. However, these provisions do not eliminate SME obligations — they affect how penalties are calibrated, not whether they apply.
Penalty benchmark: The EU AI Act’s 7% of global turnover maximum for prohibited AI practices exceeds GDPR’s 4% maximum. For a company with €10 billion in global revenue, a Tier 1 violation carries a maximum penalty of €700 million. For compliance teams making the business case for AI Act investment, this number is the starting point.
| Violation Type | Maximum Fixed Fine | % of Turnover | Who Enforces | Active From |
|---|---|---|---|---|
| Prohibited AI practices (Article 5 violations) | €35,000,000 | 7% of global annual turnover | National market surveillance authorities | 🔴 Feb 2025 |
| High-risk AI system obligation violations | €15,000,000 | 3% of global annual turnover | National market surveillance authorities | Dec 2, 2027 |
| GPAI model obligation violations | €15,000,000 | 3% of global annual turnover | EU AI Office (exclusive competence) | 🔴 Aug 2026 |
| Article 50 transparency violations (chatbots, AI content labeling) | €15,000,000 | 3% of global annual turnover | National market surveillance authorities | 🔴 Aug 2026 |
| Incorrect or misleading information to authorities | €7,500,000 | 1% of global annual turnover | National authorities / EU AI Office | Aug 2, 2026 |
| SME / startup — all violation types | Lower limit of range | Proportionality provisions apply | Same authorities as above | Per tier above |
Note: The AI Act also introduces a multi-reporting obligation that intersects with other EU regulations. Organizations experiencing an AI-related incident may face reporting obligations across three separate timeframes: 24 hours under NIS2, 72 hours under GDPR, and 15 days under the AI Act. Organizations should integrate their AI incident response procedures across all three frameworks. See our AI Incident Response guide for a practical framework.
🔗 9. EU AI Act and Other Regulations — How They Interact
The EU AI Act does not operate in isolation. For most organizations, EU AI Act compliance will intersect with existing GDPR obligations, sector-specific regulations, and international frameworks like ISO/IEC 42001 and the NIST AI RMF. The most important principle: these frameworks are additive, not exclusive. Compliance with one does not substitute for compliance with another. The compliance program must address all applicable frameworks concurrently, ideally through an integrated governance structure rather than separate workstreams.
The GDPR-AI Act intersection is the most immediately consequential for most organizations. GDPR and the EU AI Act apply concurrently to any AI system that processes personal data about EU individuals. Data minimization principles under GDPR affect how AI training data can be gathered and retained. The GDPR right to explanation for automated decisions overlaps with, but is distinct from, the AI Act’s transparency requirements. GDPR Data Protection Impact Assessments (DPIAs) must now incorporate AI Act risk assessments. The Act itself explicitly states it does not replace GDPR — both apply. DPAs retain full jurisdiction over personal data processing aspects of AI systems alongside market surveillance authorities enforcing the AI Act.
For US-based organizations operating in EU markets, the intersection with domestic frameworks requires coordination. The NIST AI Risk Management Framework (NIST AI 100-1, AI RMF 1.0) remains current as of October 2026, providing a widely adopted governance architecture, but it does not satisfy EU AI Act-specific requirements. Organizations must supplement NIST with EU-specific classification analysis and market registration. In the US states, Colorado SB 26-189 (signed May 14, 2026) becomes effective on January 1, 2027, introducing high-risk obligations similar to the EU’s “access to essential services” tier. Connecticut PA 26-15 (effective October 1, 2026) and Illinois HB 3773 (in force January 1, 2026) have established specific AI transparency and employment disclosure rules that must be mapped against the EU AI Act’s Article 50 requirements.
| Regulation / Framework | Overlap with EU AI Act | Gap / Additional Requirement | Who It Affects |
|---|---|---|---|
| GDPR | Data governance; transparency; automated decision rights | AI Act adds conformity assessment, risk management documentation, human oversight requirements not in GDPR | All organizations processing EU personal data using AI |
| ISO/IEC 42001:2023 | AI management system framework; risk management; governance | ISO 42001 does not satisfy Annex III conformity assessment; CE marking; EU AI database registration — supplementation required | Organizations using ISO 42001 as primary AI governance standard |
| NIST AI RMF 1.0 (AI 100-1) | Risk identification, assessment, governance; alignment to GOVERN/MAP/MEASURE/MANAGE | No Annex III classification equivalent; no EU-specific conformity assessment or registration requirement | US organizations with EU market exposure |
| Colorado SB 26-189 (Jan 2027) | High-risk AI obligations in employment, healthcare, housing, lending | Colorado uses “consequential decision” trigger vs EU’s Annex III category list — different scope analysis required | Organizations with US Colorado operations + EU market exposure |
| Connecticut PA 26-15 (Oct 2026) | AI transparency and disclosure requirements; state-level accountability | Scope focuses on state agency use and state residents’ rights; overlaps with Article 50 transparency duties | Organizations with Connecticut workforce or state exposure + EU markets |
| US Federal SR 26-2 (Apr 2026) | AI/ML model risk management in banking | SR 26-2 covers model validation; EU AI Act adds conformity assessment and market registration not present in SR 26-2 | US banks with EU operations using AI in credit/risk |
Organizations certified to ISO/IEC 42001:2023 have a strong foundation for EU AI Act compliance — the management system structure, risk management processes, and governance documentation required by ISO 42001 directly support the Act’s obligations. However, ISO 42001 certification alone does not satisfy EU AI Act conformity assessment requirements. The gap areas — CE marking, EU AI database registration, and the specific Annex III classification analysis — must be addressed explicitly alongside any ISO 42001 program.
📋 10. EU AI Act Compliance Checklist — What to Do Right Now
The most common question from compliance teams in October 2026 is not “what does the EU AI Act require” — it is “where do we start?” The answer is always the same: start with your AI system inventory. You cannot classify what you have not identified, you cannot assess risk for systems you do not know exist, and you cannot build governance for a scope you have not defined. The AI system inventory is the foundation of every other EU AI Act compliance activity.
Start with your HR AI systems. CV screening, interview tools, and performance management AI are explicitly listed in Annex III — and are deployed by more organizations than any other high-risk category. If you have not classified your HR AI systems against Annex III, that is your immediate first step. This review should be completed in the next 30 days.
The master compliance checklist below is structured to be actionable immediately. Use it as a working document — assign owners, set target dates, and track status. For a broader audit framework, see The AI Audit Checklist and our AI Model Risk Management framework. For human oversight implementation guidance, see our Human-in-the-Loop guide.
| # | Requirement | Your Role | Evidence Needed | Priority / Deadline |
|---|---|---|---|---|
| 1 | Complete AI system inventory — all AI tools, models, and automated decision systems in use | All organizations | Inventory register; system descriptions; vendor names | 🔴 Immediate — do this week |
| 2 | Identify which systems process data about people in the EU or affect EU residents | All organizations | Scope determination document; data flow mapping | 🔴 Immediate |
| 3 | Apply Article 50 disclosure requirements to all chatbots and AI-content tools deployed to EU users | Deployer | Interface disclosure text; implementation evidence | 🔴 ACTIVE NOW |
| 4 | Check all AI-generated content for EU audiences — implement labeling and machine-readable markers | Deployer / Content publisher | Content labeling evidence; marking implementation | 🔴 By Dec 2, 2026 (existing systems) |
| 5 | Confirm no AI systems in use violate Article 5 prohibited practices | All organizations | Legal review sign-off; prohibited practice clearance | 🔴 NOW — enforced since Feb 2025 |
| 6 | Apply Annex III risk classification to each AI system in inventory — flag all potential high-risk systems | All organizations | Classification assessment document per system | 🟠 Within 30 days |
| 7 | Confirm role for each in-scope system: are you a provider, deployer, or both? | All organizations | Role determination memo per system; legal sign-off | 🟠 Within 30 days |
| 8 | Engage legal counsel for high-risk system determinations — especially HR, credit, biometric, healthcare | All organizations | Legal engagement confirmation; scope memo | 🟠 Within 60 days |
| 9 | Obtain GPAI compliance documentation from AI model providers | Deployer | Vendor compliance documentation; GPAI Code of Practice status | 🟠 Q4 2026 |
| 10 | Build AI system risk management program for high-risk systems (Article 9) | Provider / Deployer | Risk policy; risk register; review schedule | 🟡 Q1 2027 |
| 11 | Conduct data governance assessment (Article 10) | Provider | Data quality assessment; bias evaluation; policy | 🟡 Q1 2027 |
| 12 | Prepare Annex IV technical documentation (Article 11) | Provider | Technical documentation bundle; version records | 🟡 Q2 2027 |
| 13 | Implement automatic logging / audit trail (Article 12) | Provider / Deployer | Log samples; retention policy; audit trail test | 🟡 Q2 2027 |
| 14 | Build and test human oversight mechanism (Article 14) | Provider / Deployer | Override mechanism test records; training evidence | 🟡 Q2 2027 |
| 15 | Complete accuracy, robustness, and cybersecurity assessment (Article 15) | Provider | Performance benchmarks; penetration test report | 🟡 Q2 2027 |
| 16 | Initiate conformity assessment | Provider | Assessment report; notified body engagement | 🟡 Q3 2027 |
| 17 | Prepare Declaration of Conformity and CE marking | Provider | Signed Declaration; CE marking documentation | 🟡 Q3 2027 |
| 18 | Register in EU AI database | Provider | EU AI database registration confirmation | 🔴 Before Dec 2, 2027 deployment |
| 19 | Deliver AI literacy training per Article 4 | Deployer | Training records; completion rates; curriculum | 🔴 NOW — Feb 2025 active |
| 20 | Align GDPR DPIA process with AI Act risk assessment | All organizations | Updated DPIA documents; integrated review log | 🟠 Q4 2026 |
| 21 | Identify national market surveillance authority | All organizations | Authority identification doc; contact log | 🟡 Q1 2027 |
| 22 | Build AI incident response plan | All organizations | Incident plan; reporting workflow; exercise records | 🟠 Q4 2026 |
❓ 11. EU AI Act — Questions Compliance Teams Are Asking
Does the EU AI Act apply to companies outside the EU? Yes — the EU AI Act has extraterritorial reach similar to the GDPR. It applies to providers who place AI systems on the EU market, deployers who operate AI systems within the EU, and third-country organizations whose AI system outputs are used in the EU. Non-EU companies that supply AI tools used by EU businesses, or deploy AI that affects EU residents, are in scope regardless of where the company is headquartered.
The high-risk provisions were supposed to apply in August 2026 — what actually happened? The Digital Omnibus on AI (Regulation (EU) 2026/1744) entered into force on July 27, 2026, six days before the original August 2 high-risk deadline. It deferred standalone high-risk Annex III obligations to December 2, 2027. Article 50 transparency obligations and GPAI enforcement powers were not deferred — they took effect on August 2, 2026, as originally scheduled. Any compliance guide or article stating that “high-risk provisions are now active” as of August 2, 2026, without acknowledging the deferral is inaccurate and should be treated with caution.
What is the difference between a provider and a deployer? A provider is an organization that develops an AI system and places it on the market. A deployer is an organization that uses an AI system in a professional context. The same AI system can have one provider and many deployers. If you build and sell an HR screening tool, you are the provider. If you purchase that tool and use it to screen job applicants, you are the deployer. Both carry obligations — but different ones. Crucially: if you substantially modify an AI system or adapt it to a high-risk use case, you become the provider for that deployment.
Does using ChatGPT or Claude make my organization a GPAI provider? No. Using a GPAI model via API or subscription makes you a deployer. The provider is Anthropic (Claude), OpenAI (ChatGPT), or Google (Gemini). Providers carry GPAI compliance obligations. However, if you deploy those models in an Annex III high-risk use case — for example, using Claude to screen job applications — you become a high-risk AI system deployer and inherit deployer-level obligations under the Act.
Do small businesses need to comply? Yes — the EU AI Act applies to all organizations regardless of size, including SMEs and startups. However, the Act includes proportionality provisions that affect how penalties are calibrated for smaller organizations, and some national authorities are expected to prioritize larger-scale deployments in initial enforcement. The compliance obligations themselves — particularly prohibited practices and Article 50 transparency — apply from day one regardless of company size.
🔒 12. RAG Pipelines and the EU AI Act — A Regulated Privacy Surface
Retrieval-Augmented Generation (RAG) architectures have become the standard for enterprise AI deployment in 2026, but their compliance status is frequently misunderstood. RAG systems are not exempt from EU AI Act obligations. In fact, because RAG systems process personal data at inference time to augment model prompts, they represent a significant regulated privacy surface under GDPR Article 5. For organizations deploying RAG-augmented systems in high-risk sectors like recruitment, credit, or healthcare, the retrieval pipeline is as legally consequential as the foundation model itself.
The primary compliance requirement for RAG pipelines is data minimisation at the retrieval layer. Under GDPR Article 5, any AI system processing EU personal data must only retrieve the minimum information necessary for the specific task. This means a RAG system that retrieves full documents when only a single paragraph is required may be in violation of GDPR. Furthermore, Article 10 of the EU AI Act requires stringent training and operational data governance for high-risk systems. When a RAG system provides the operational context for a high-risk decision (such as an AI assistant summarizing a patient’s medical history for a triage decision), that RAG pipeline must be documented, bias-assessed, and subject to technical measures that prevent unauthorized data retrieval across user contexts.
Practical implementation requires applying federated access controls at the retrieval layer rather than relying solely on source-system permissions. Organizations must implement audit logging of all retrieval activity to satisfy Article 12 (Record Keeping) and Article 13 (Transparency) obligations. If you are a deployer of a RAG-augmented AI system in a high-risk context, your conformity assessment and Fundamental Rights Impact Assessment (FRIA) must specifically cover the retrieval pipeline, the indexing strategy, and the data minimisation controls applied at inference time. For a full technical explanation of how RAG systems work and how to secure the retrieval pipeline, see our guide to Retrieval-Augmented Generation (RAG) Explained.
| RAG Component | EU AI Act Obligation | GDPR Obligation | Risk if Ignored |
|---|---|---|---|
| Retrieval layer | Article 10 data governance (high-risk) | Article 5 data minimisation | Over-retrieval of personal data = Article 5 violation |
| Access controls | Article 25 Privacy by Design | Article 25 GDPR (PbD) | Unauthorised retrieval across user contexts |
| Audit logging | Article 12/13 transparency doc | Article 5(1)(f) integrity | No evidence trail for regulator investigation |
| Personal data in index | FRIA requirement (high-risk) | DPIA required | Dual compliance gap (AI Act + GDPR) |
🏁 13. Conclusion — EU AI Act Compliance Is an 18-Month Sprint
The Digital Omnibus deferral has given organizations breathing room on the most demanding high-risk obligations. But it has not reduced the compliance burden or the strategic urgency. The window between late 2026 and December 2027 is for building genuinely complex compliance structures: AI system inventory, Annex III risk classification, Article 9 risk management systems, Article 14 human oversight mechanisms, and full technical documentation. None of these tasks can be completed in the final weeks before the deadline. Organizations that treat December 2027 as a distant horizon are setting themselves up for a compressed, expensive, high-risk sprint in Q4 2027.
For organizations with chatbots, AI-generated content tools, or generative AI deployed to EU audiences, there is no deferral. Article 50 transparency obligations are active now. Every customer-facing chatbot in the EU must disclose it is AI. Every piece of AI-generated content published for public consumption must carry machine-readable markers. These are current legal requirements. The EU AI Office’s power to fine GPAI providers is also active. The regulatory framework is not arriving; for a significant portion of AI deployments, it has already arrived. The organizations that move first — that classify their systems and build their governance programs now — will have a meaningful competitive advantage when enforcement accelerates through 2027 and 2028. The 2026 consensus is clear: the preparation window is open, the deadline is fixed, and the work starts today.
📌 Key Takeaways
| ✅ | Takeaway |
|---|---|
| ✅ | The Digital Omnibus (Regulation (EU) 2026/1744) deferred standalone high-risk Annex III obligations to December 2, 2027, but Article 50 transparency duties and GPAI enforcement powers took effect on August 2, 2026. |
| ✅ | Article 50 compliance is active right now — chatbot disclosures, labeling of AI-generated public content, and machine-readable marking are enforceable legal requirements with fines up to €15 million or 3% turnover. |
| ✅ | RAG pipelines represent a critical privacy surface where GDPR Article 5 data minimisation applies at inference time; high-risk RAG deployments require both a DPIA and AI Act technical documentation. |
| ✅ | HR AI systems remain the highest volume high-risk category; organisations deploying CV screening or performance management tools must conduct an Annex III classification review immediately. |
| ✅ | The EU AI Act has extraterritorial reach: if your AI system output is used in the EU or affects EU residents, your organisation is in scope regardless of its headquarters location. |
| ✅ | GPAI providers (foundational model developers) have been subject to binding obligations since August 2025; since August 2026, the EU AI Office has the power to fine non-compliant model providers. |
| ✅ | Prohibited practices (Article 5), such as biometric surveillance and social scoring, have been enforceable since February 2, 2025, and carry the Act’s highest penalties of up to 7% turnover. |
| ✅ | The immediate first step for every organization is a complete AI system inventory; you cannot build a compliance program or manage risk for systems you have not officially identified. |
🔗 Related Articles
- 📖 AI Regulation in 2026: 7 New Laws Reshaping How Businesses Use AI
- 📖 EU AI Act Article 27 FRIA: What It Is and Who Must Comply (2026)
- 📖 DPIA for AI Systems: A Step-by-Step Compliance Guide (2026)
- 📖 AI Governance Explained: How to Build an AI Policy Framework
- 📖 The AI Audit Checklist: How to Prove Your Company Is Compliant in 2026
❓ Frequently Asked Questions: EU AI Act Compliance 2026
1. Does the EU AI Act apply to companies based outside the EU?
Yes. The EU AI Act has extraterritorial reach — it applies to any organization that deploys AI used by EU residents or affecting EU markets, regardless of where the company is headquartered. This is similar to the GDPR’s extraterritorial scope. Learn more in our EU AI Act Compliance Guide.
2. Did high-risk AI provisions actually go live in August 2026?
Not fully. The Digital Omnibus (Regulation (EU) 2026/1744) deferred standalone high-risk Annex III obligations to December 2, 2027. However, Article 50 transparency duties and GPAI enforcement powers did take effect on August 2, 2026, as scheduled. See our full EU AI Act timeline for the accurate compliance calendar.
3. What AI systems are classified as high-risk under Annex III?
Annex III covers AI used in hiring and performance management, credit scoring and insurance underwriting, biometric identification, critical infrastructure, educational admissions and assessment, law enforcement, border control, and the administration of justice. Review our AI Risk Assessment guide for a structured classification approach.
4. What are the maximum penalties for EU AI Act non-compliance?
The highest tier — violations of Article 5 prohibited AI practices — carries fines of up to €35 million or 7% of global annual turnover, whichever is higher. This exceeds the GDPR maximum of 4%. High-risk AI system violations carry up to €15 million or 3% of turnover. The prohibited practices regime has been enforced since February 2025.
5. What is the difference between a provider and a deployer under the EU AI Act?
A provider develops and places an AI system on the market. A deployer uses an AI system in a professional context. If you buy an AI HR screening tool and use it to evaluate job applicants, you are the deployer — and you carry independent compliance obligations including human oversight and record keeping. Our AI Governance framework guide covers how to structure accountability for both roles.
📧 Get the AI Buzz Weekly Digest
Weekly AI insights, tools, and strategies — delivered every Monday. Free.
Leave a Reply